Open-source · MIT · Multi-Node Mesh & V2 Engine
current: jsuzanne/stigix:v2  ·  v2.0.112

An open, customizable & extensible platform
for real SASE / SD-WAN validation

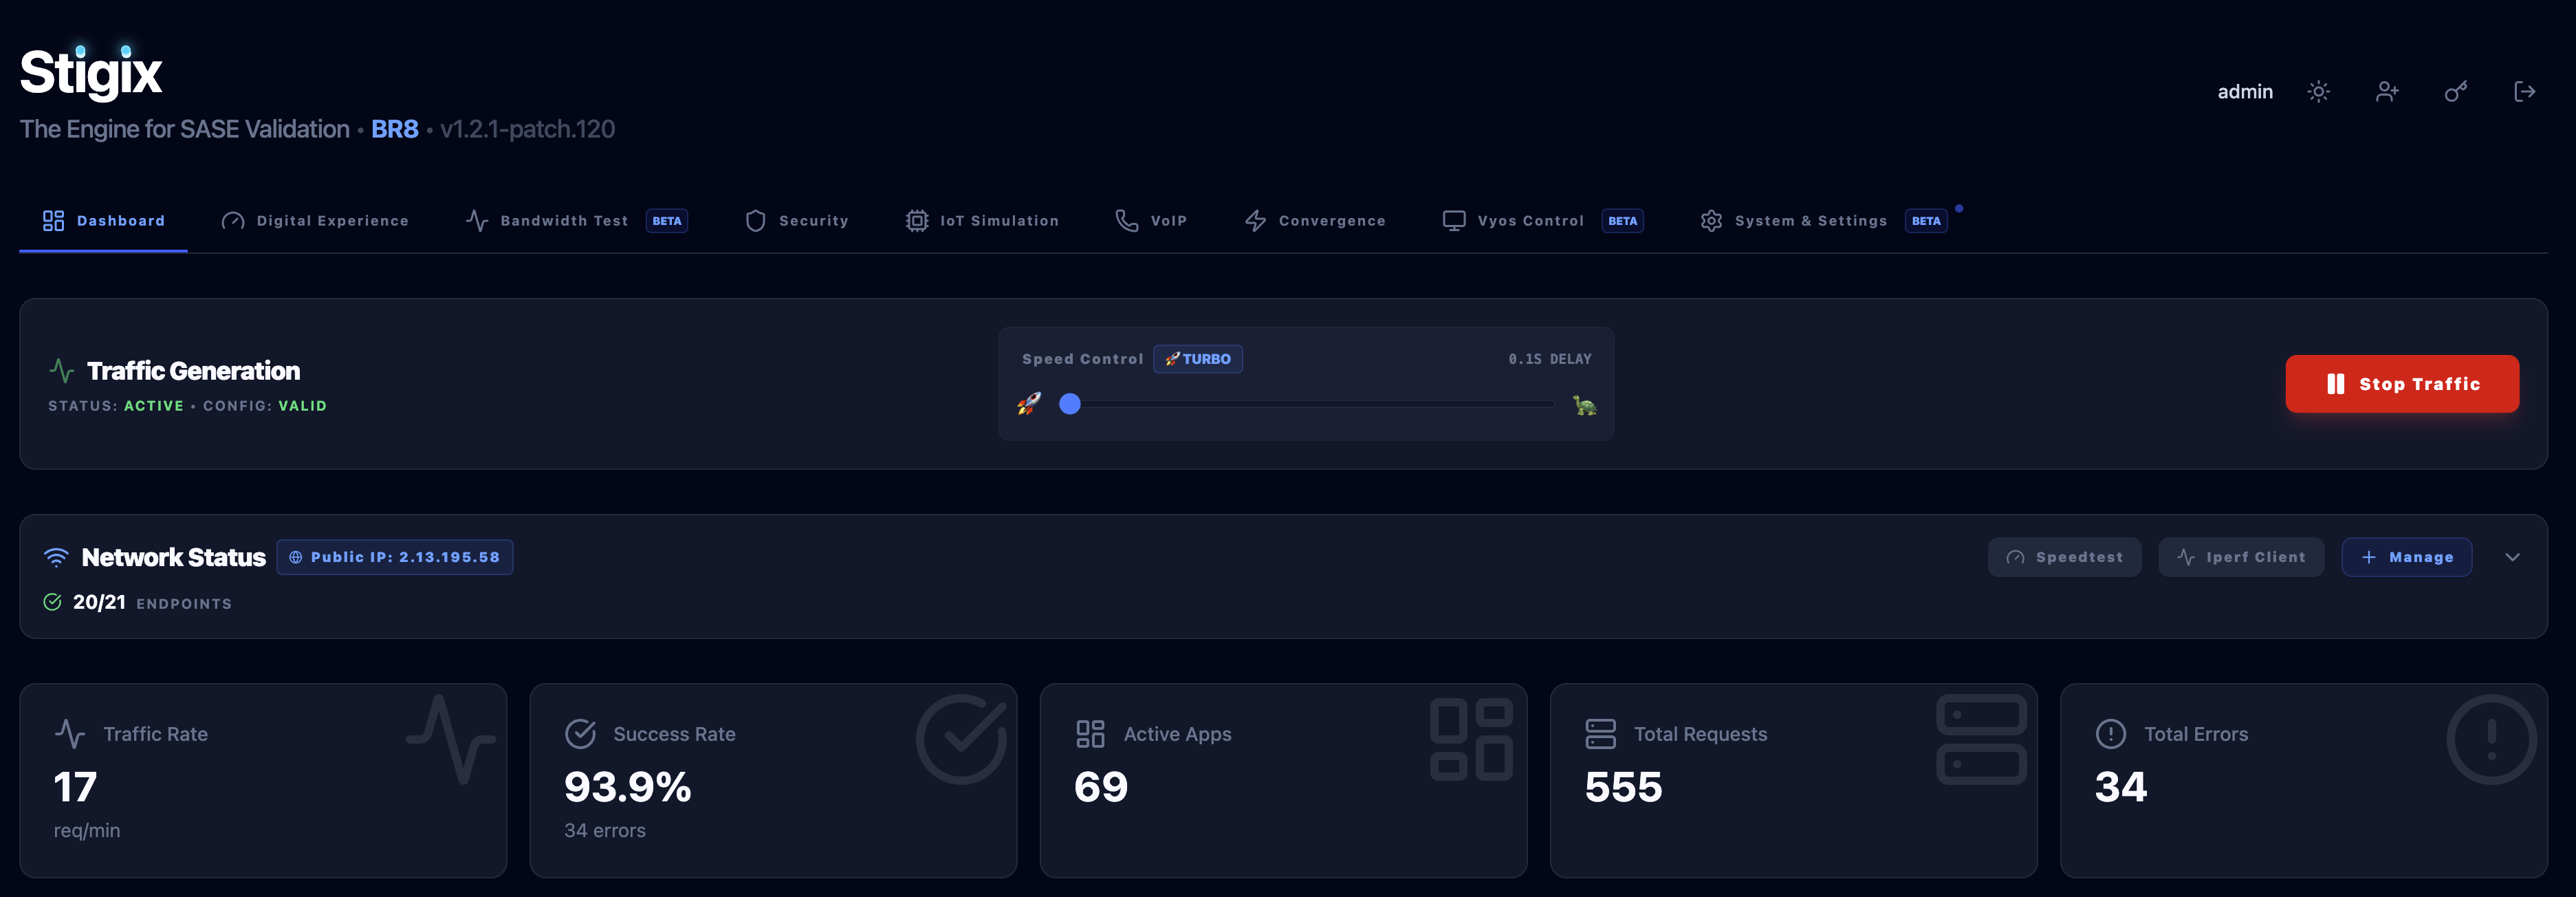
Stigix generates realistic SaaS and East-West custom TCP enterprise traffic, orchestrates zero-touch multi-node mesh provisioning, runs active DEM performance probes, executes automated security tests, measures failover convergence, automates VyOS routers, simulates voice and IoT devices, and visualizes Prisma SD-WAN overlay topology — in labs, demos, and POC environments.

Runs on Docker — AMD64 & ARM64 Zero-Touch Mesh & Central Provisioning Custom TCP East-West & Chaos Engine
Note: This is a personal, community-driven open-source project. It is not an official Palo Alto Networks product and is not supported or endorsed by Palo Alto Networks. All opinions and configurations are the author's own. Use at your own risk.
How It Works

Distributed Multi-Node Architecture

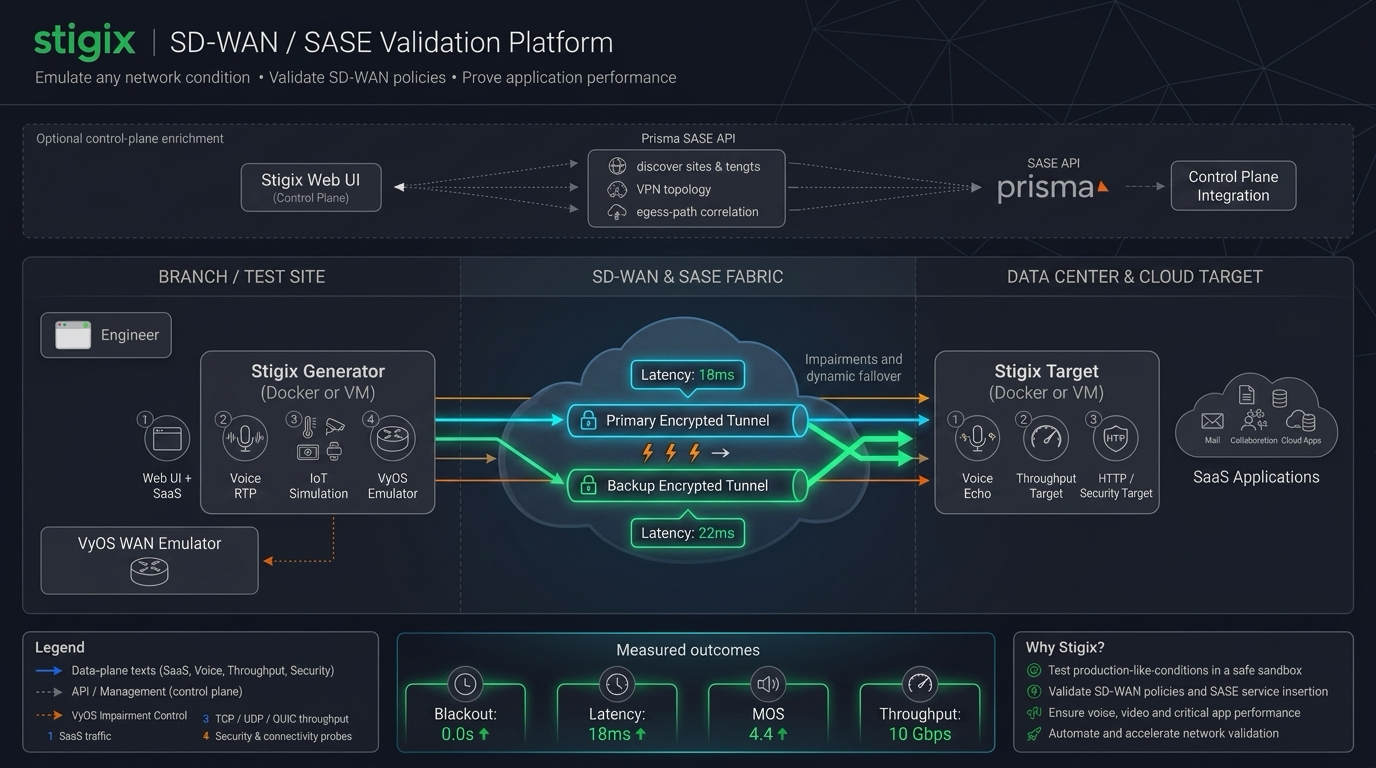
Stigix deploys seamlessly across Datacenters, Branch sites, and Cloud instances. A Leader node orchestrates Central Global Provisioning, while every peer acts concurrently as a traffic sender, custom TCP host listener, and SLA responder.

Stigix SD-WAN / SASE Validation Platform Architecture — Branch Site, SD-WAN & SASE Fabric, Datacenter & Cloud Target
Origin
"I built this after years of writing one-off scripts for SD-WAN POCs and never finding a single lab platform that matched what I see in the field."

The pattern was always the same: a new POC, a new set of one-off scripts to simulate SaaS traffic, test URL filtering, or measure failover convergence. Nothing reusable. Nothing that handled both the traffic side and the security validation side in the same tool.

Stigix was built to change that — a single platform for generating realistic application traffic, running security policy tests, simulating voice and IoT devices, measuring SD-WAN convergence time, and giving you a real-time view of what's happening across the network.

Problems it solves

  • No realistic SaaS & custom line-of-business TCP traffic for SD-WAN path steering
  • No single tool combining URL filtering, DNS security, and threat prevention validation
  • No zero-touch multi-branch lab orchestration with centralized configuration push
  • No precise failover convergence measurement with microsecond timing in a lab
  • IoT and voice simulation requiring custom scripting every time
  • No link between physical router impairments, underlay topology, and traffic observation
  • No zero-config multi-node setup for branch/hub lab scenarios

Platform

Core capabilities

Each capability is independently usable and seamlessly integrated into the unified dashboard, CLI, and central provisioning engine.
Capability
Description
Key specs
Custom TCP Applications V2 NEW
traffic simulation · East-West
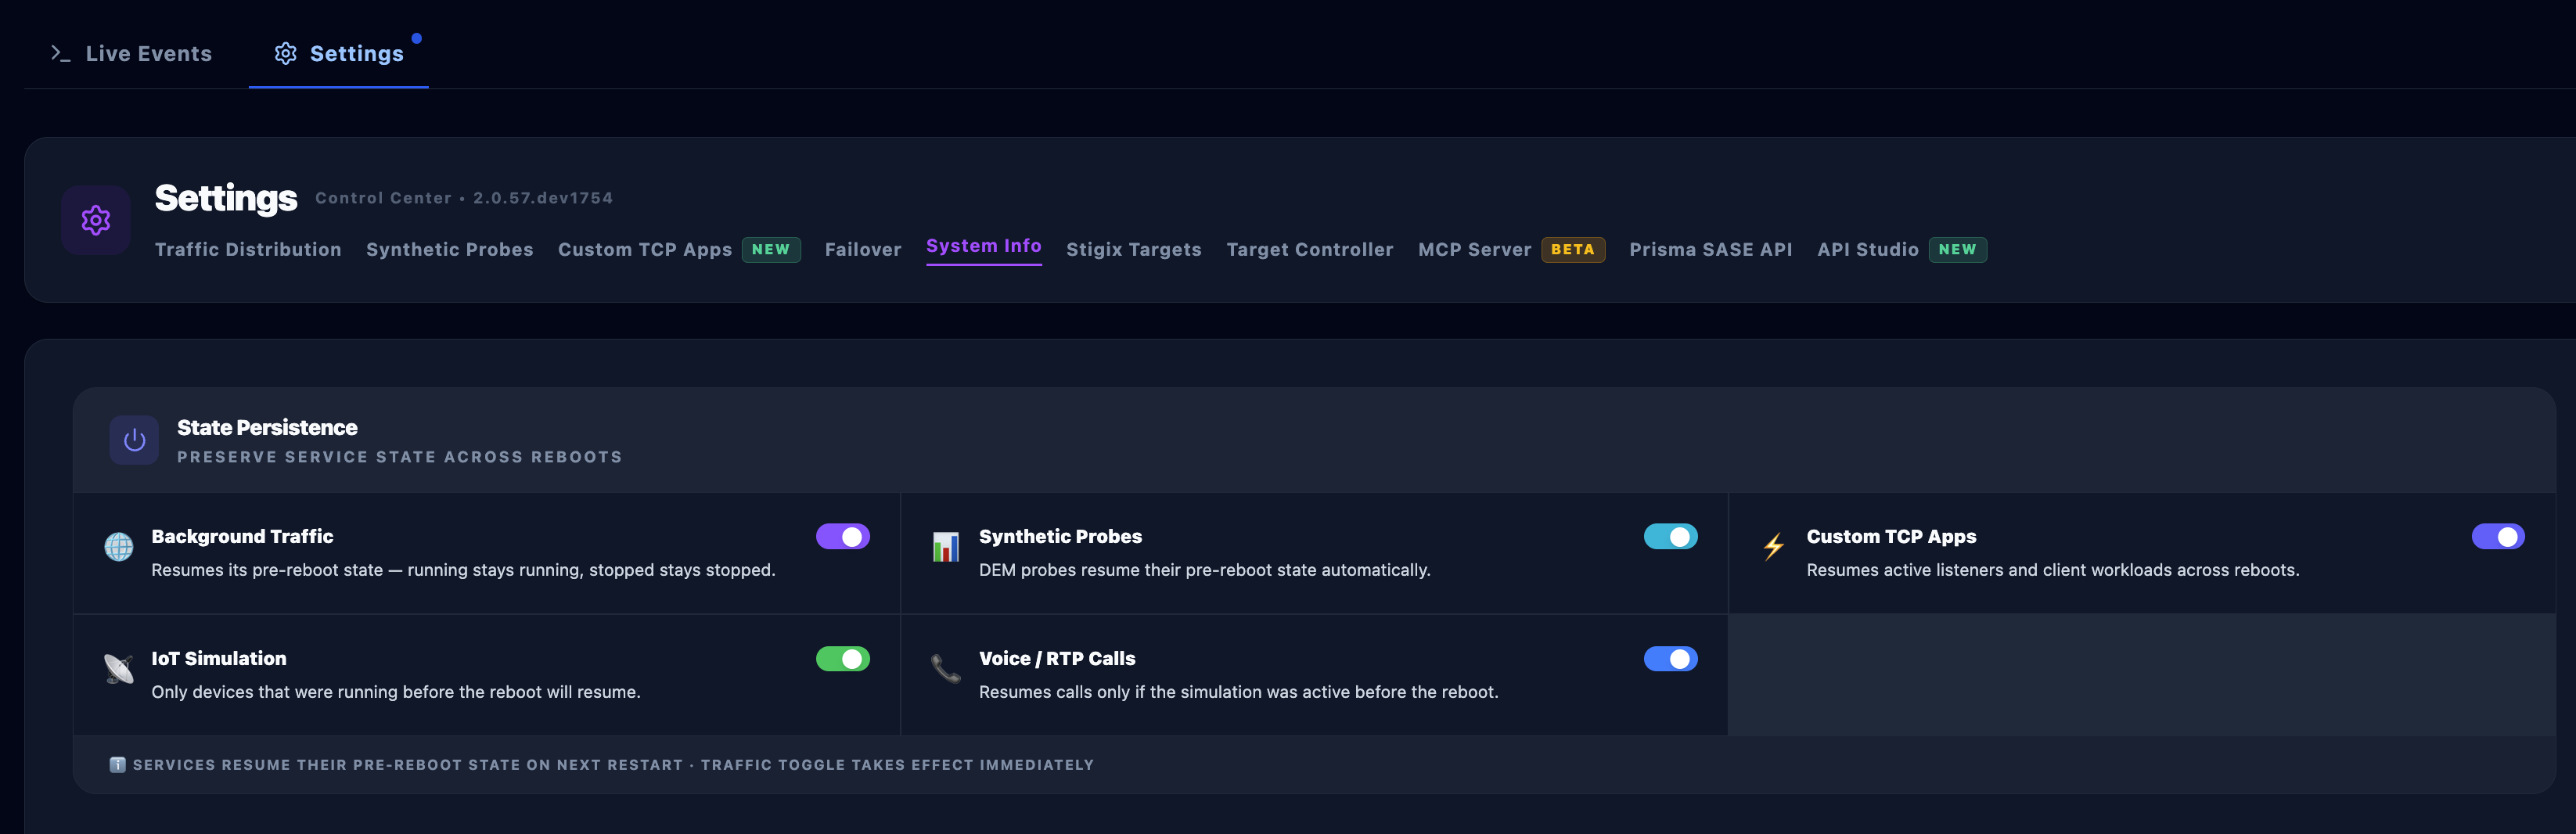
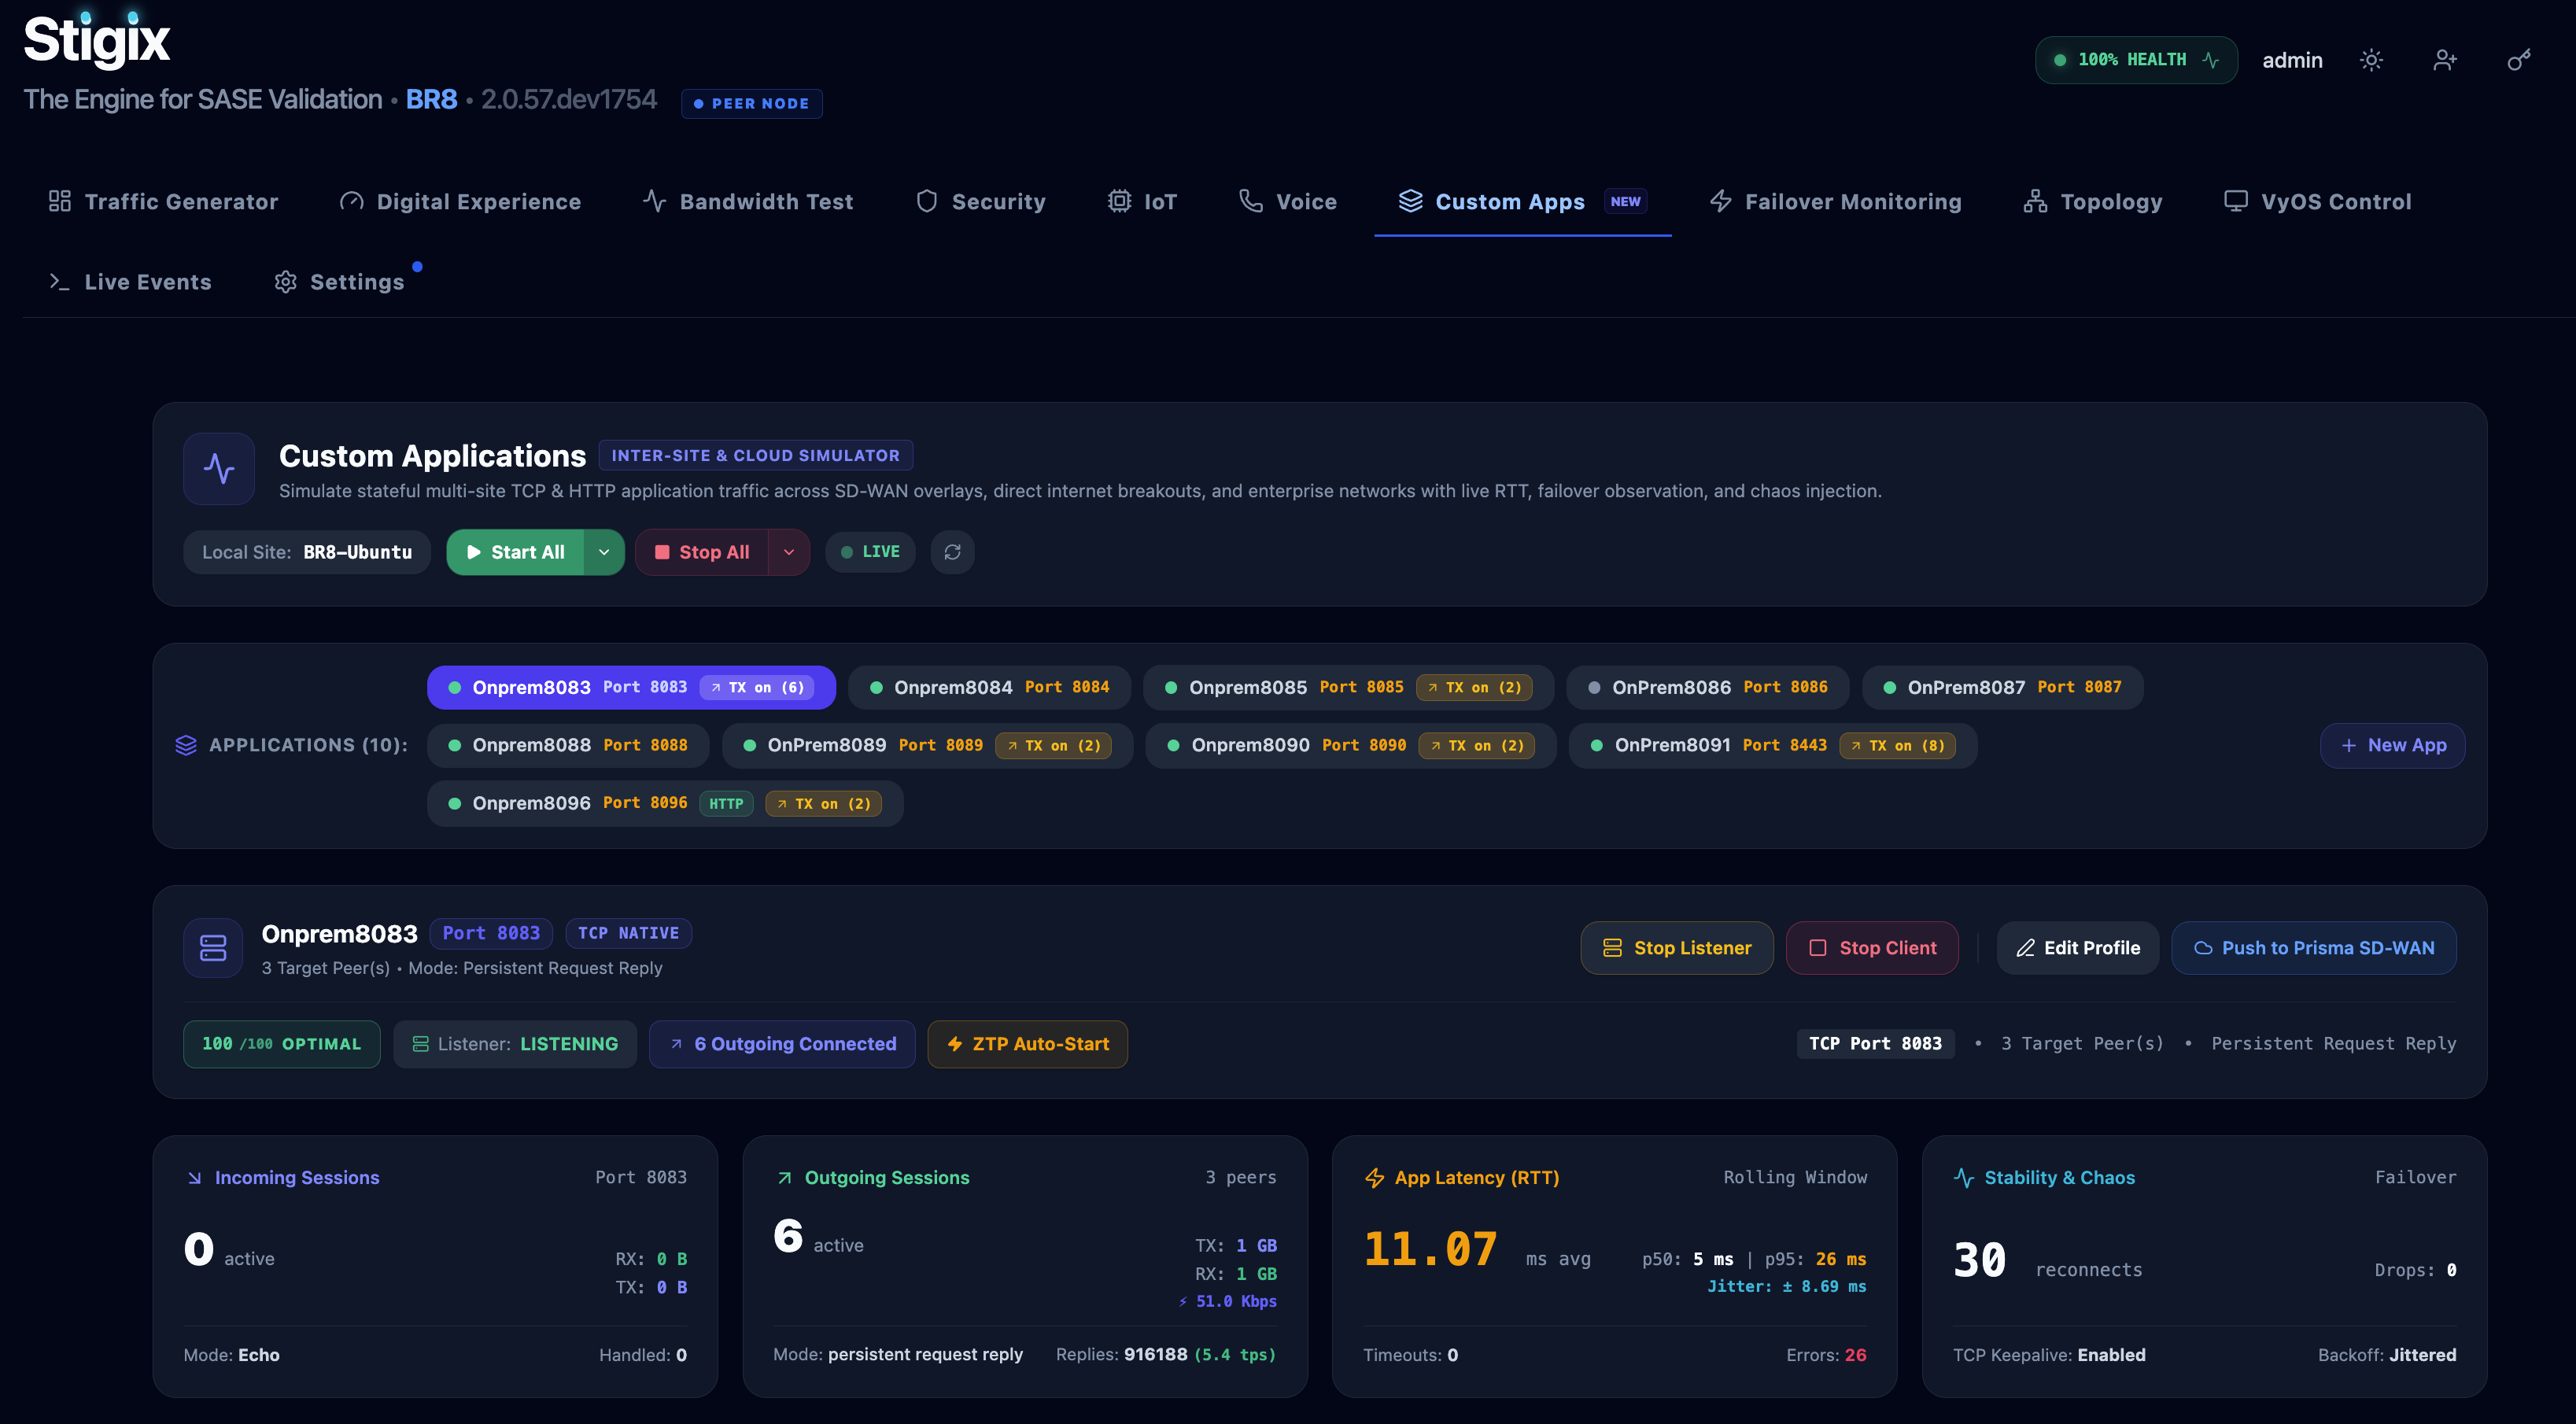
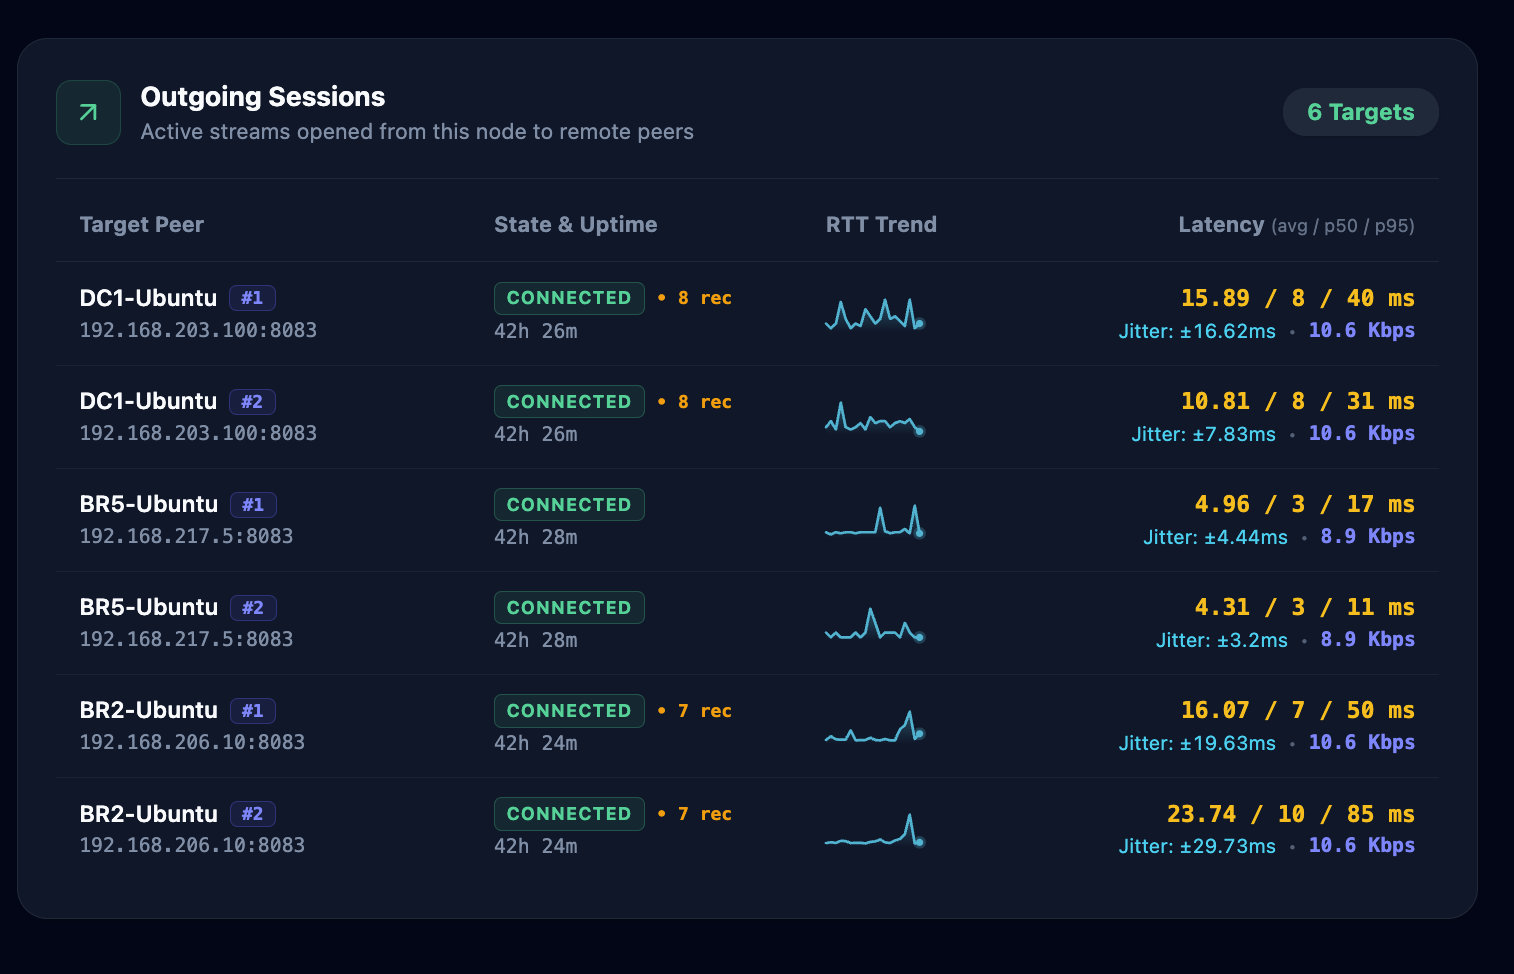
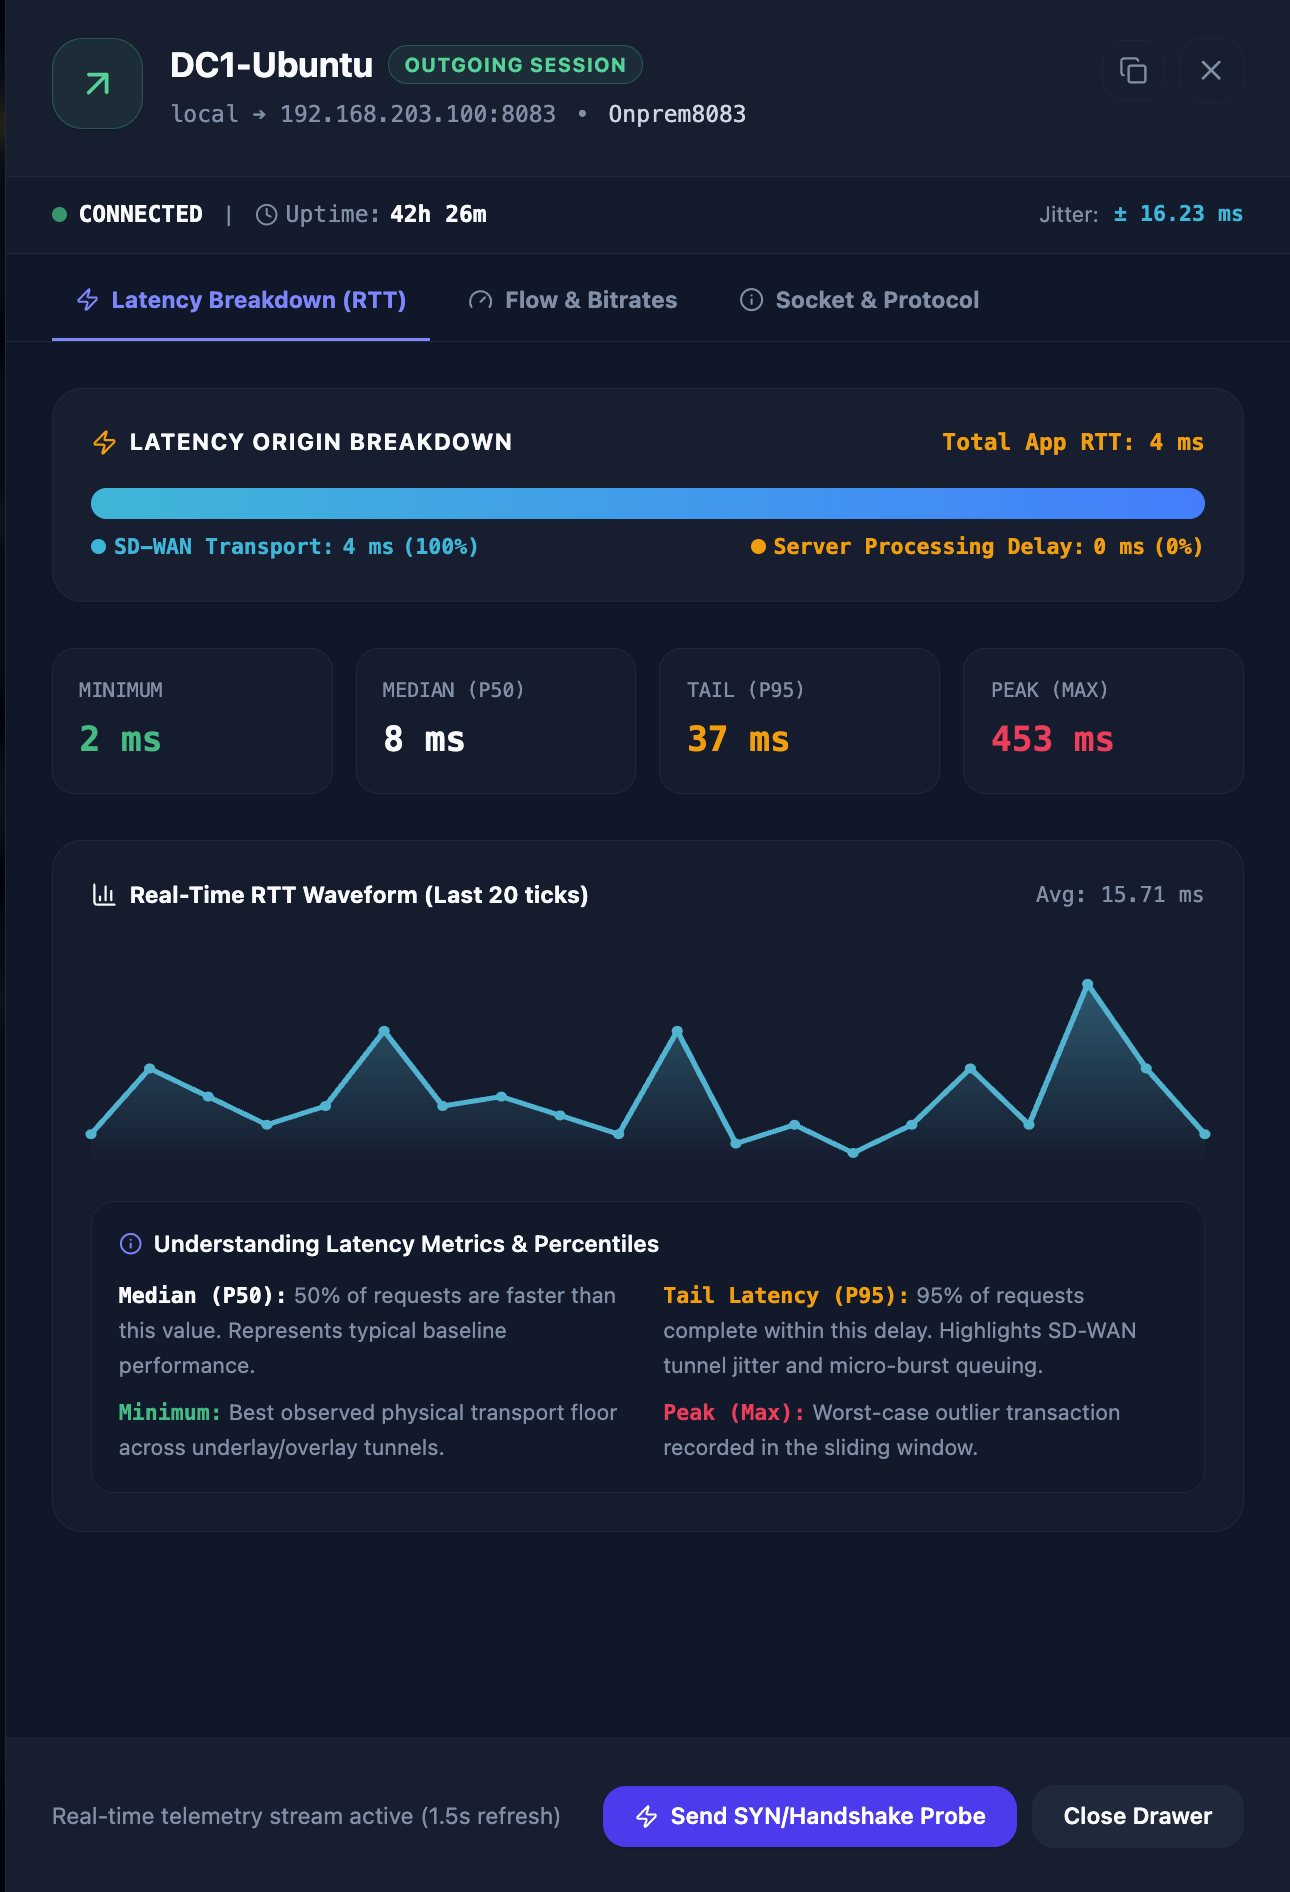
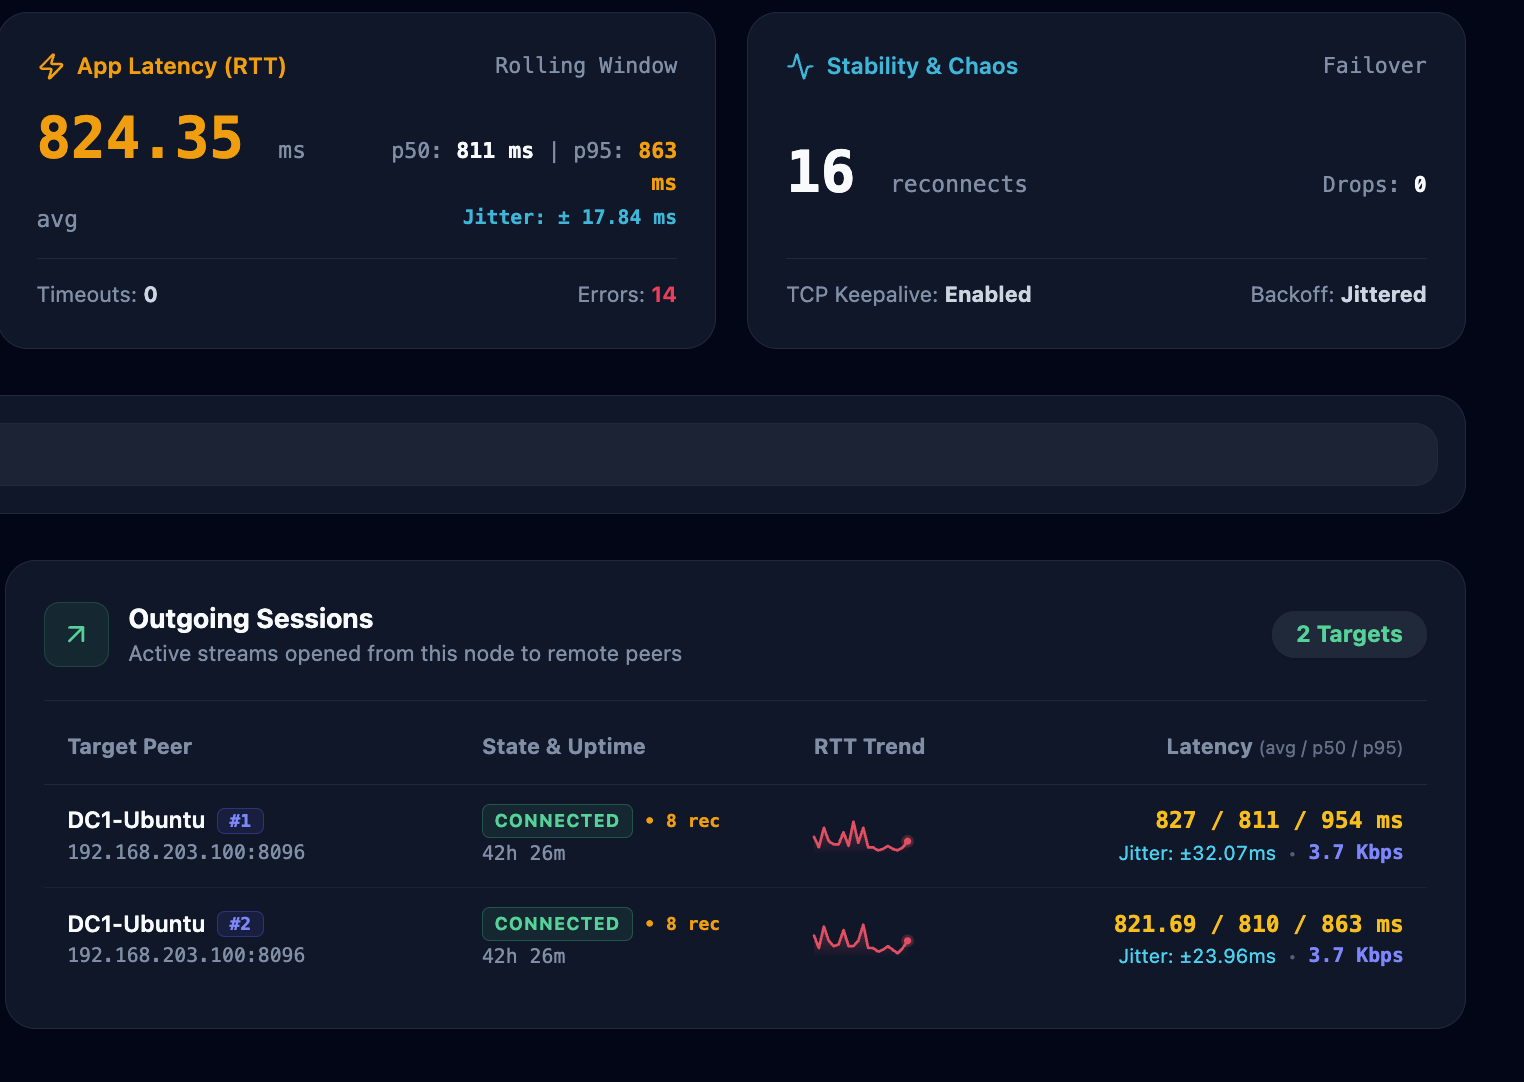
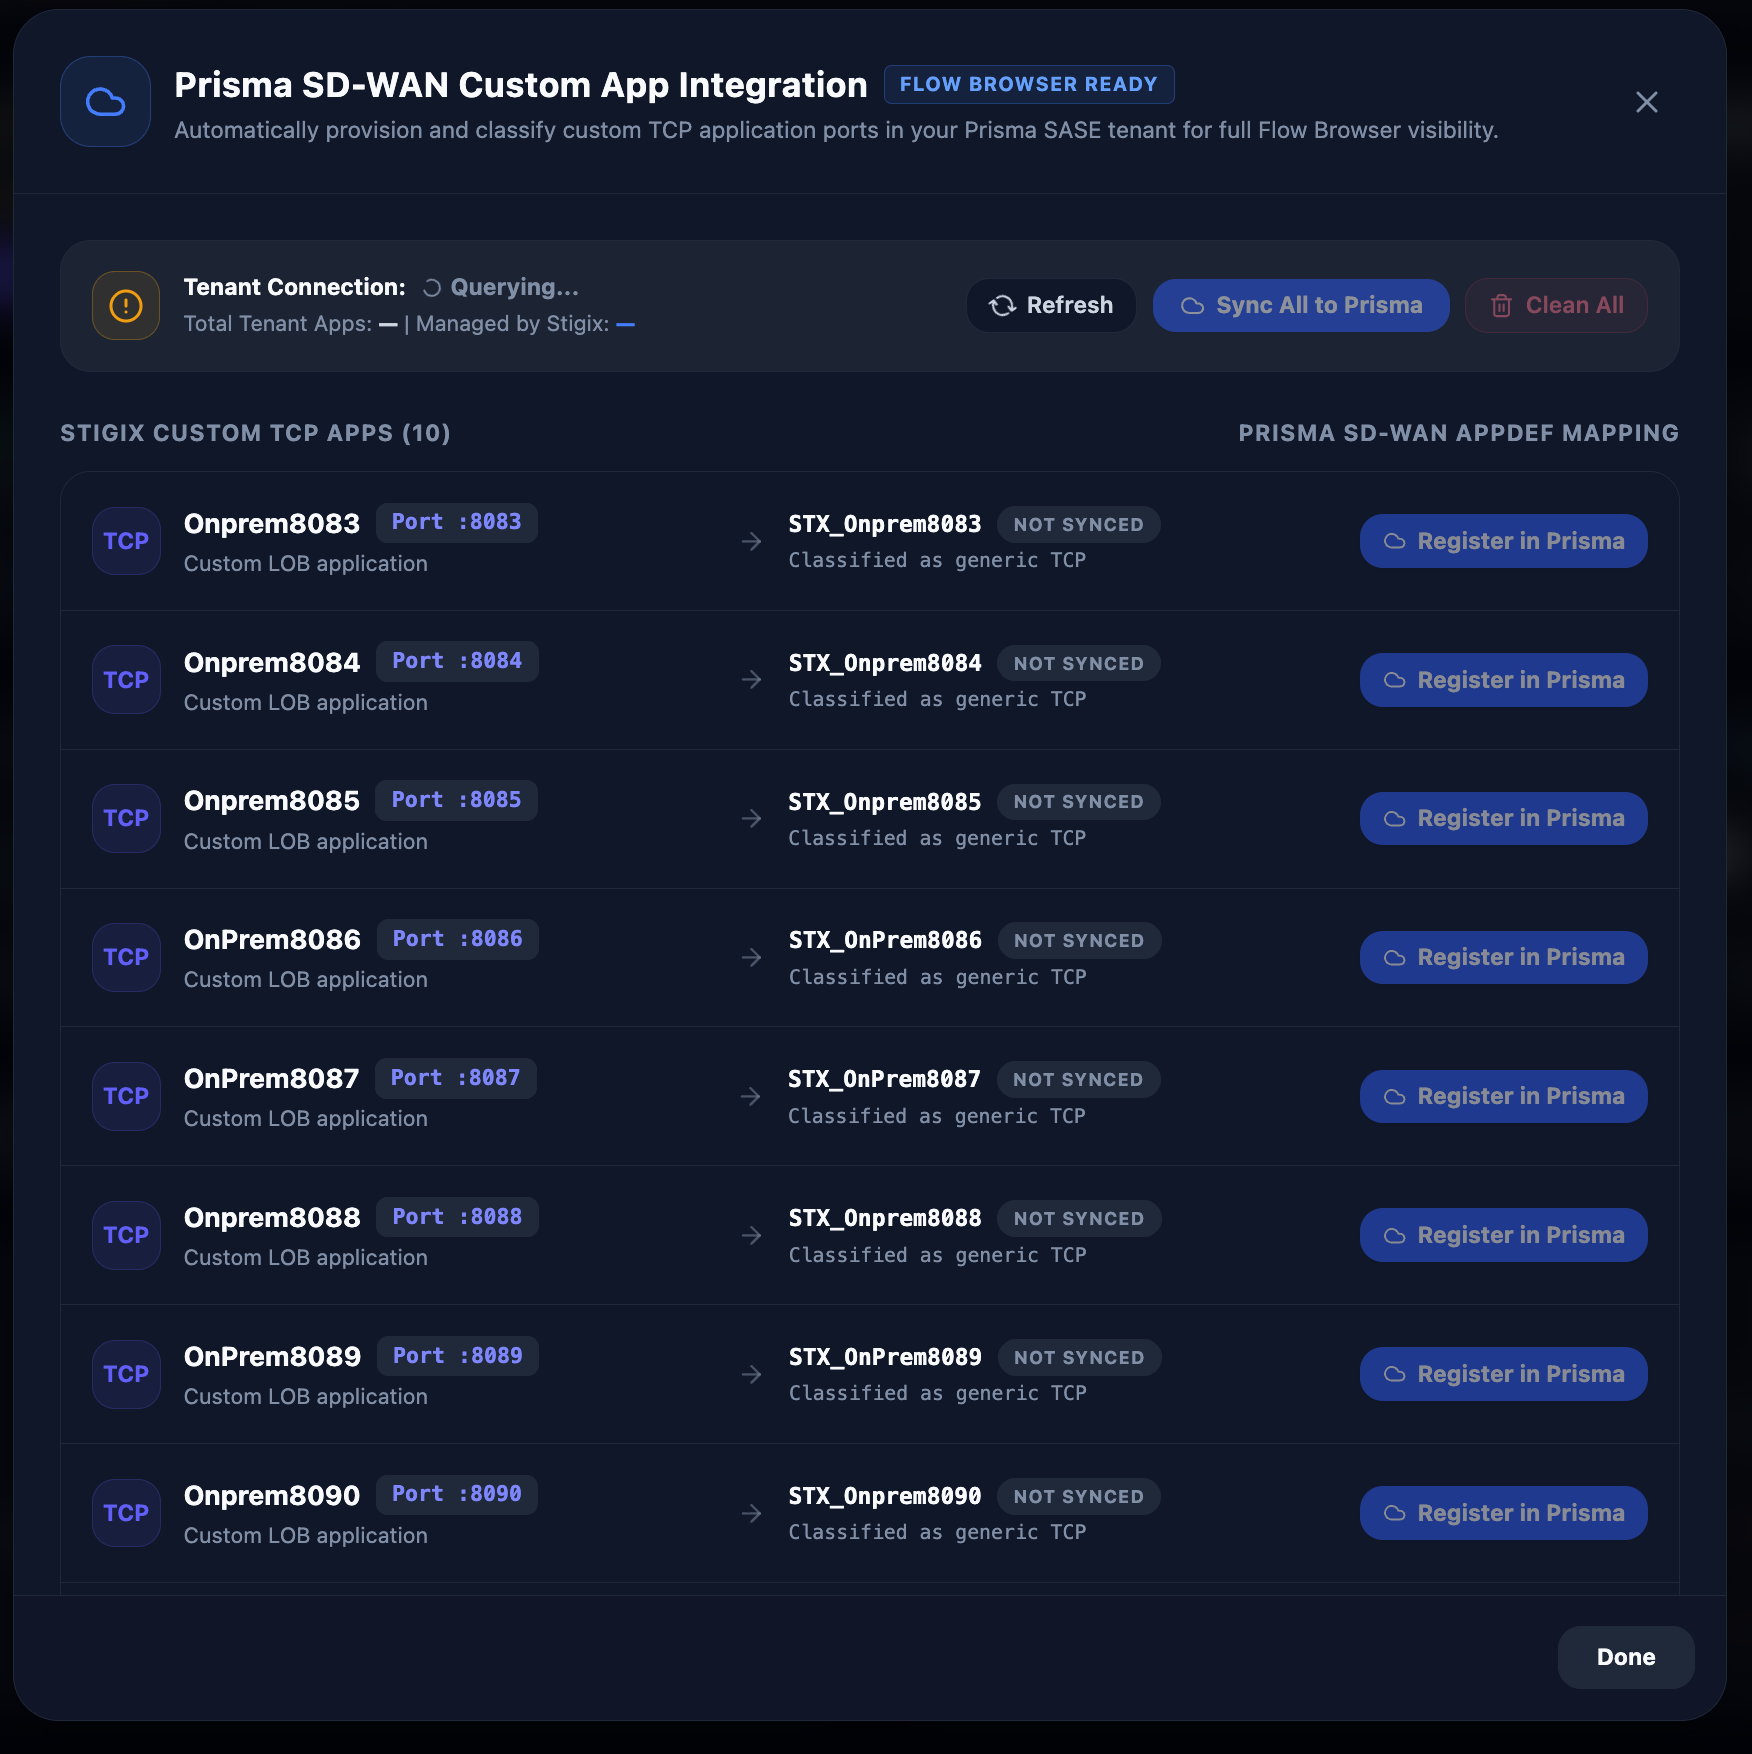
Multi-application East-West workload simulation with dual host TCP listeners and outbound client workload generators. Includes 8 server response simulation modes (Echo, ACK, fixed delay, jittered delay, looping degradation, drop response, connection resets, application error codes), 5 client workload modes, rolling RTT percentiles ($p50/p95/\text{avg}$), state persistence across reboots, and an interactive 4-step wizard with port availability check.
East-West Dual-Role 8 Chaos modes p50/p95 RTT State persistence
Central Global Provisioning V2 NEW
orchestration · multi-node
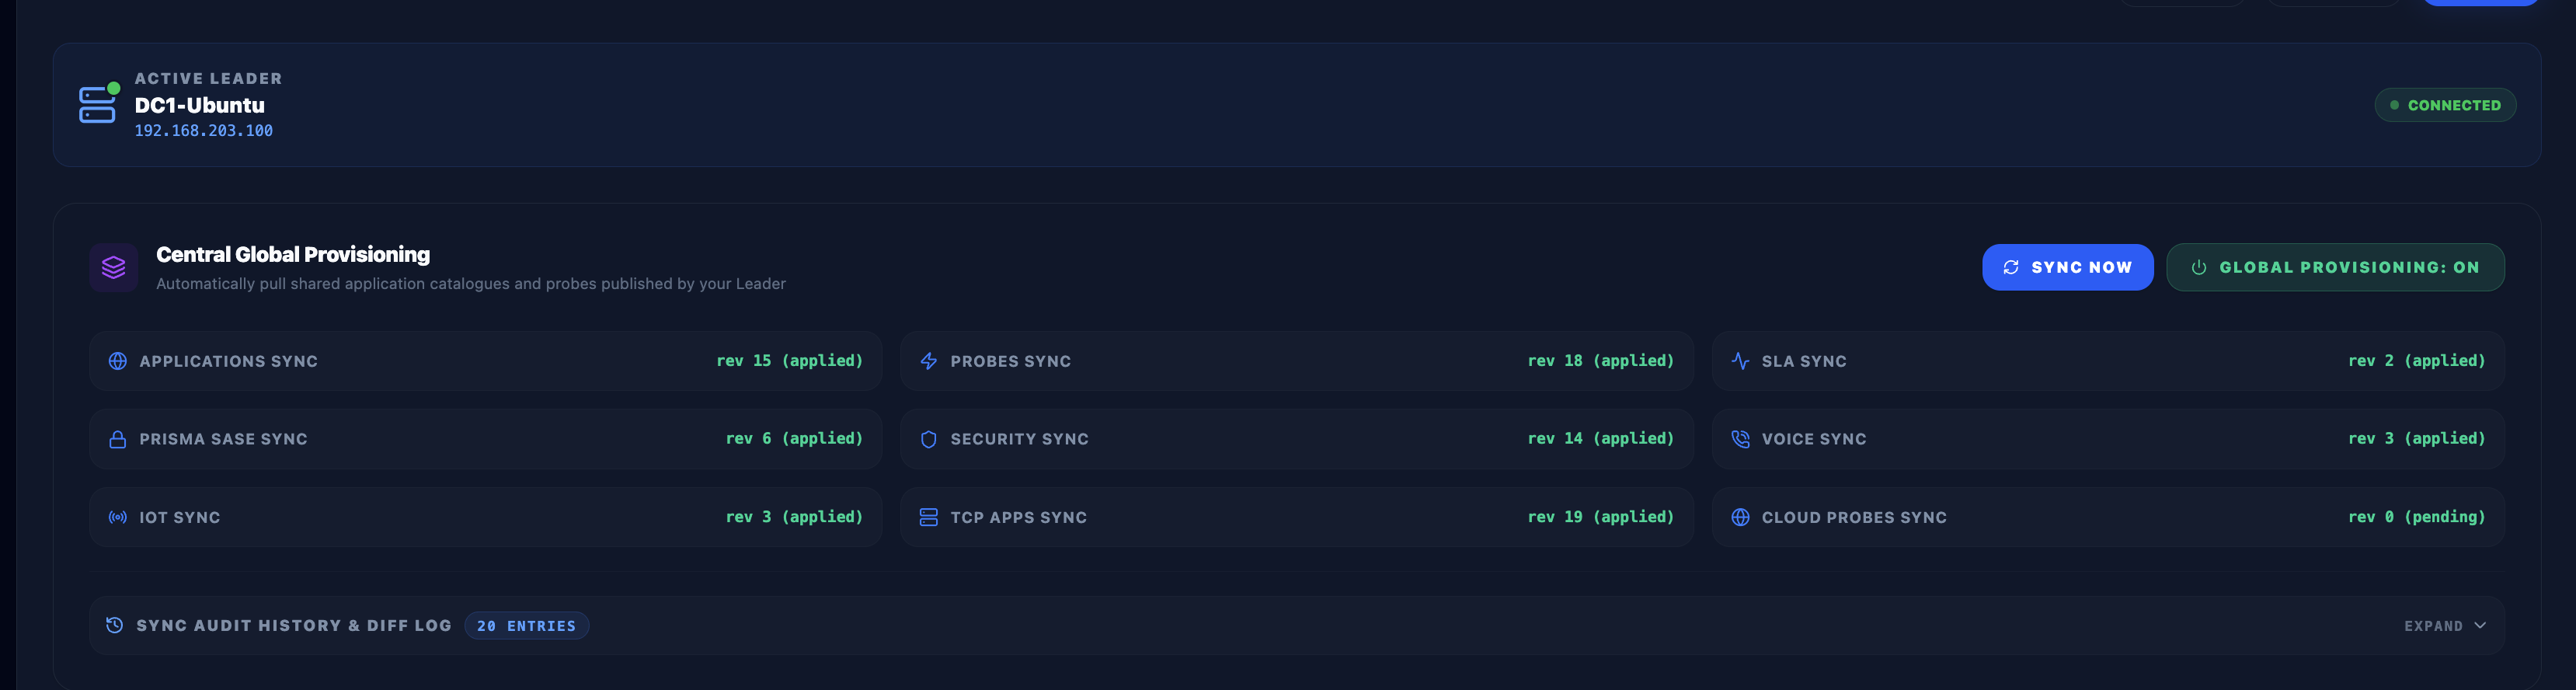
Centralized pull-mode distribution (30s cycle) of 8 configuration bundles (Applications, Synthetic Probes, SLA, Security Policies, Voice, IoT, Prisma SD-WAN, and Custom TCP Apps) from the Leader to all registered branch peers. Zero-downtime hot reloading, revision tracking, local site overrides, and one-click rollbacks.
8 Bundles 30s Pull Sync Hot-Reload Rollback Leader-Branch
Zero-Touch Peer Onboarding V2 NEW
operations · mesh
Single-command onboarding (curl ... | sudo bash -s -- --controller <URL>) to instantly join remote Linux nodes, branch servers, and Raspberry Pis to a central Stigix Leader. Dynamic target synthesis automatically exposes learned peers across the mesh with self-filtering and heartbeat monitoring — zero external dependencies.
1-Line Onboard Direct Controller Target Synthesis No-Cloudflare
Physical Underlay & Actions V2 NEW
topology · physical · chaos
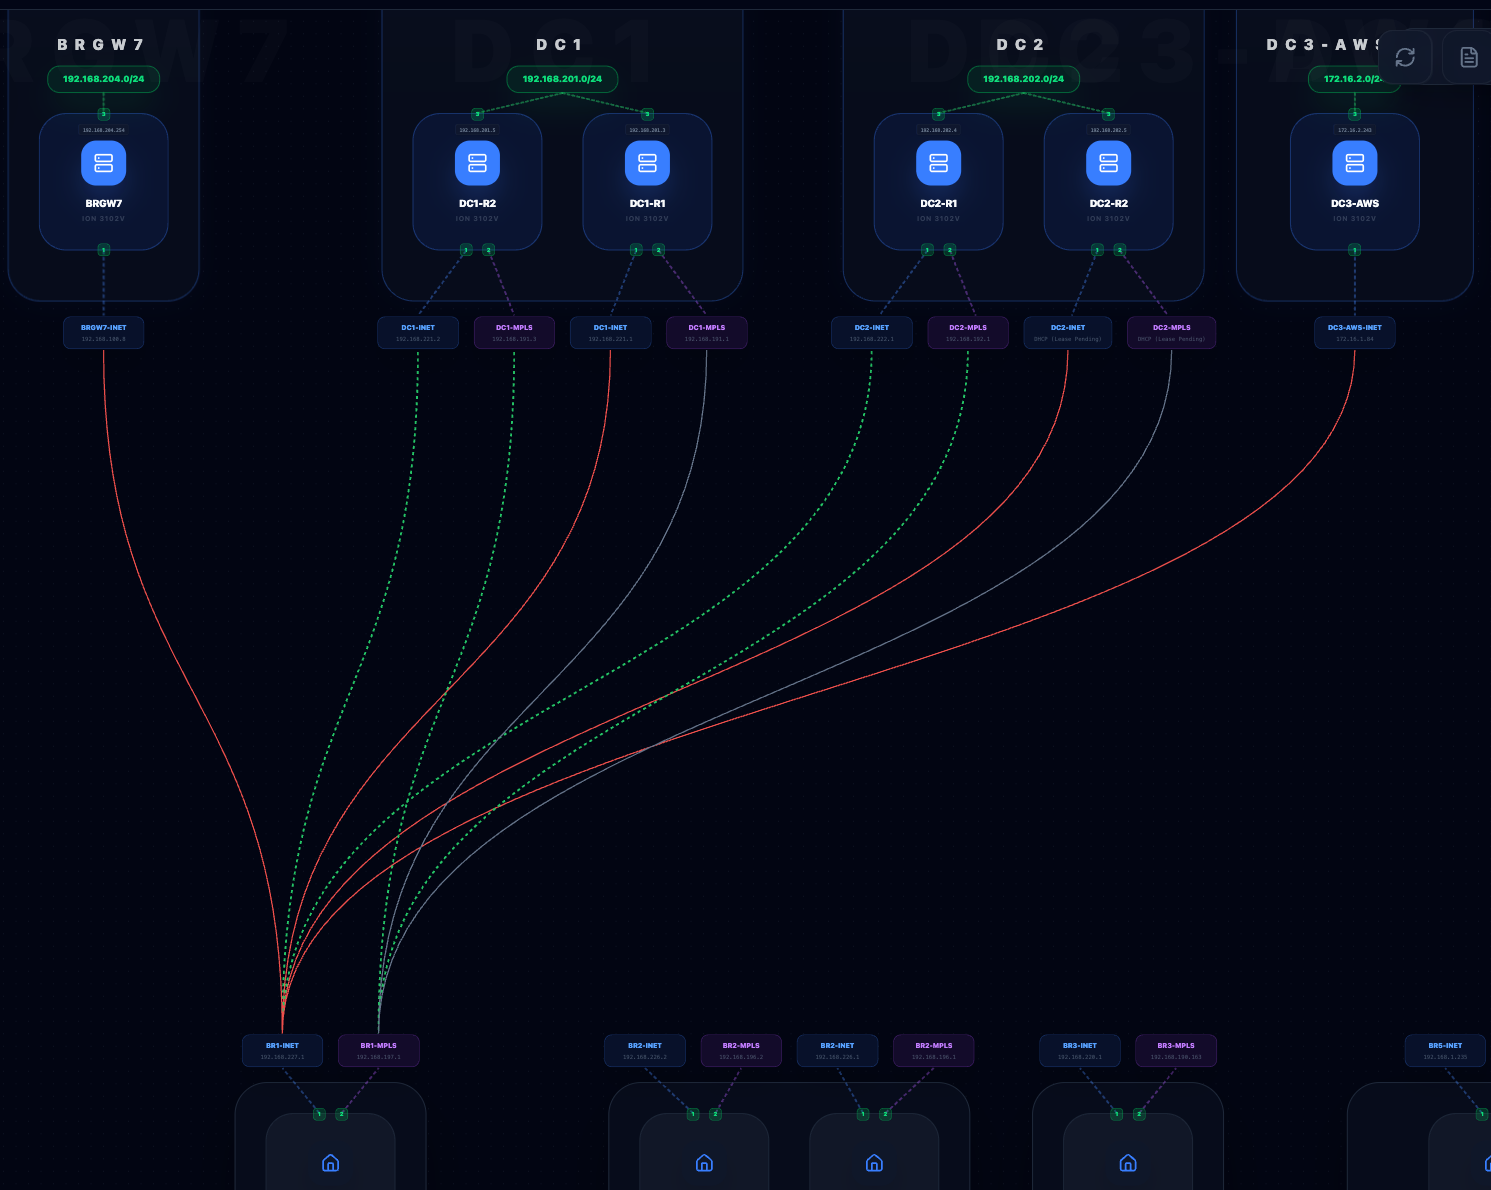
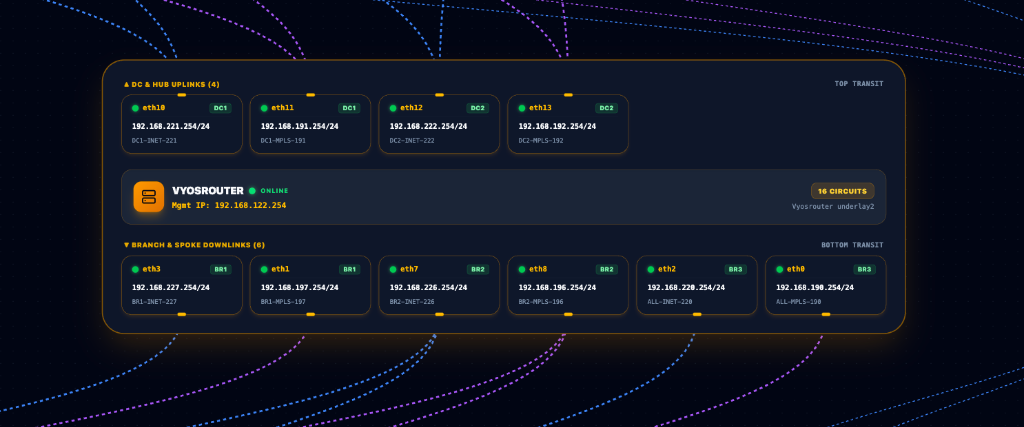
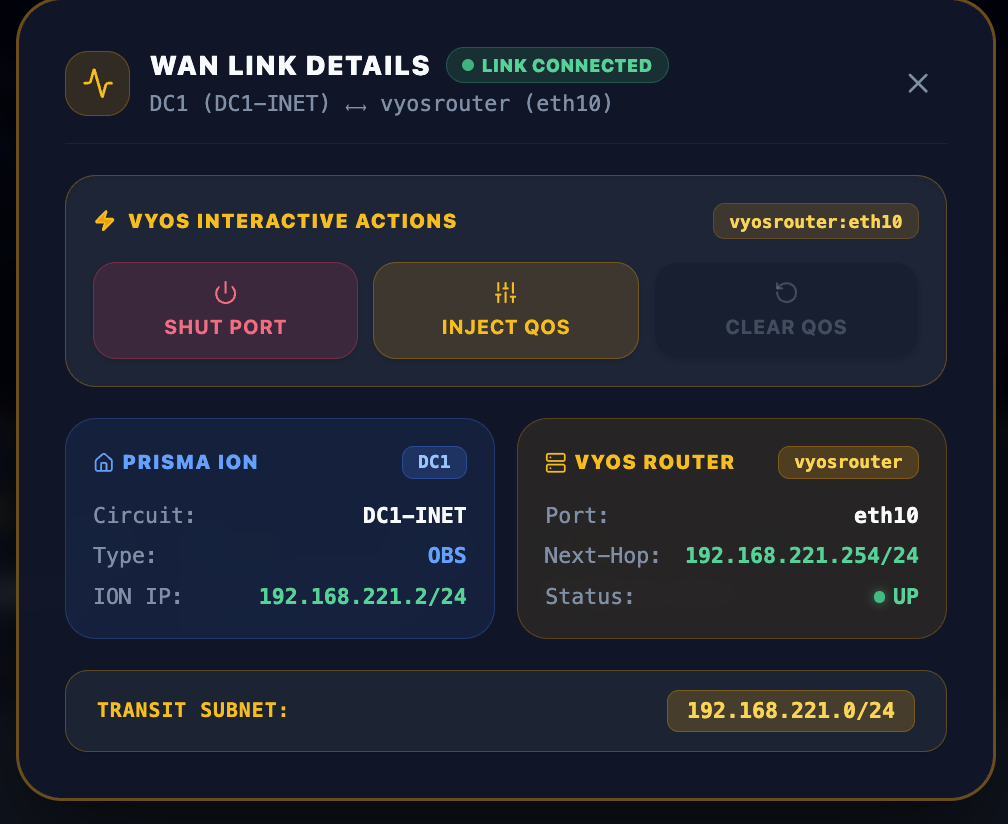
Real-time interactive canvas visualization of physical VyOS backbone routers with direct 1:1 port-to-port cable wiring and spatial anti-crossing alignment. Execute direct topology actions: instant Shut / No-Shut port toggle with live status write-through, Inject WAN Impairment (Netem latency/loss), and persistent QoS badges on canvas port chips.
Physical Underlay Interactive Actions Shut/No-Shut Netem Sliders 1:1 Cabling
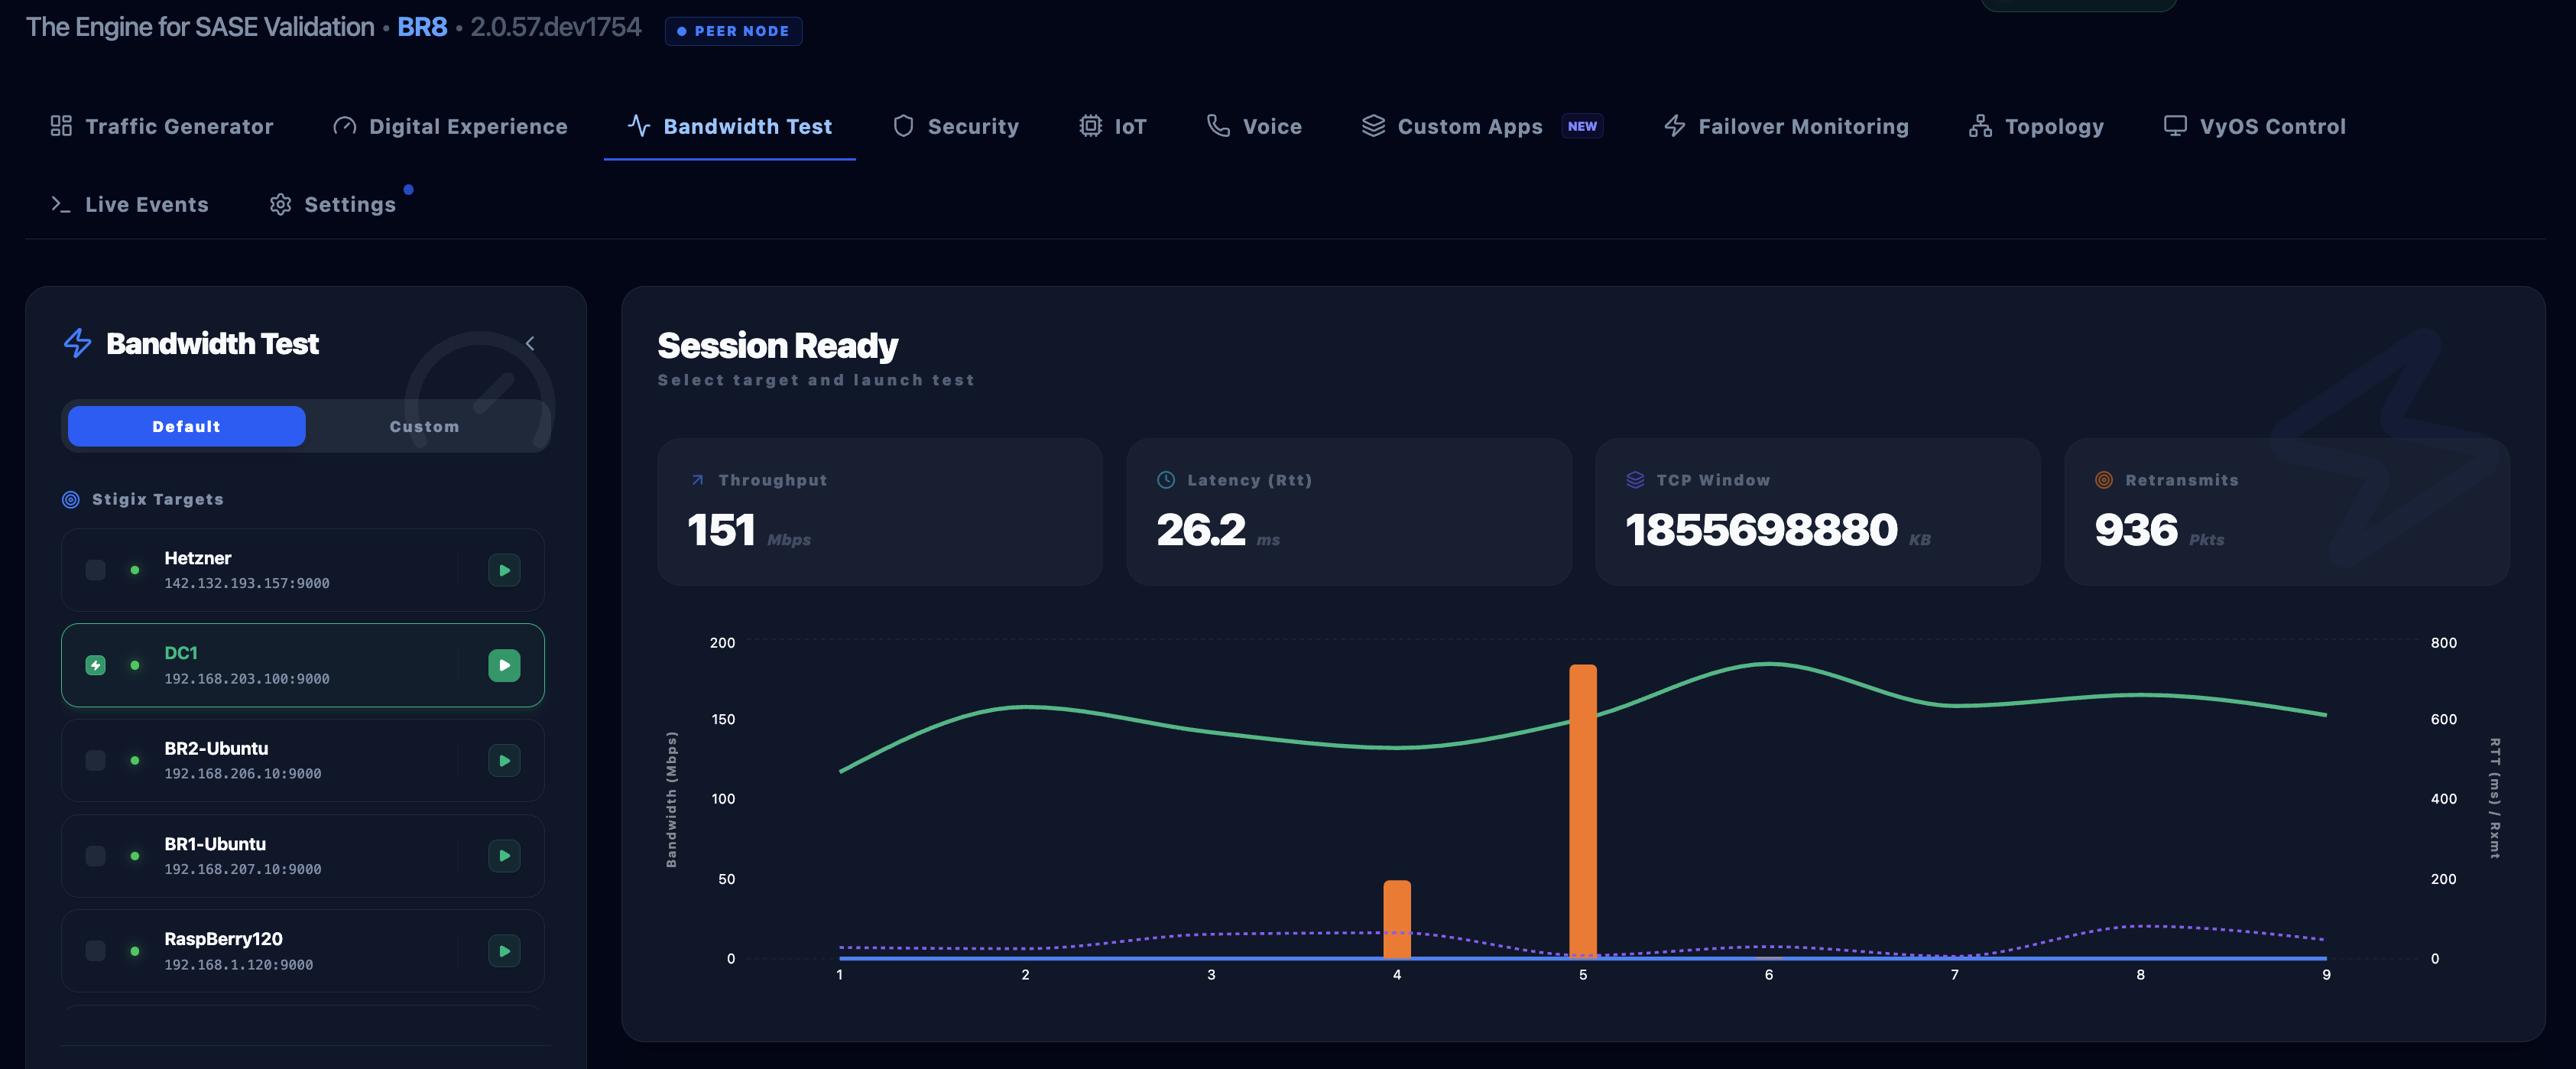
SaaS Traffic Generation
traffic control
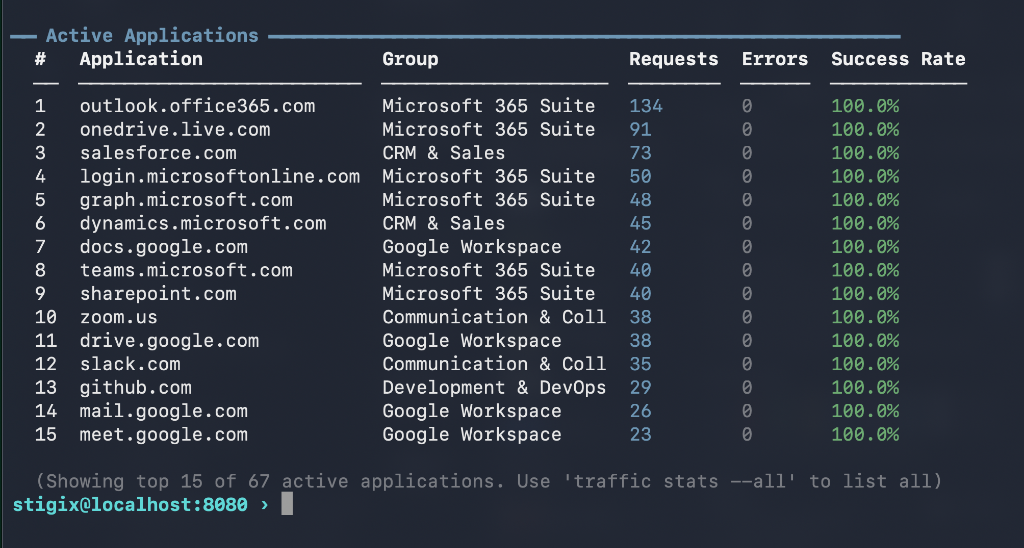
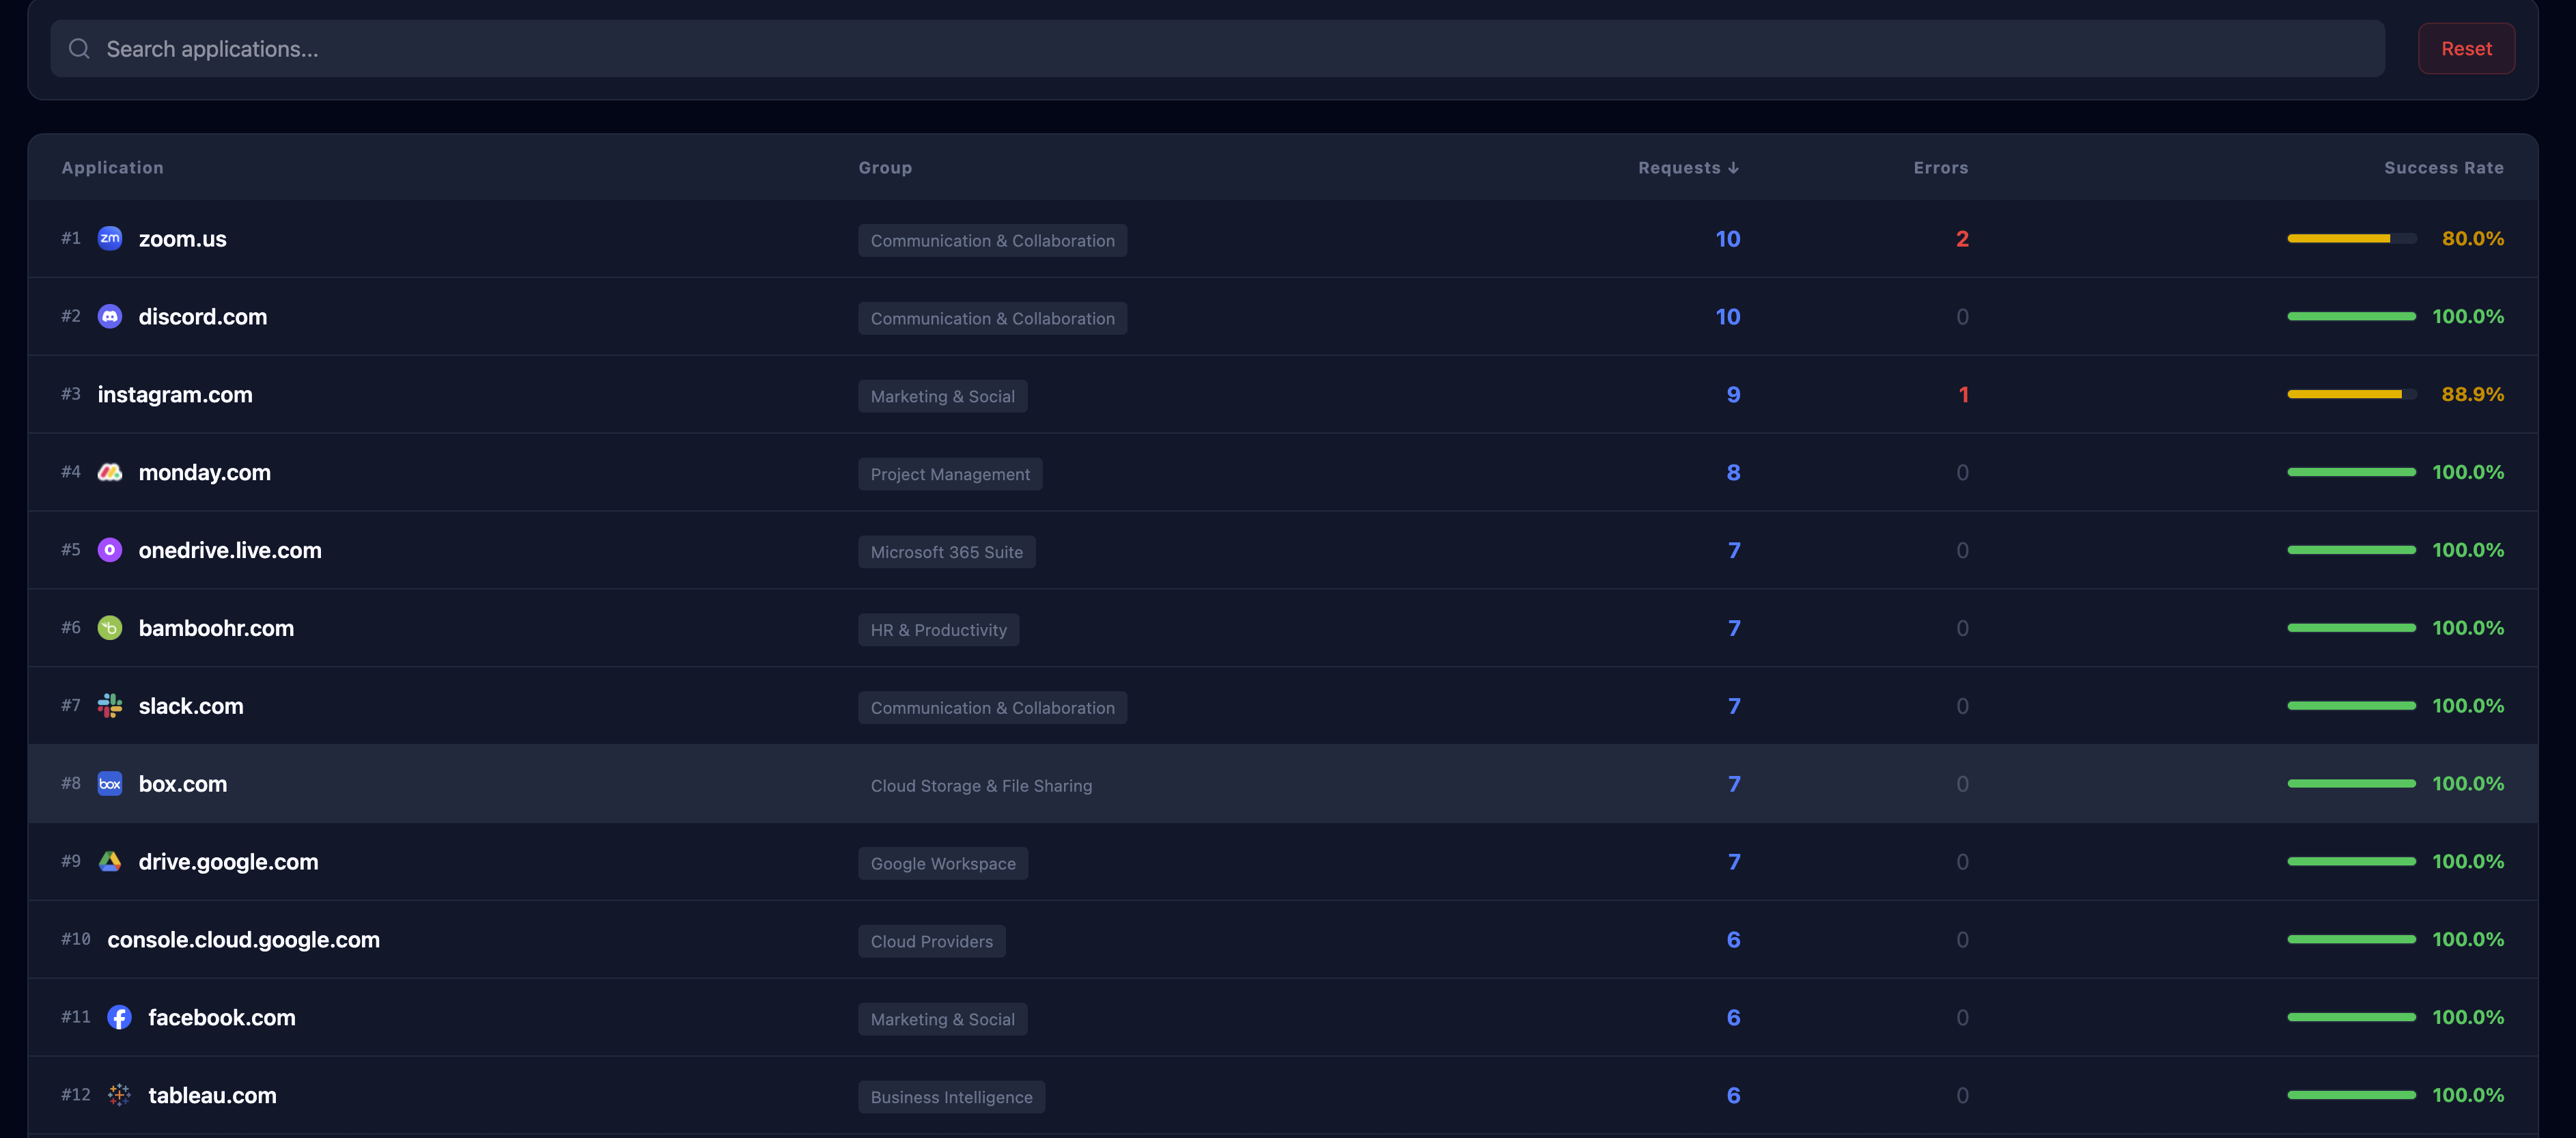
67 pre-configured SaaS applications including Google Workspace, Microsoft 365, Salesforce, and Zoom. Authentic HTTP/S requests with proper User-Agent headers and Referers. Weighted distribution per application group with live rate control from the dashboard.
67 apps HTTP/S Weighted Rate slider
Digital Experience
performance monitoring
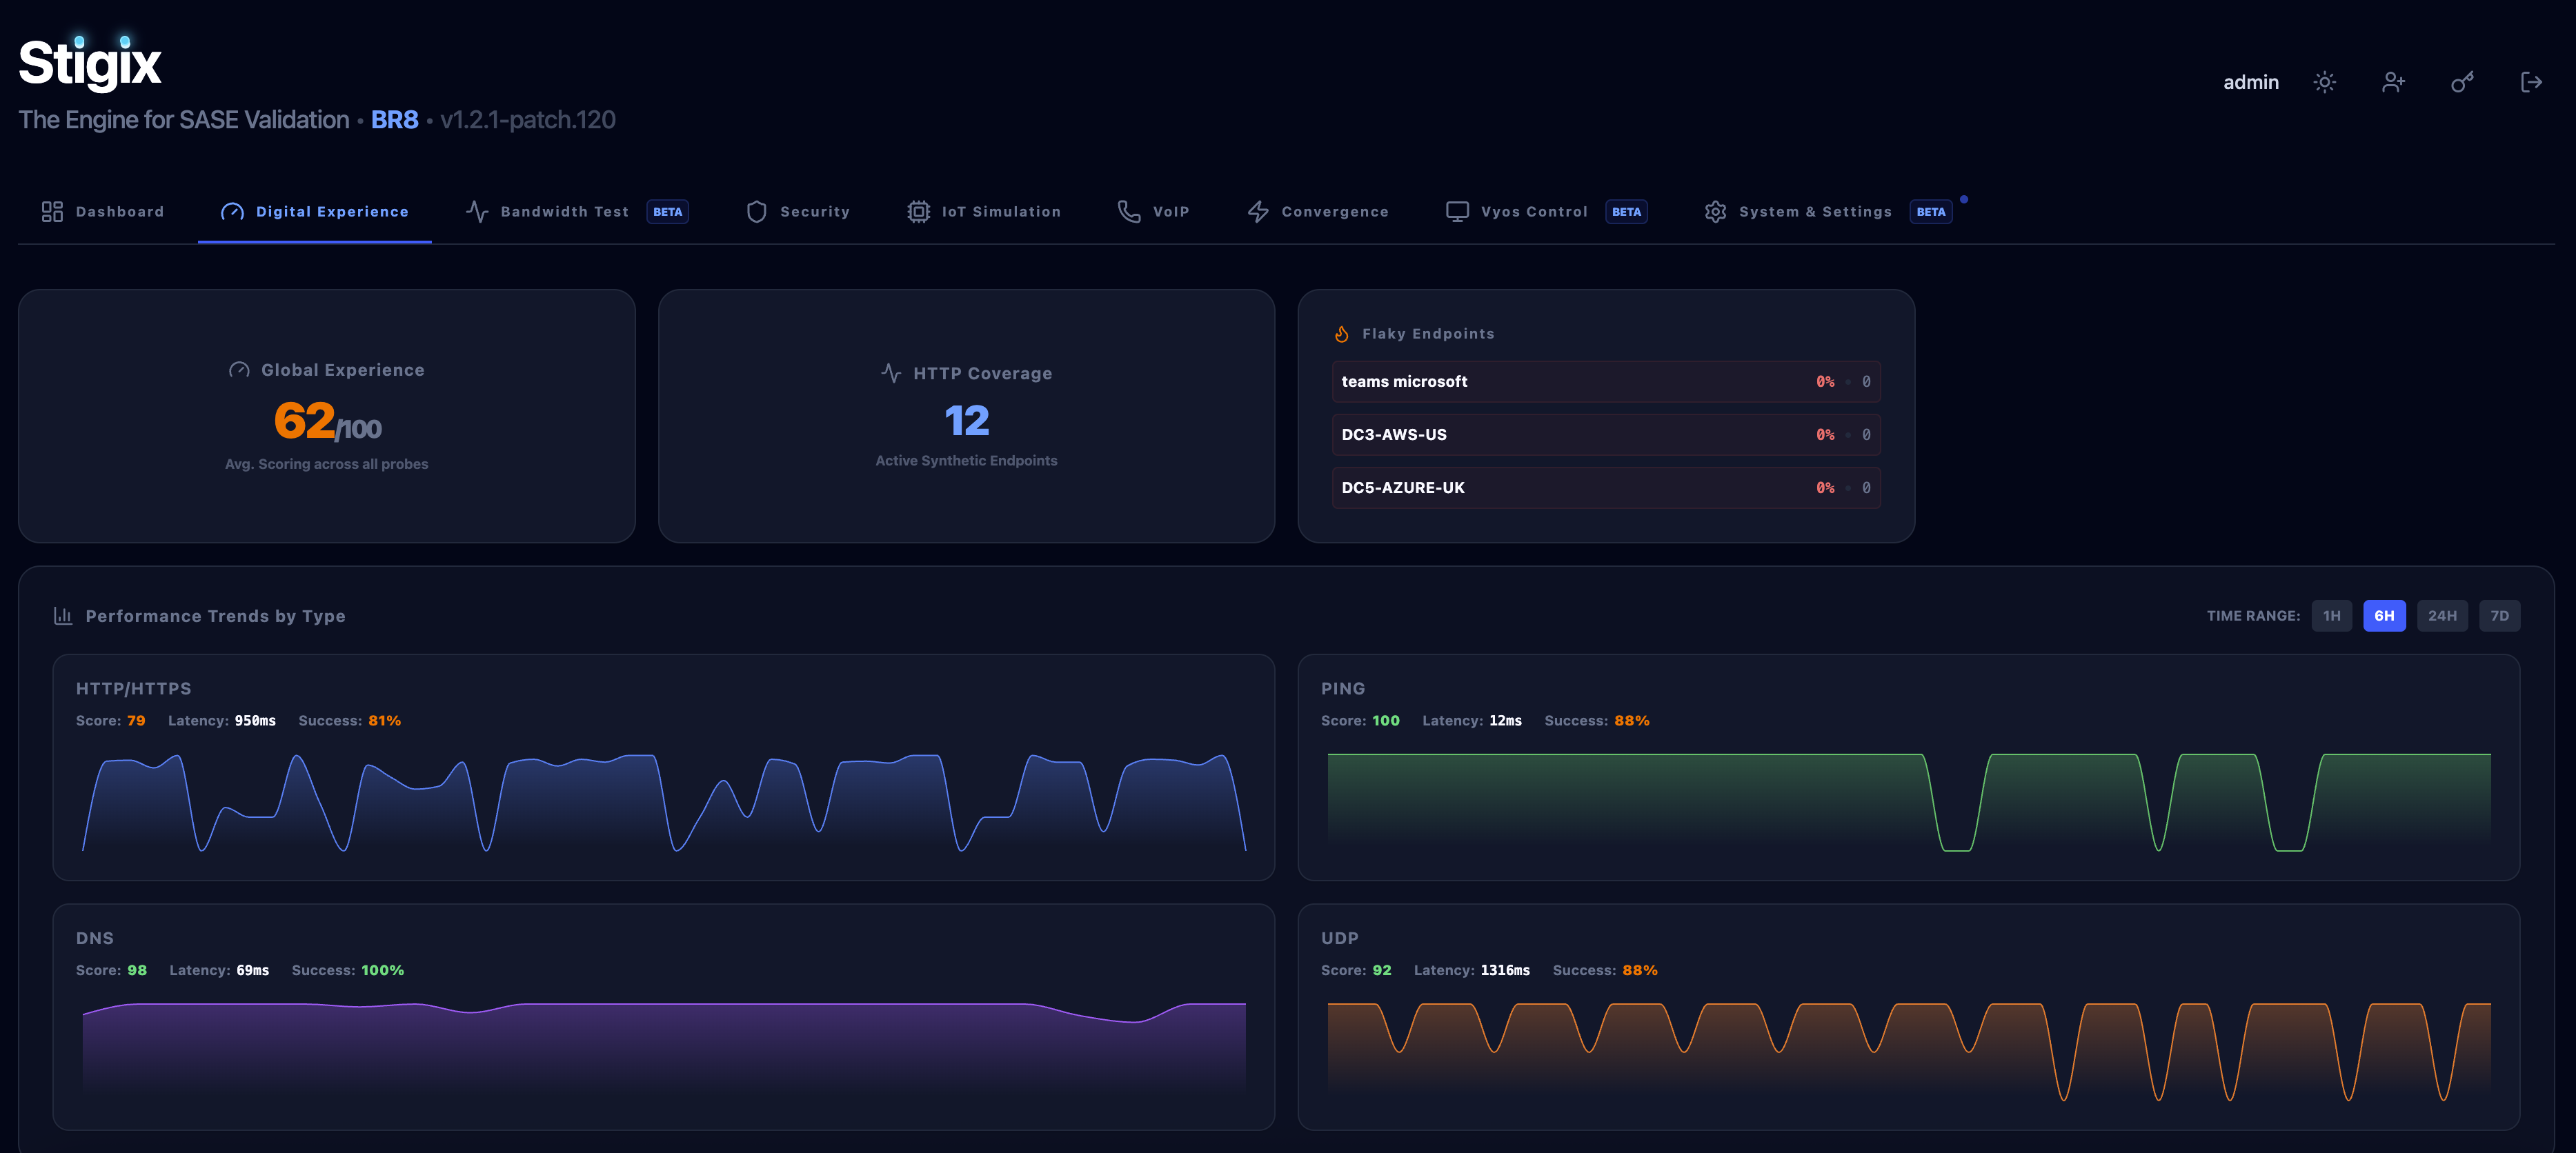
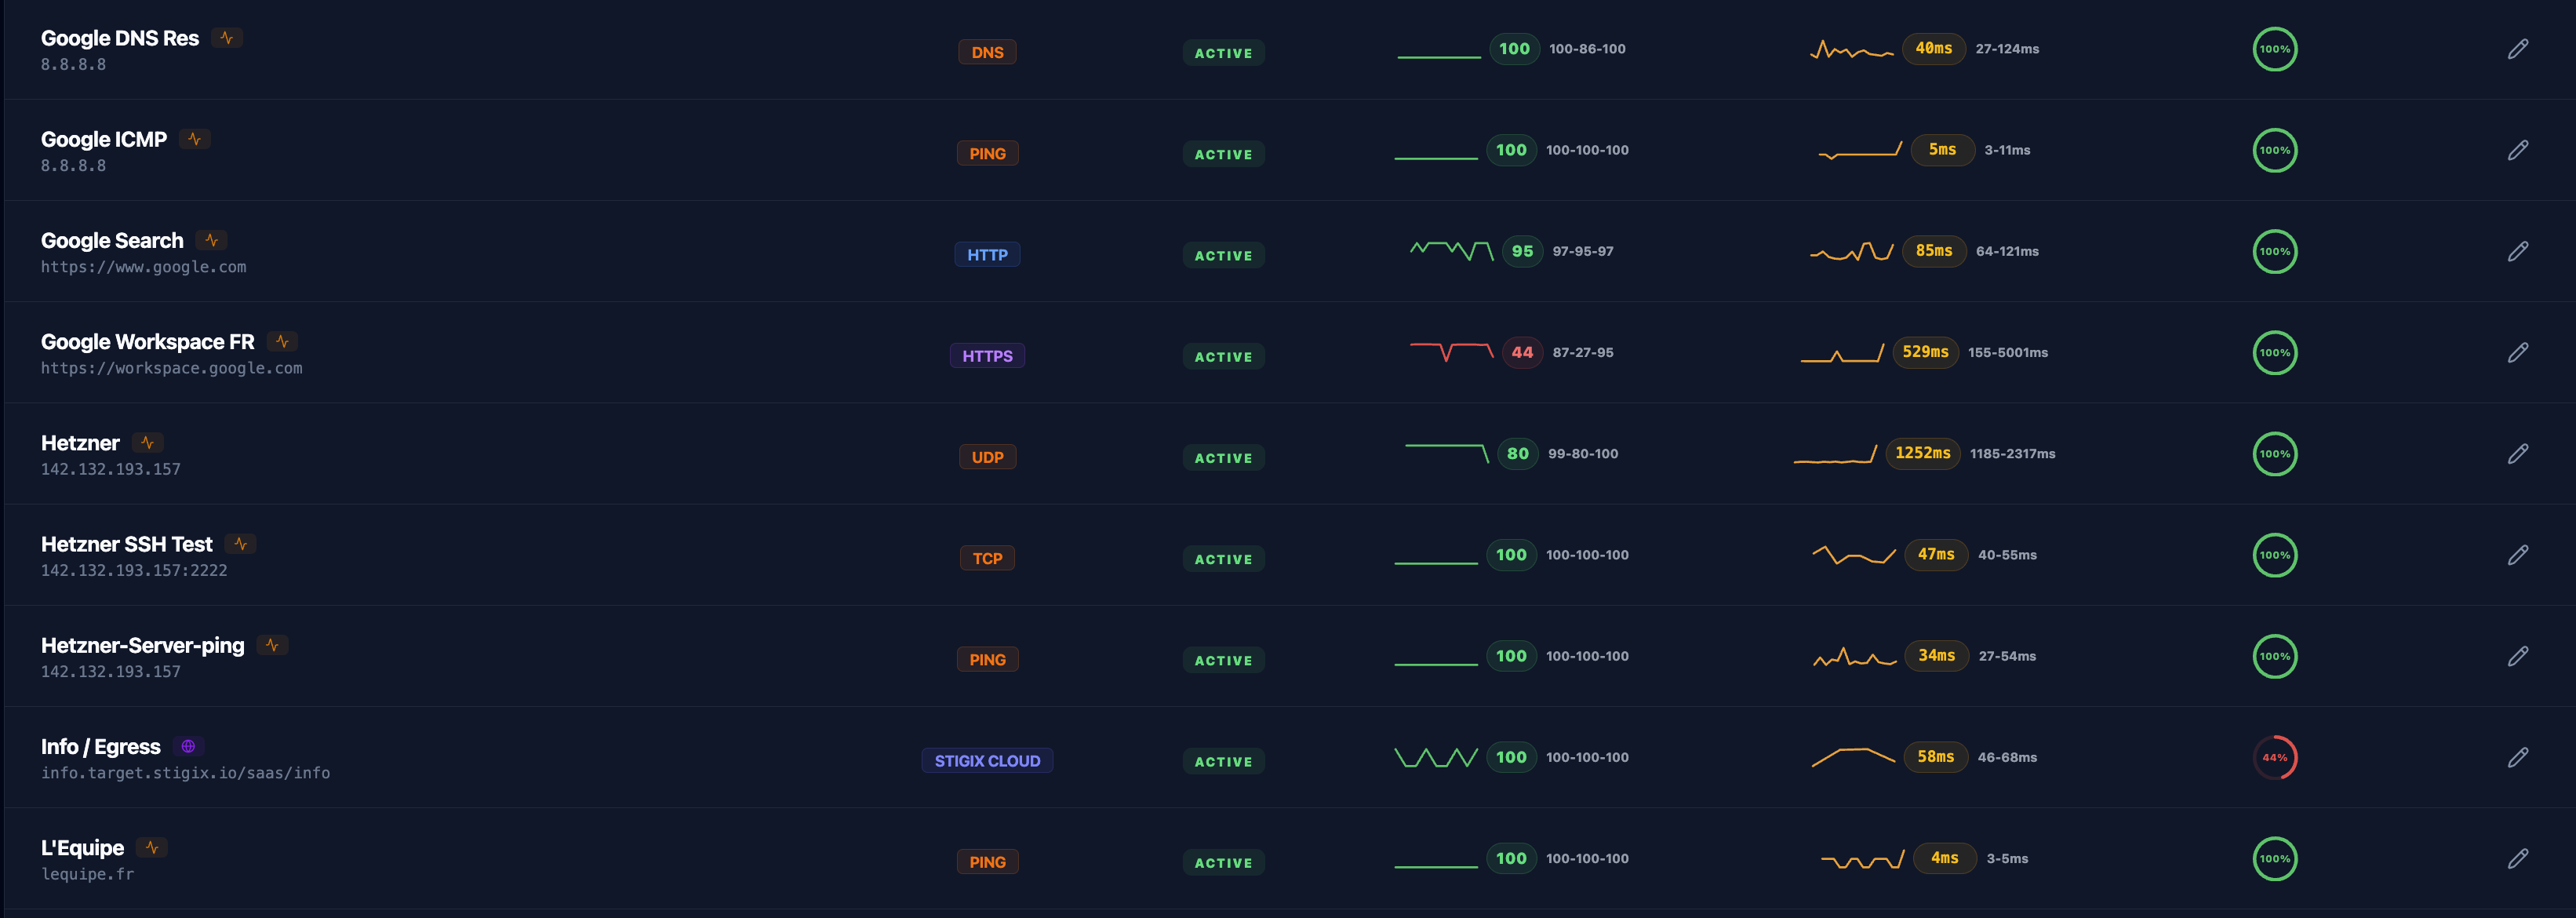
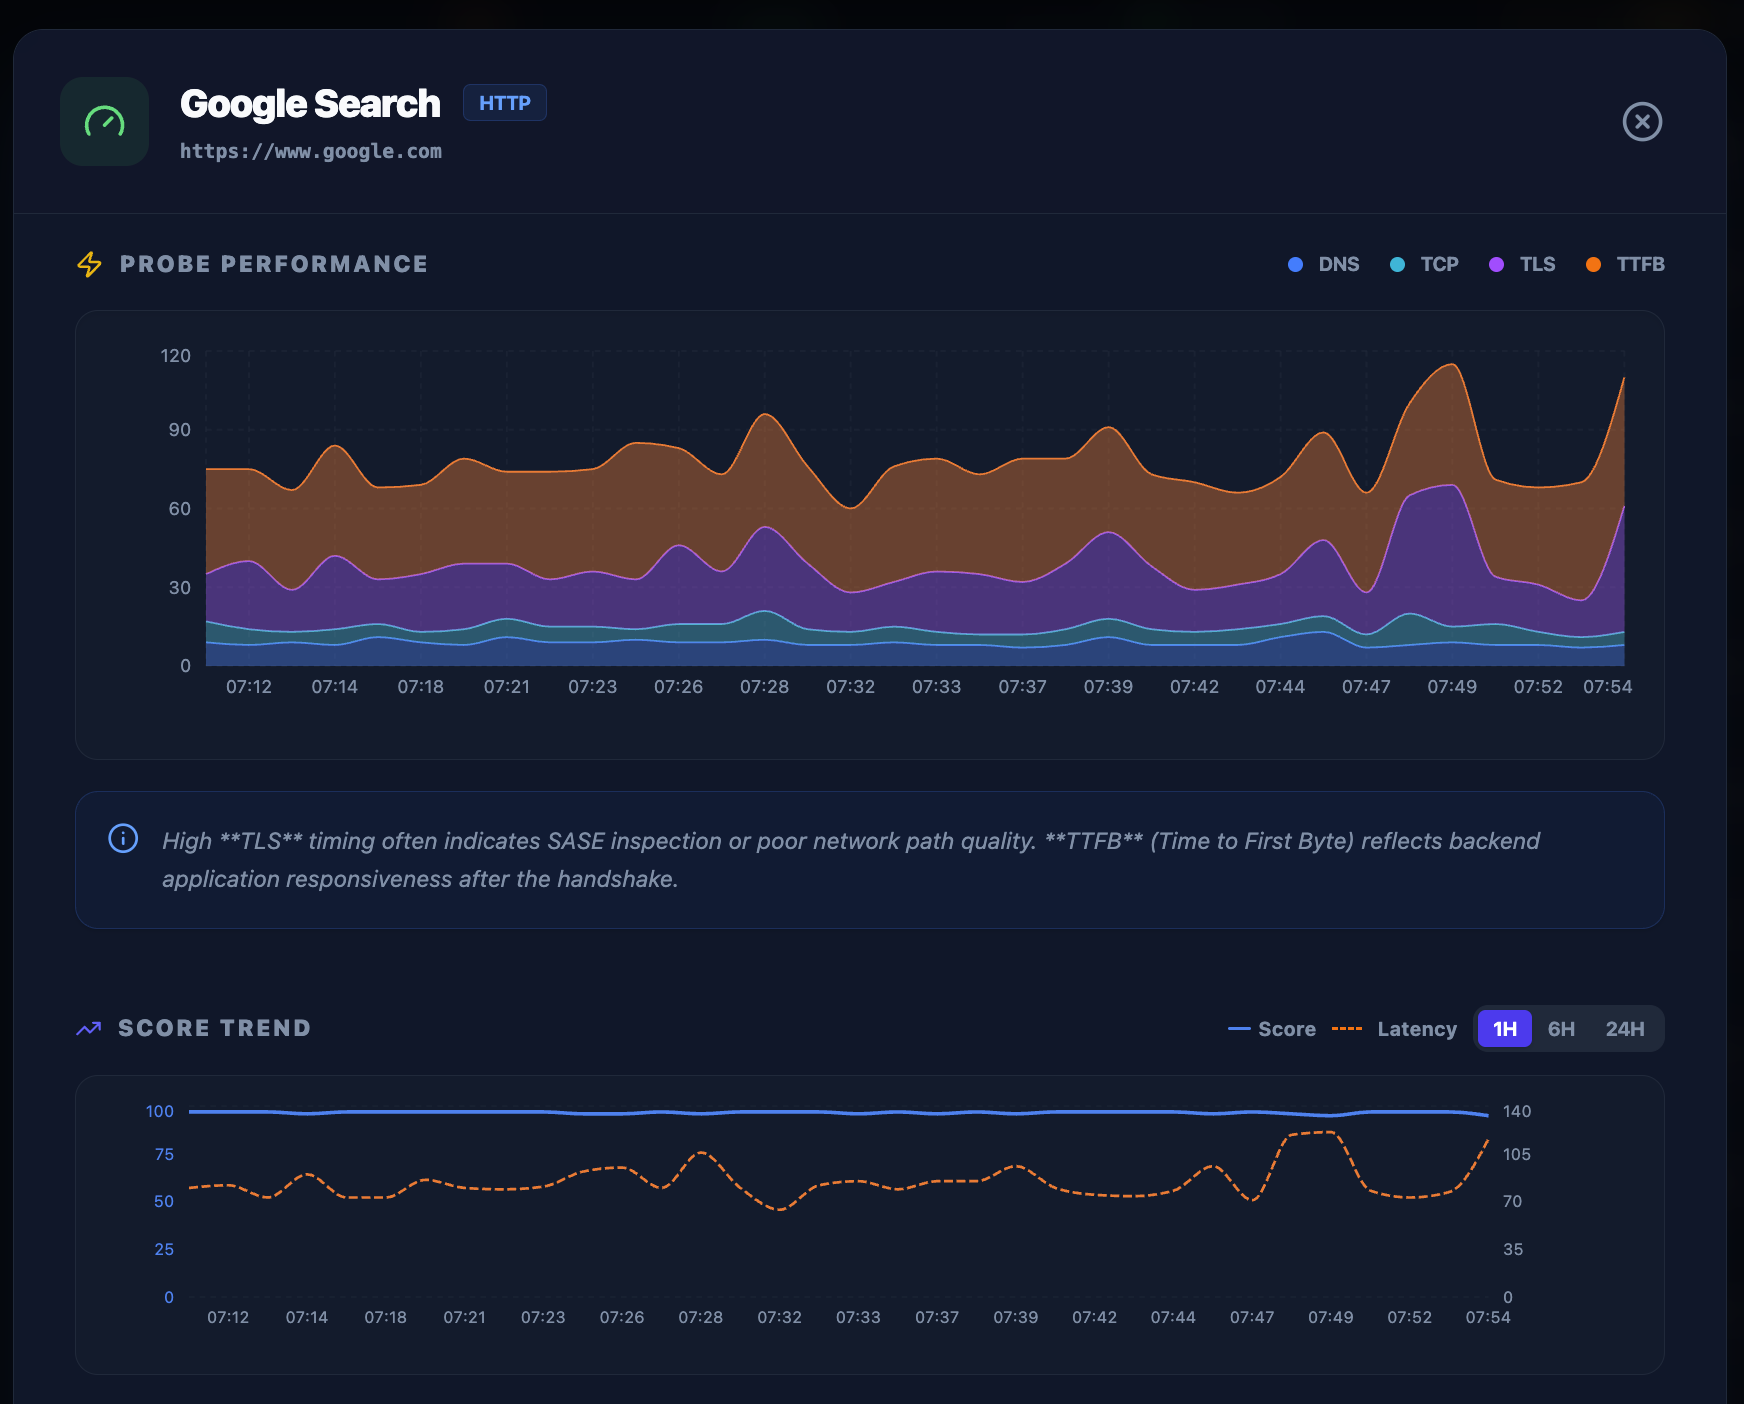
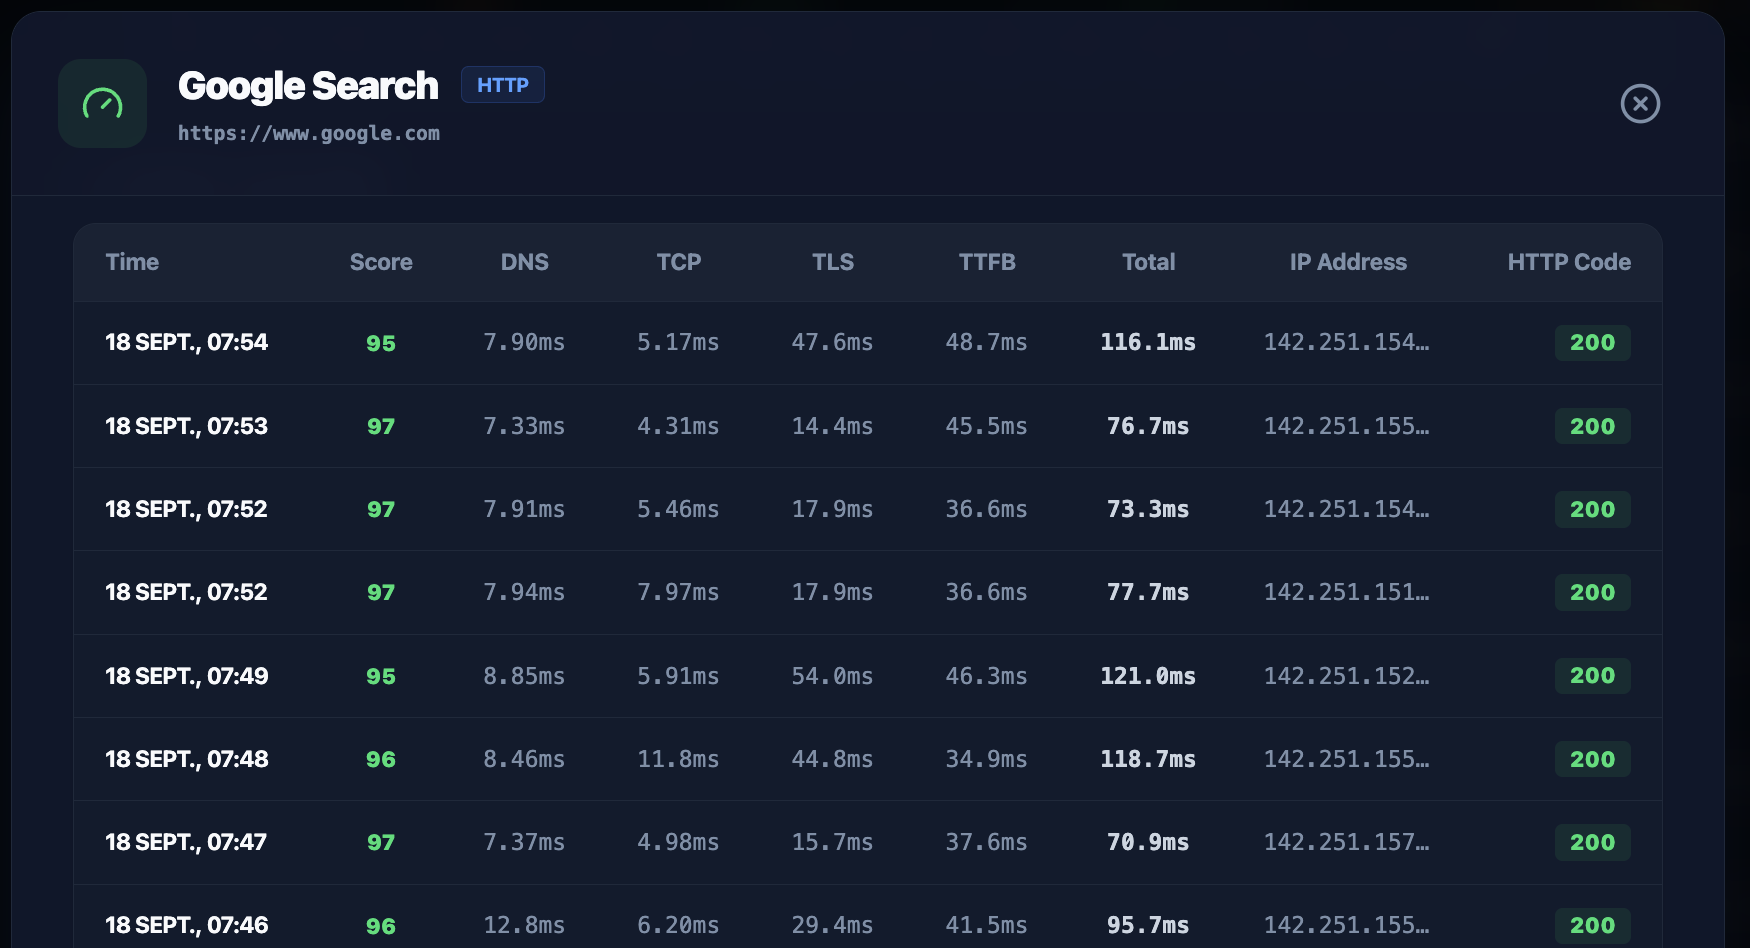
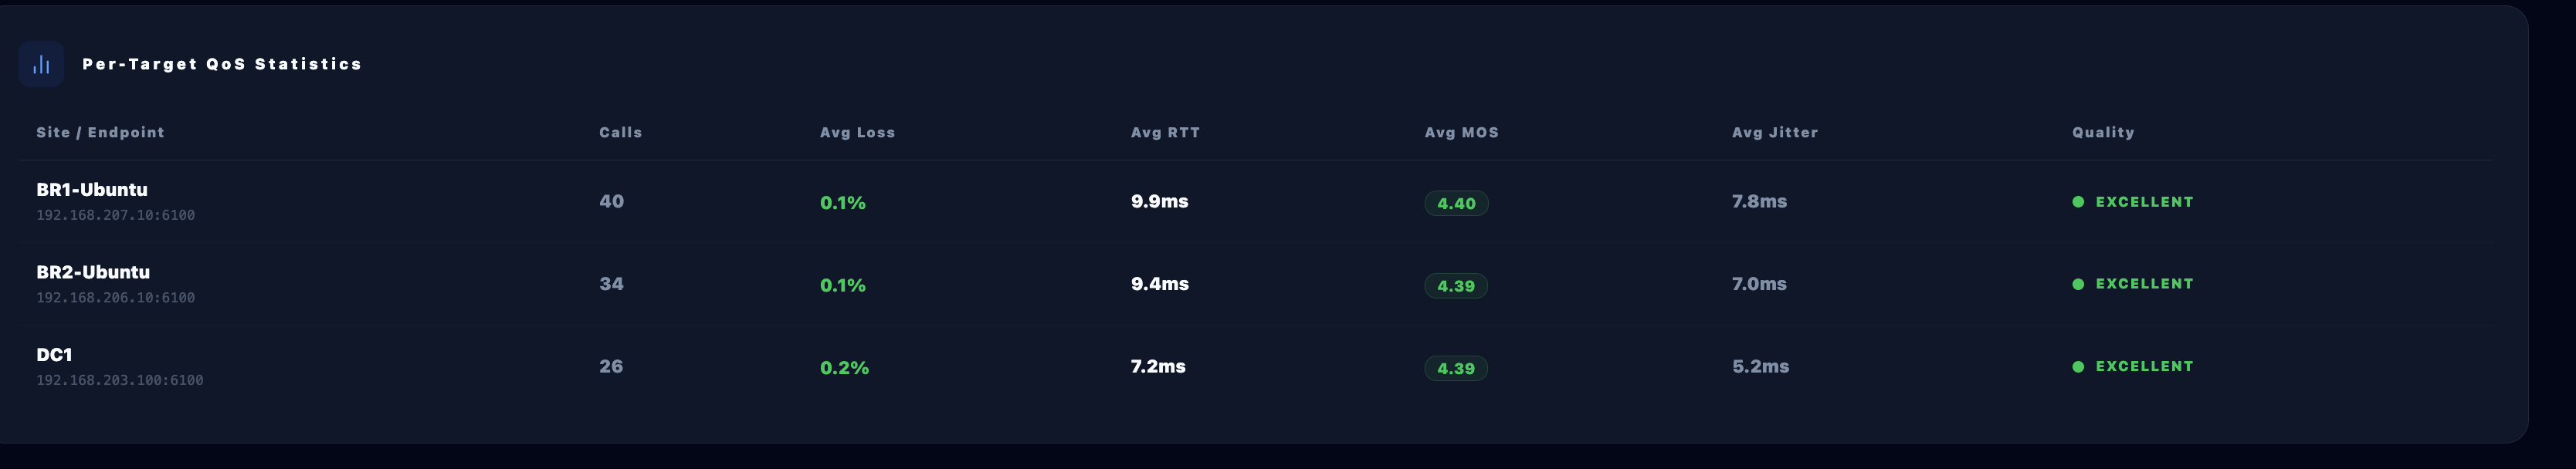
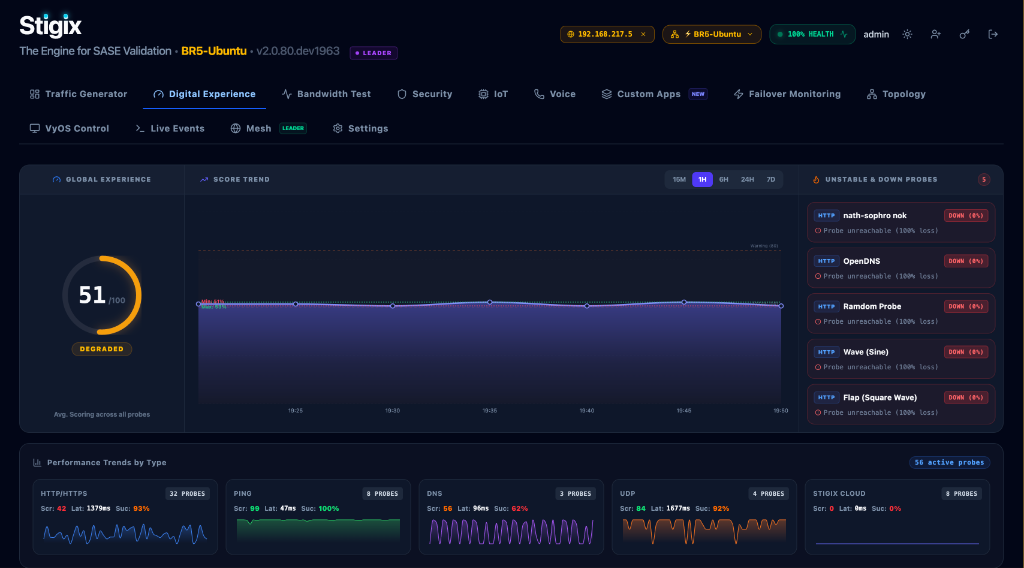
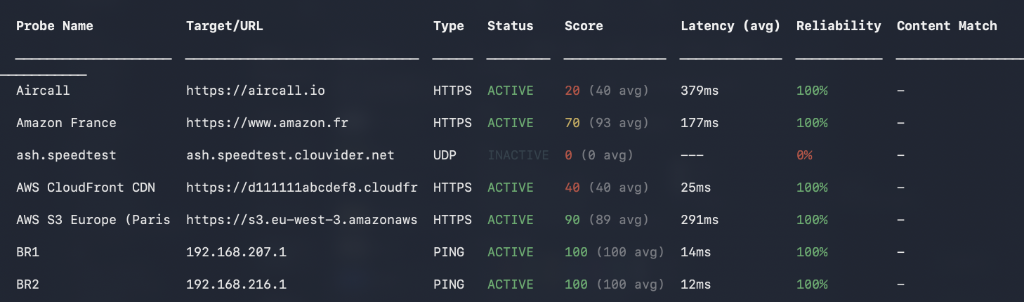
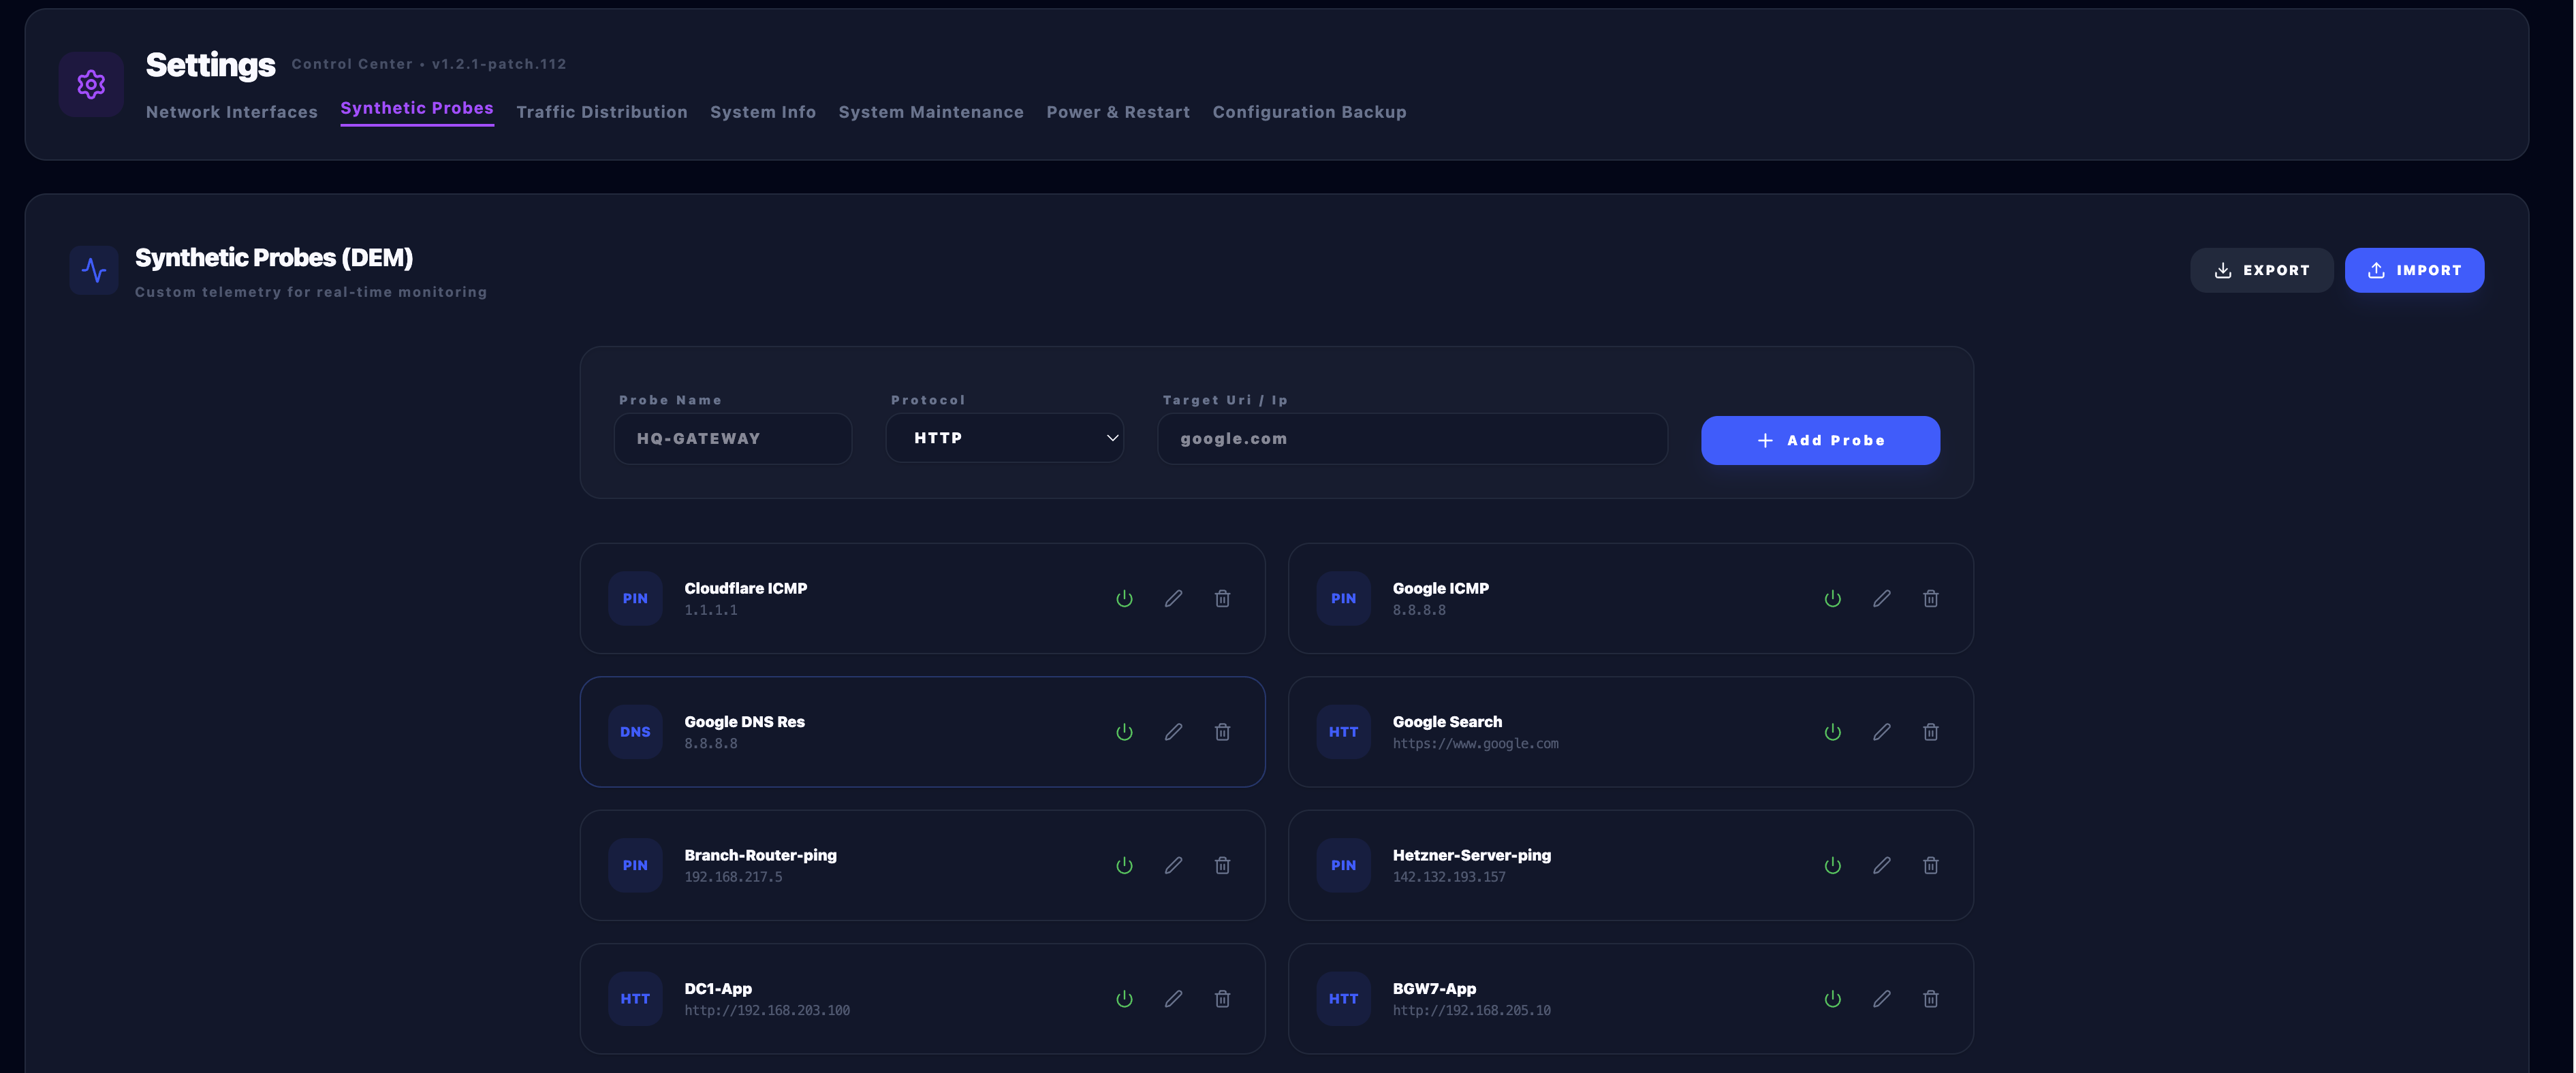
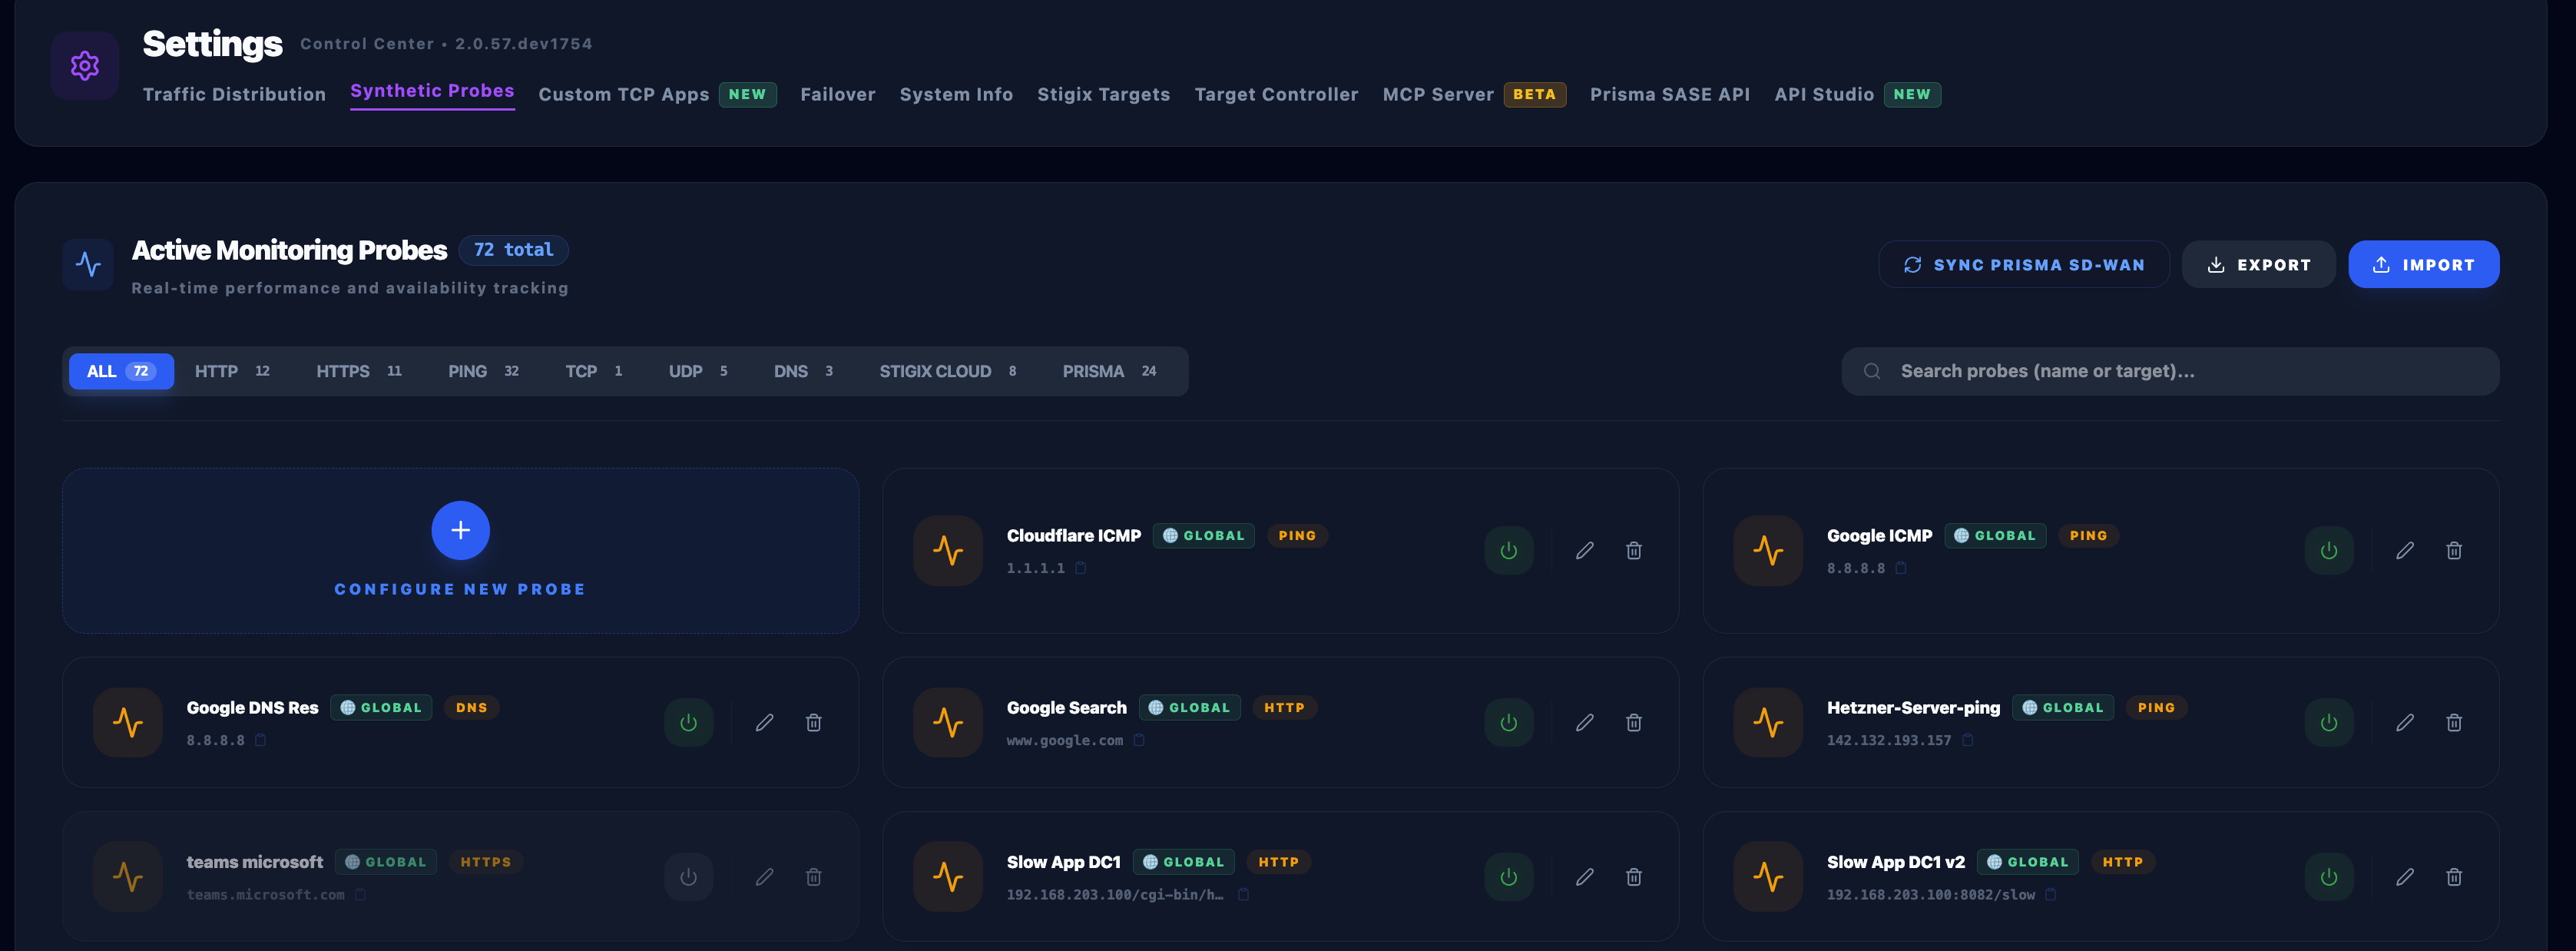
Synthetic connectivity probes (HTTP, ICMP, TCP) with per-site latency tracking and endpoint health monitoring. Real-time log streaming via WebSocket. Live statistics dashboard with success/failure rates, latency metrics, and bandwidth tracking. Export results in JSON, CSV, or JSONL. 7-day persistent JSONL storage with auto-rotation.
HTTP/ICMP/TCP WebSocket JSON/CSV 7-day log
Security Validation
security
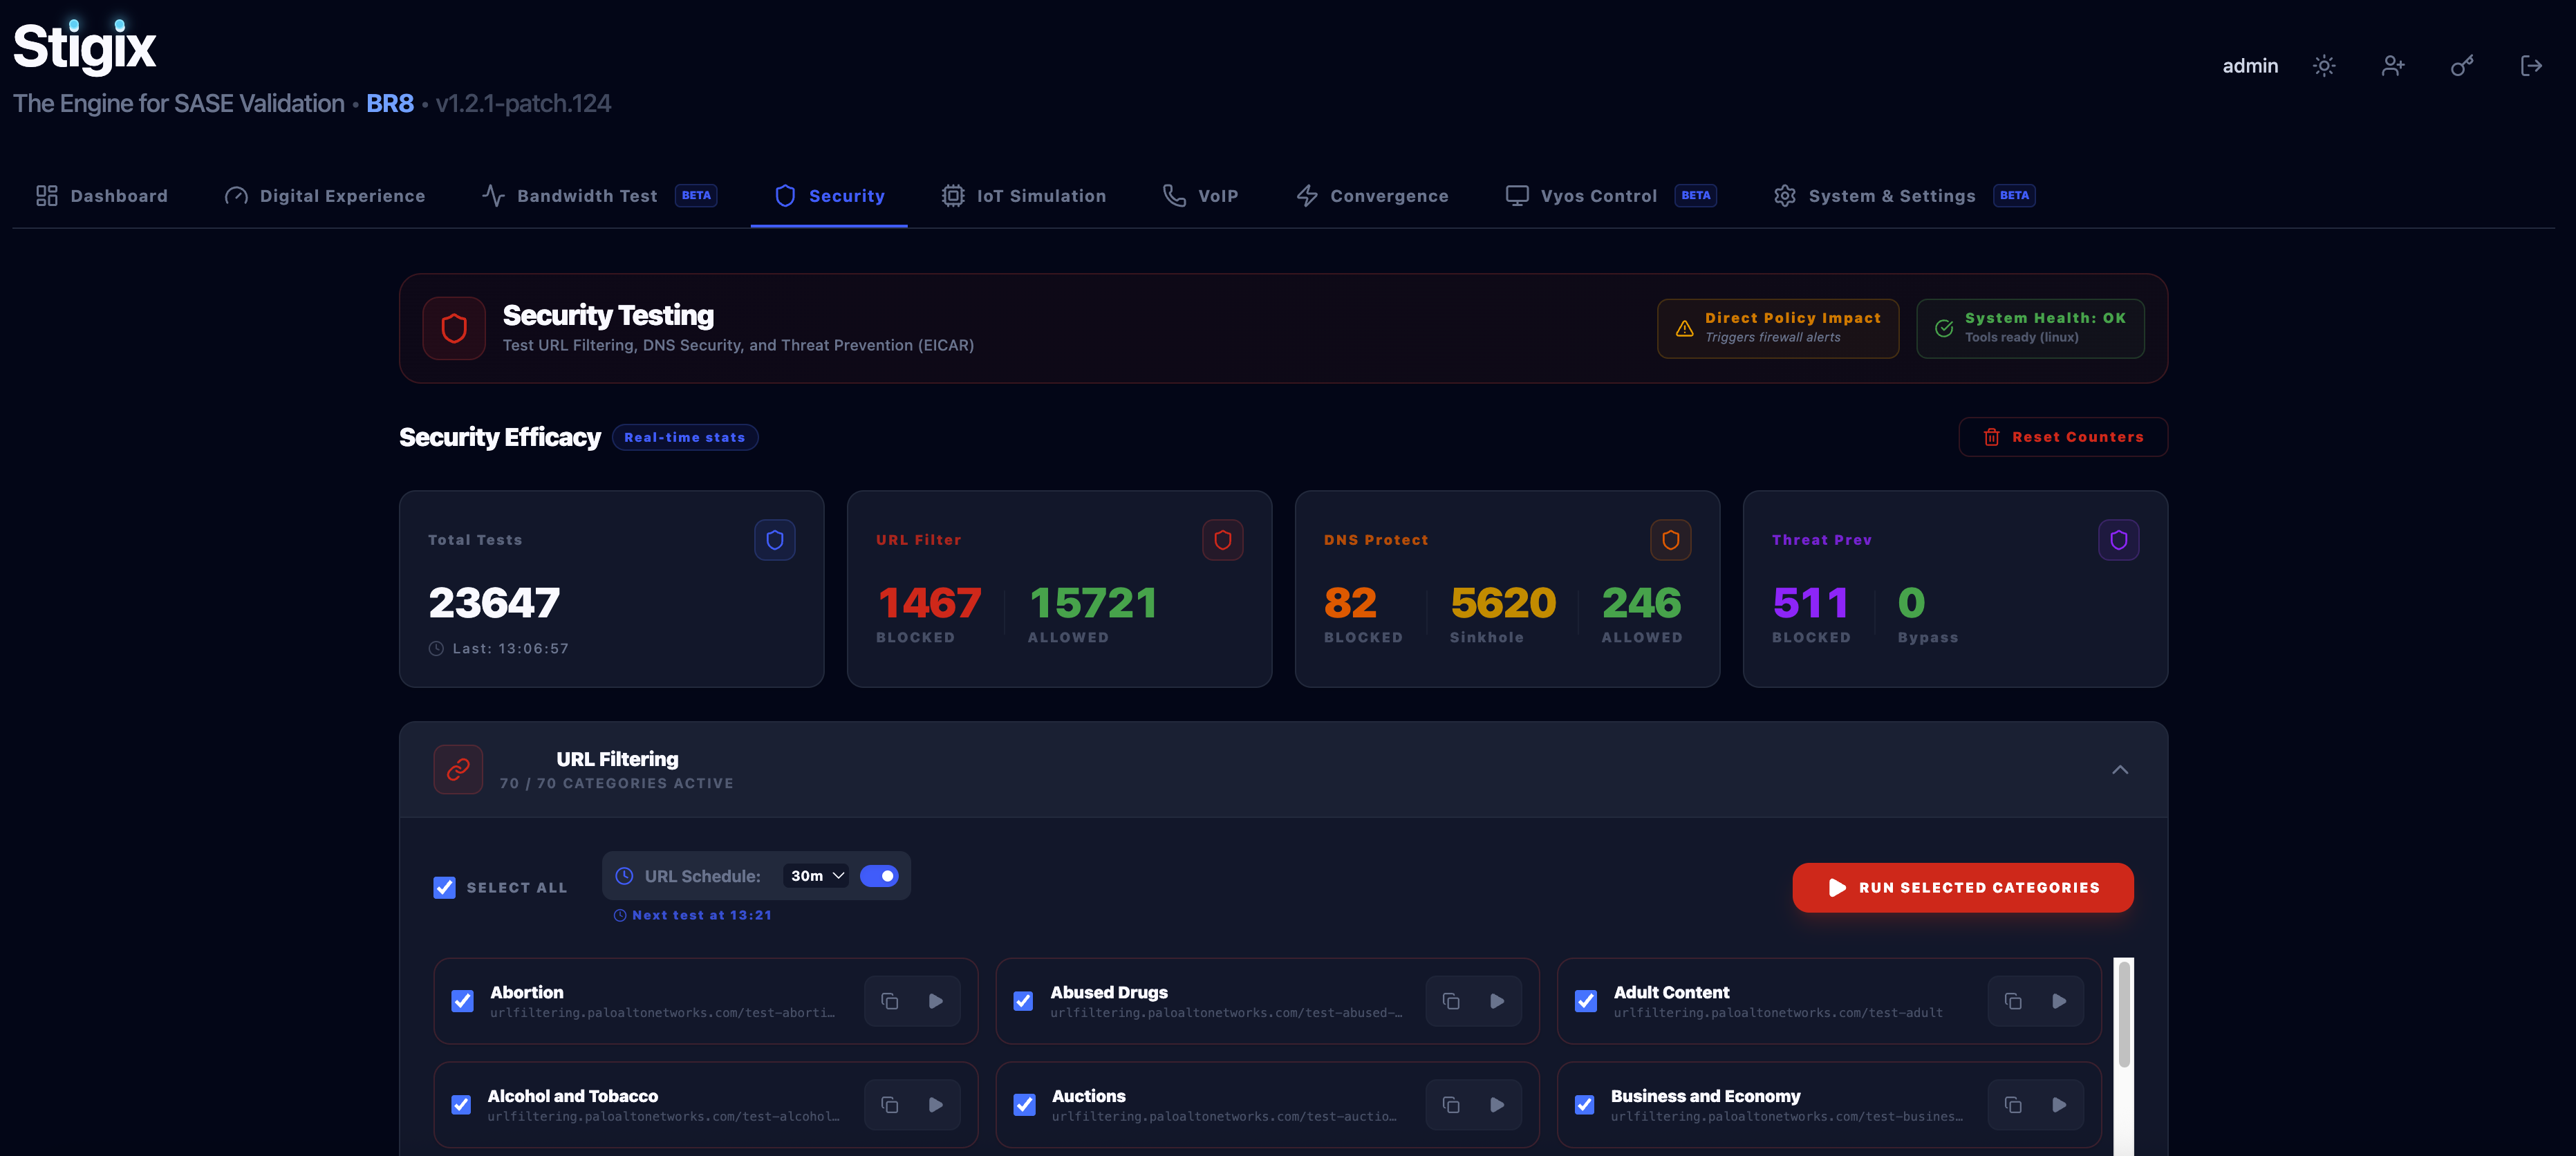
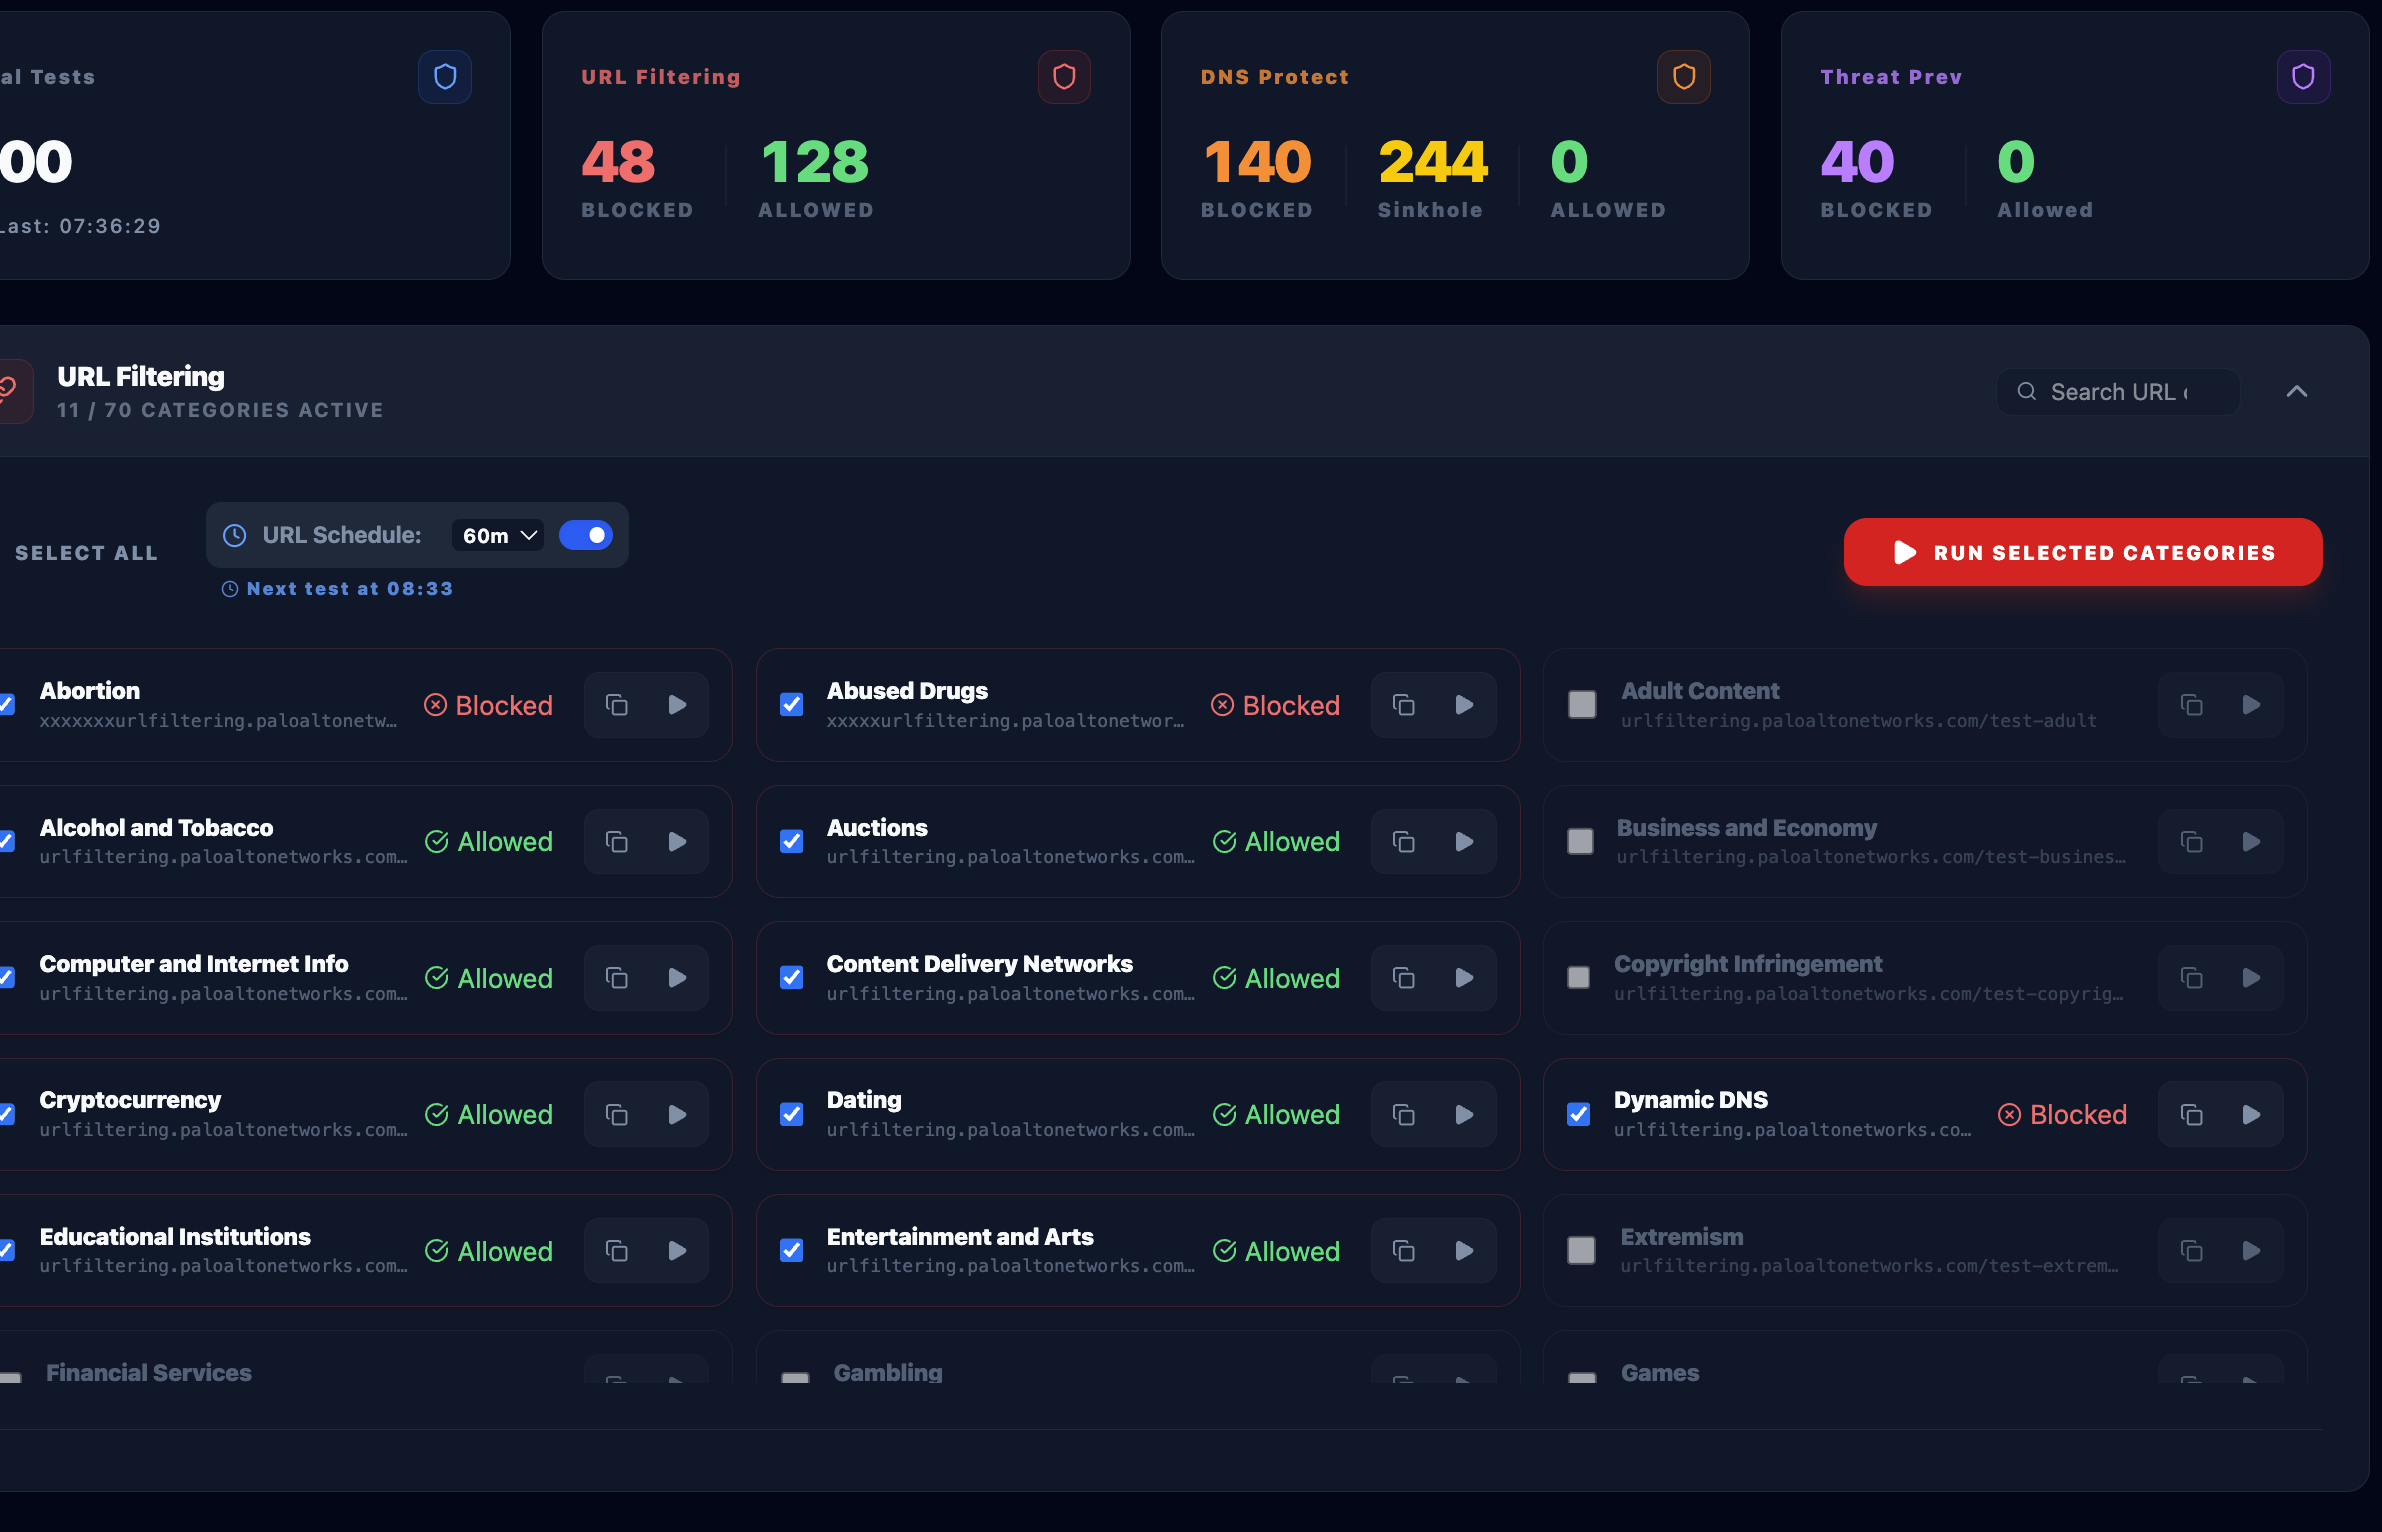
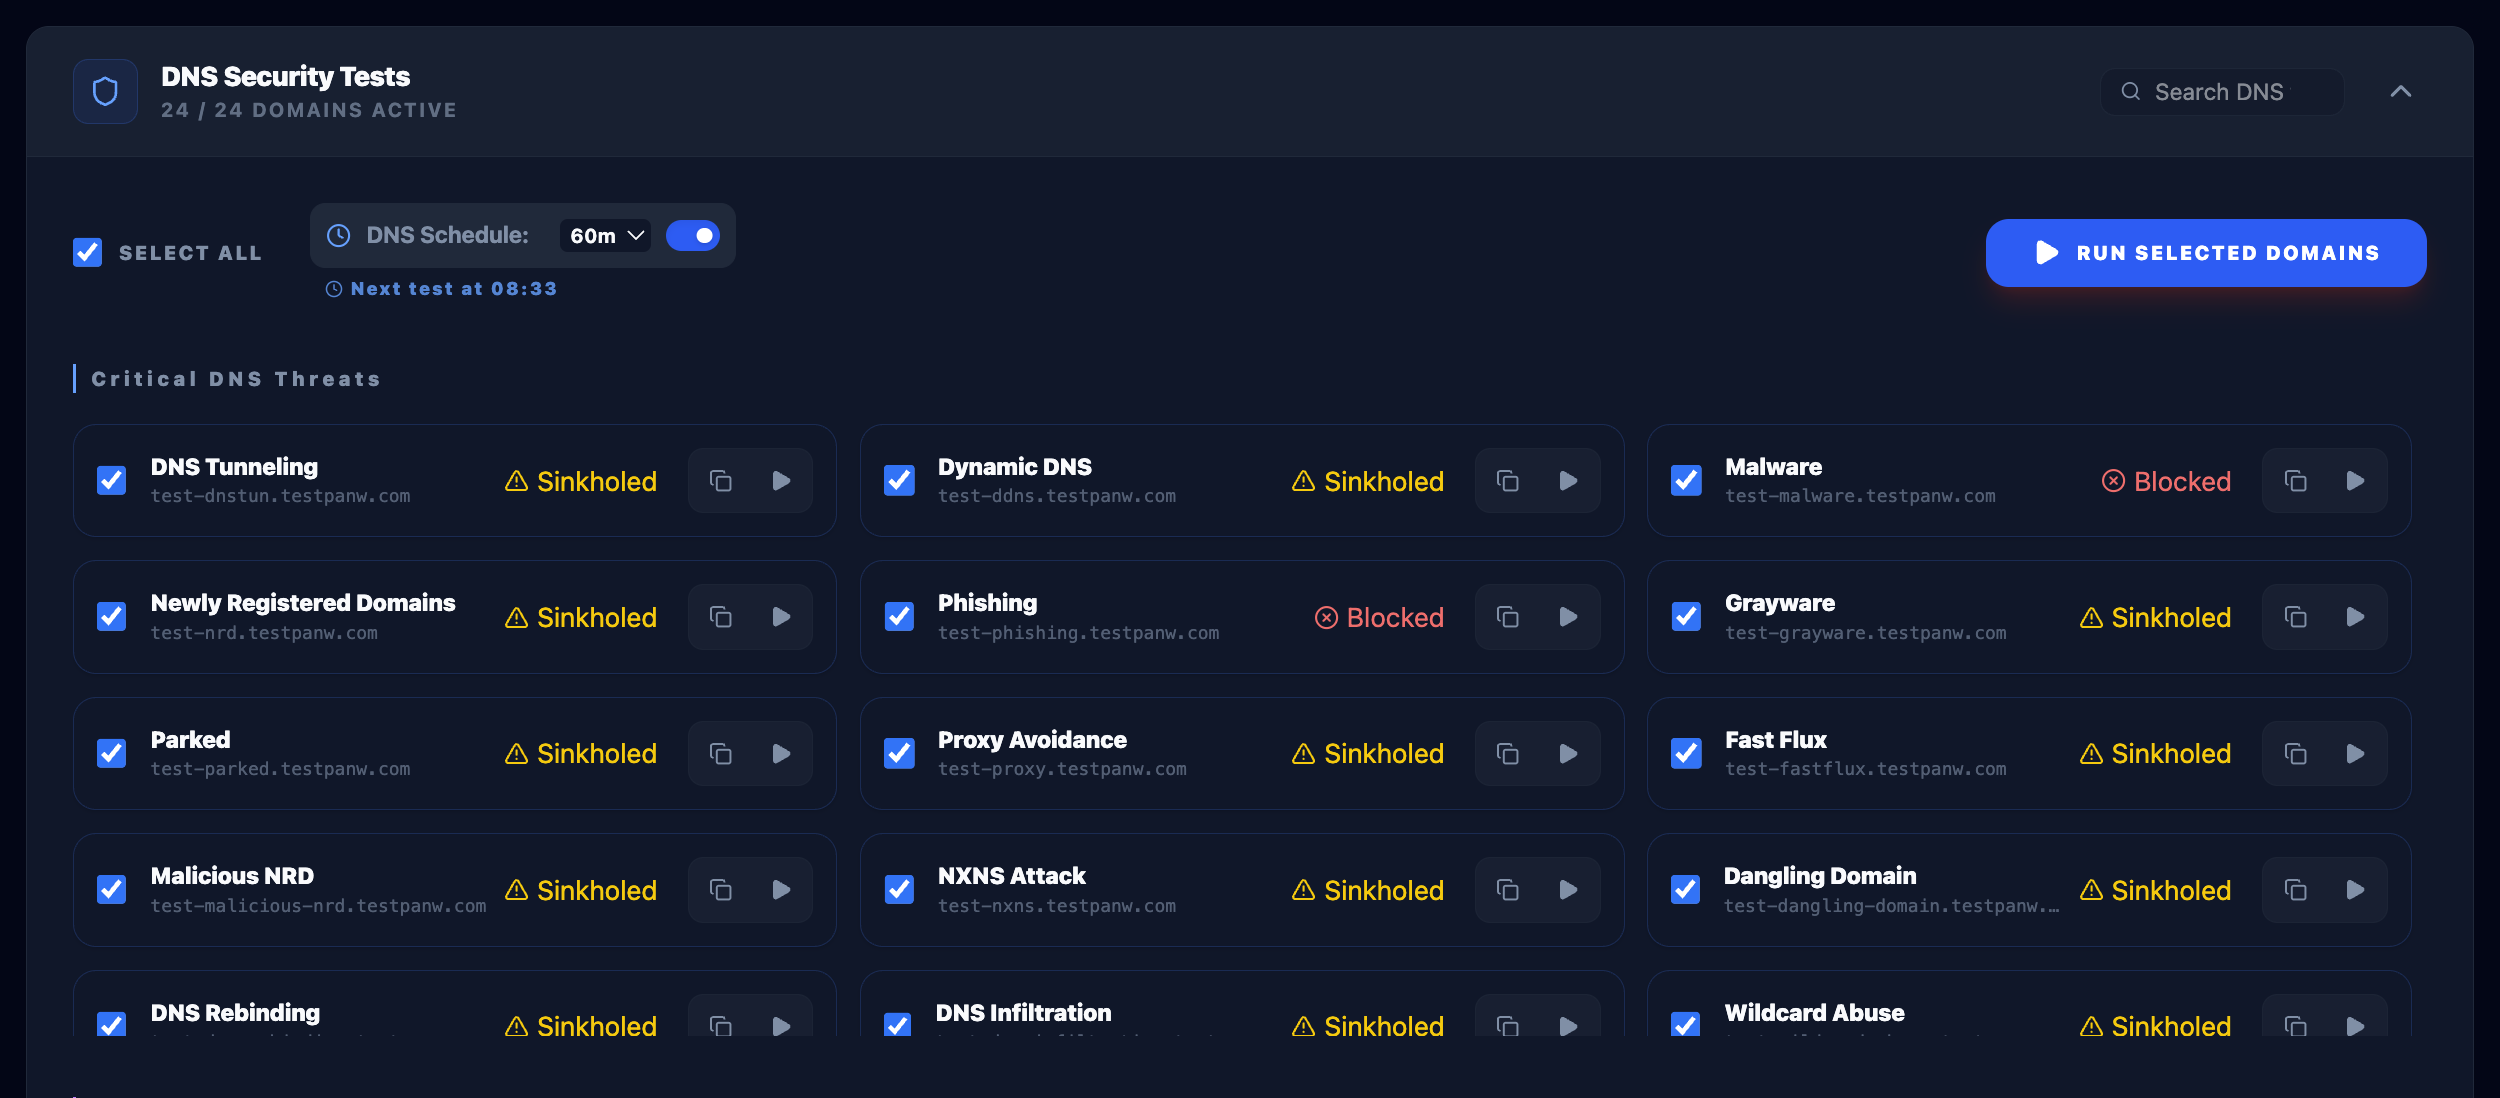
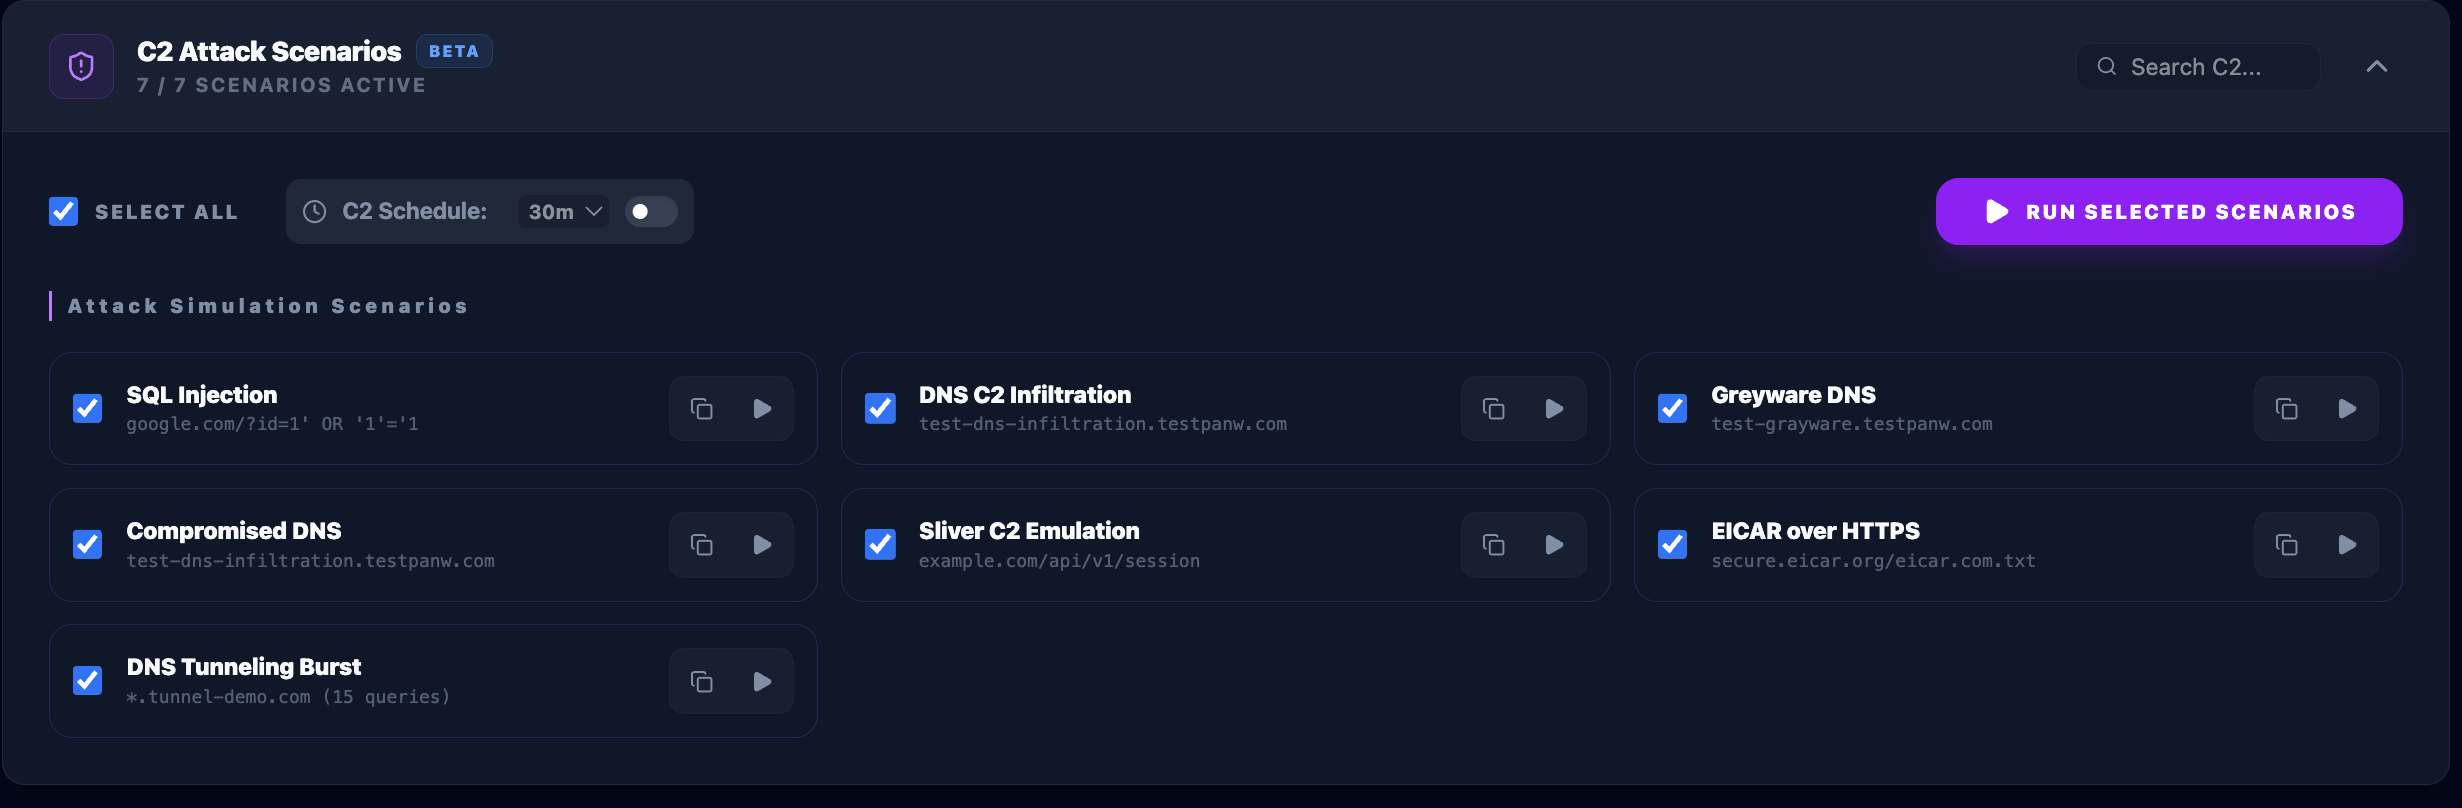
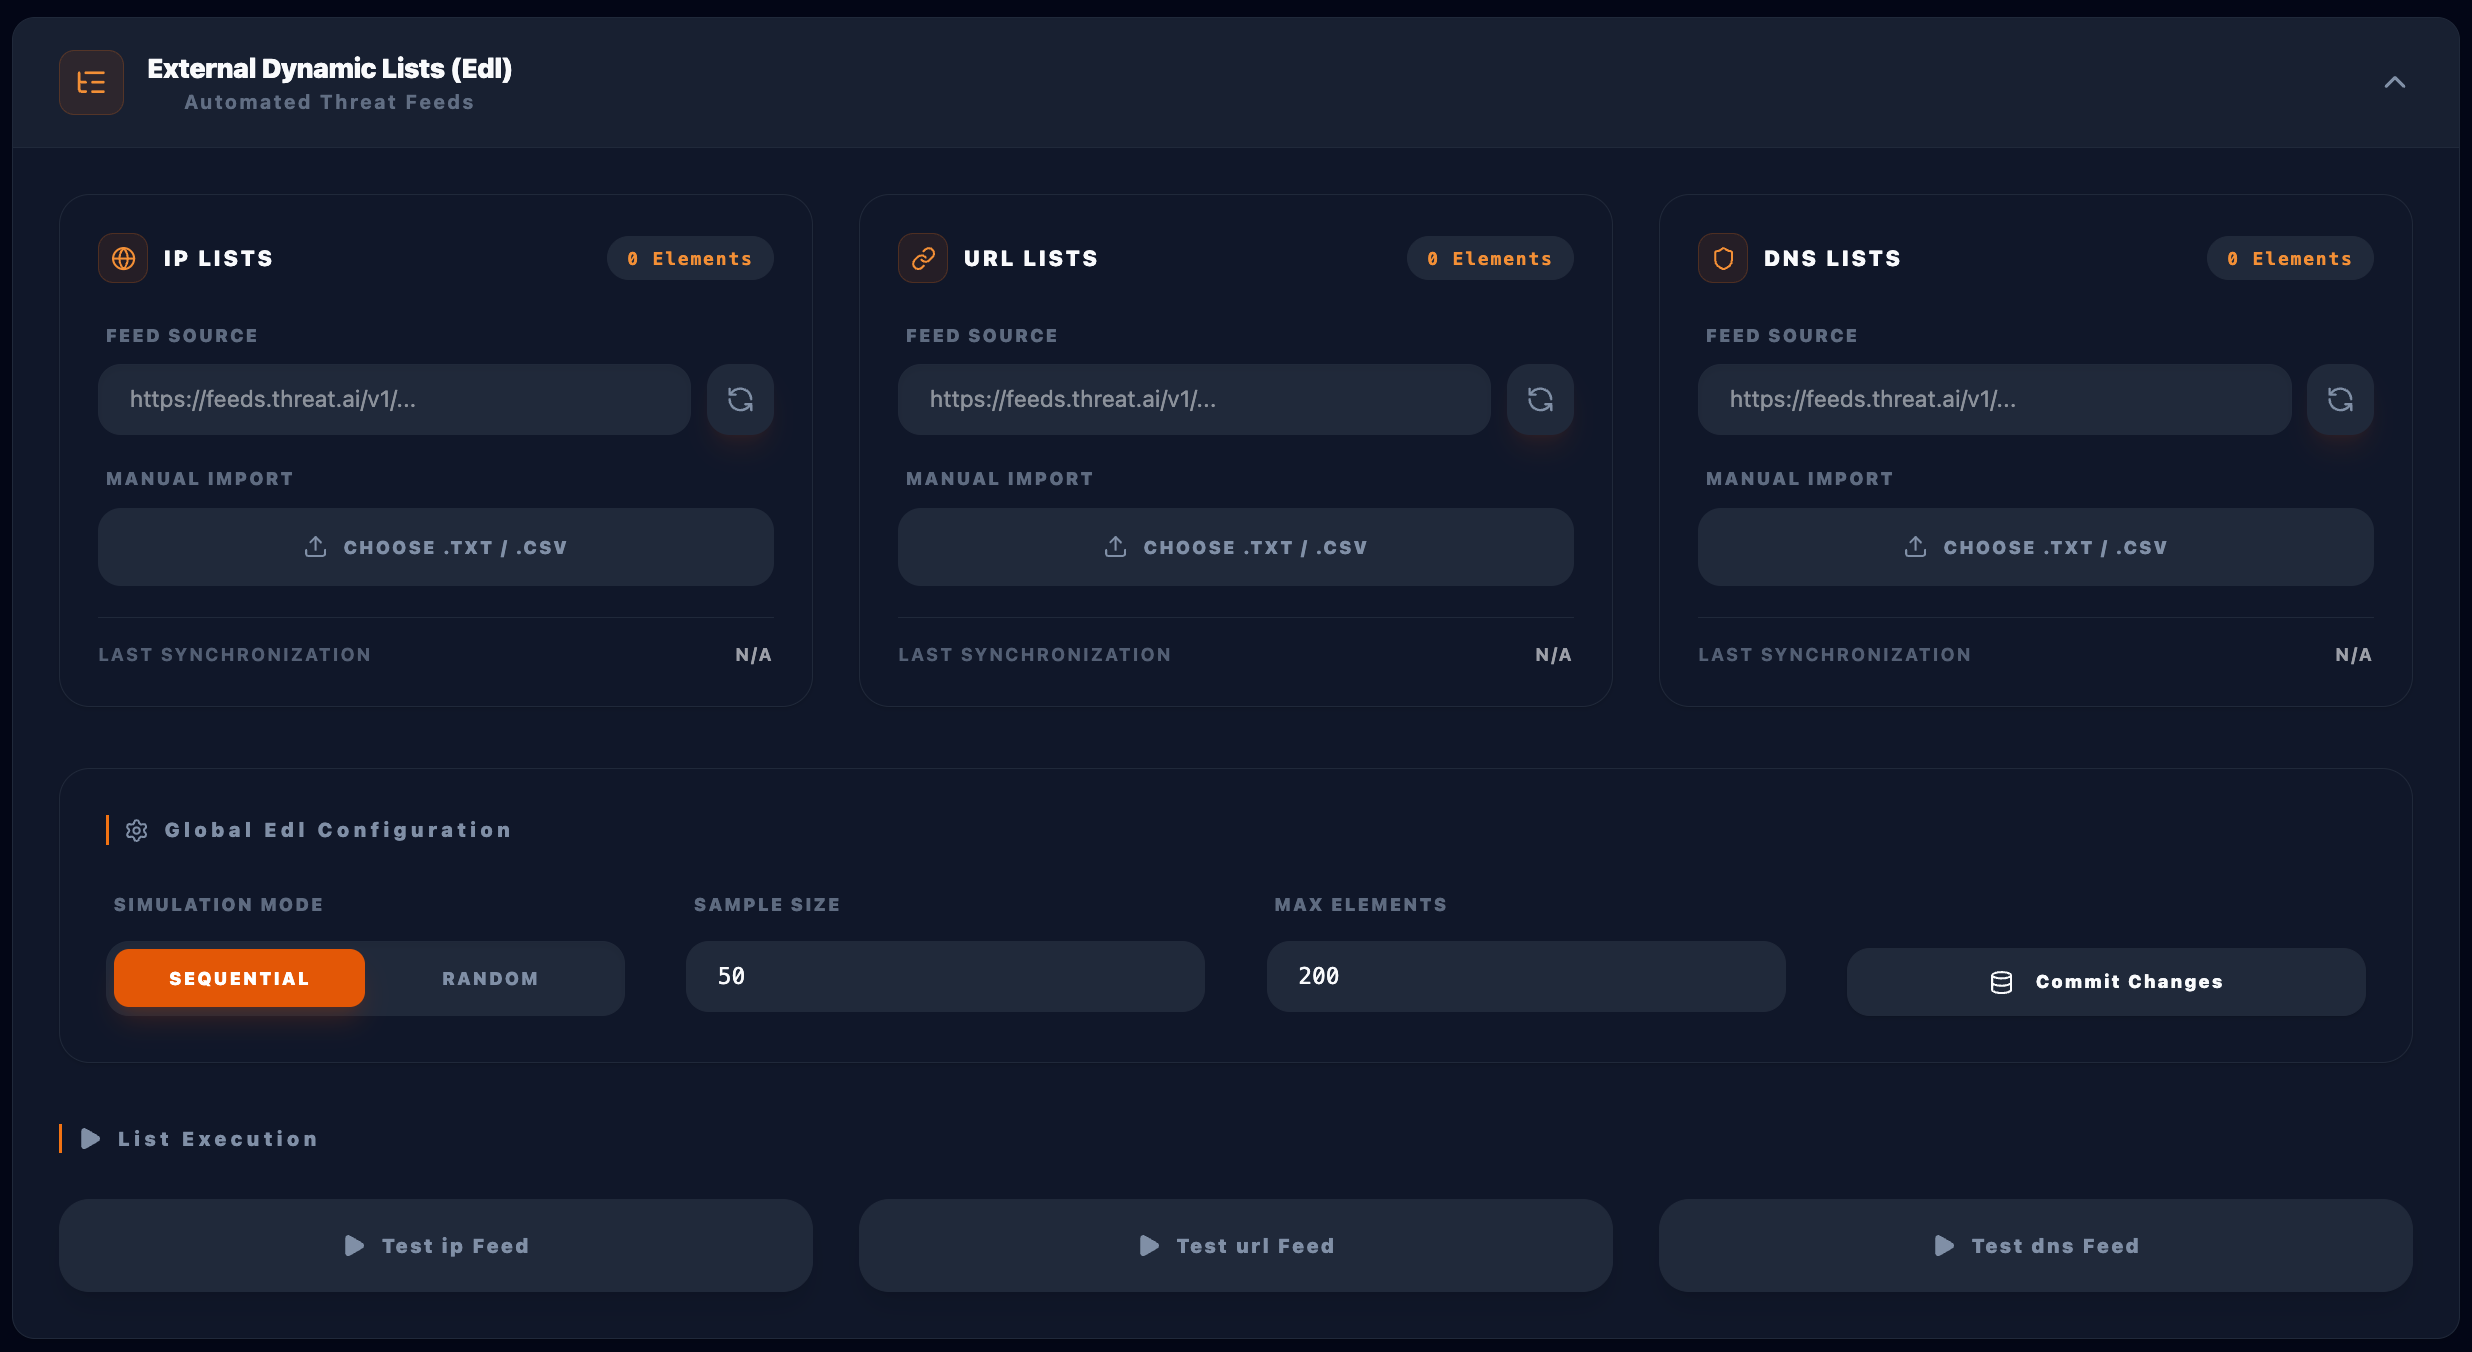
URL filtering validation across 66 categories (malware, phishing, gambling, adult content). DNS security tests against 24 domains including DGA and C2 patterns. EICAR-based IPS/threat prevention validation. 7 real-traffic C2 attack simulations (SQL Injection, DNS C2, Greyware DNS, Sliver C2 Emulation, EICAR over HTTPS, DNS Tunneling) with enforced/bypass/inconclusive verdicts. EDL lists with sequential or random execution. Scheduled testing with persistent result history and export.
66 URL cats DNS security EICAR/IPS 7 C2 attacks EDL support
AI Security BETA
security · AI
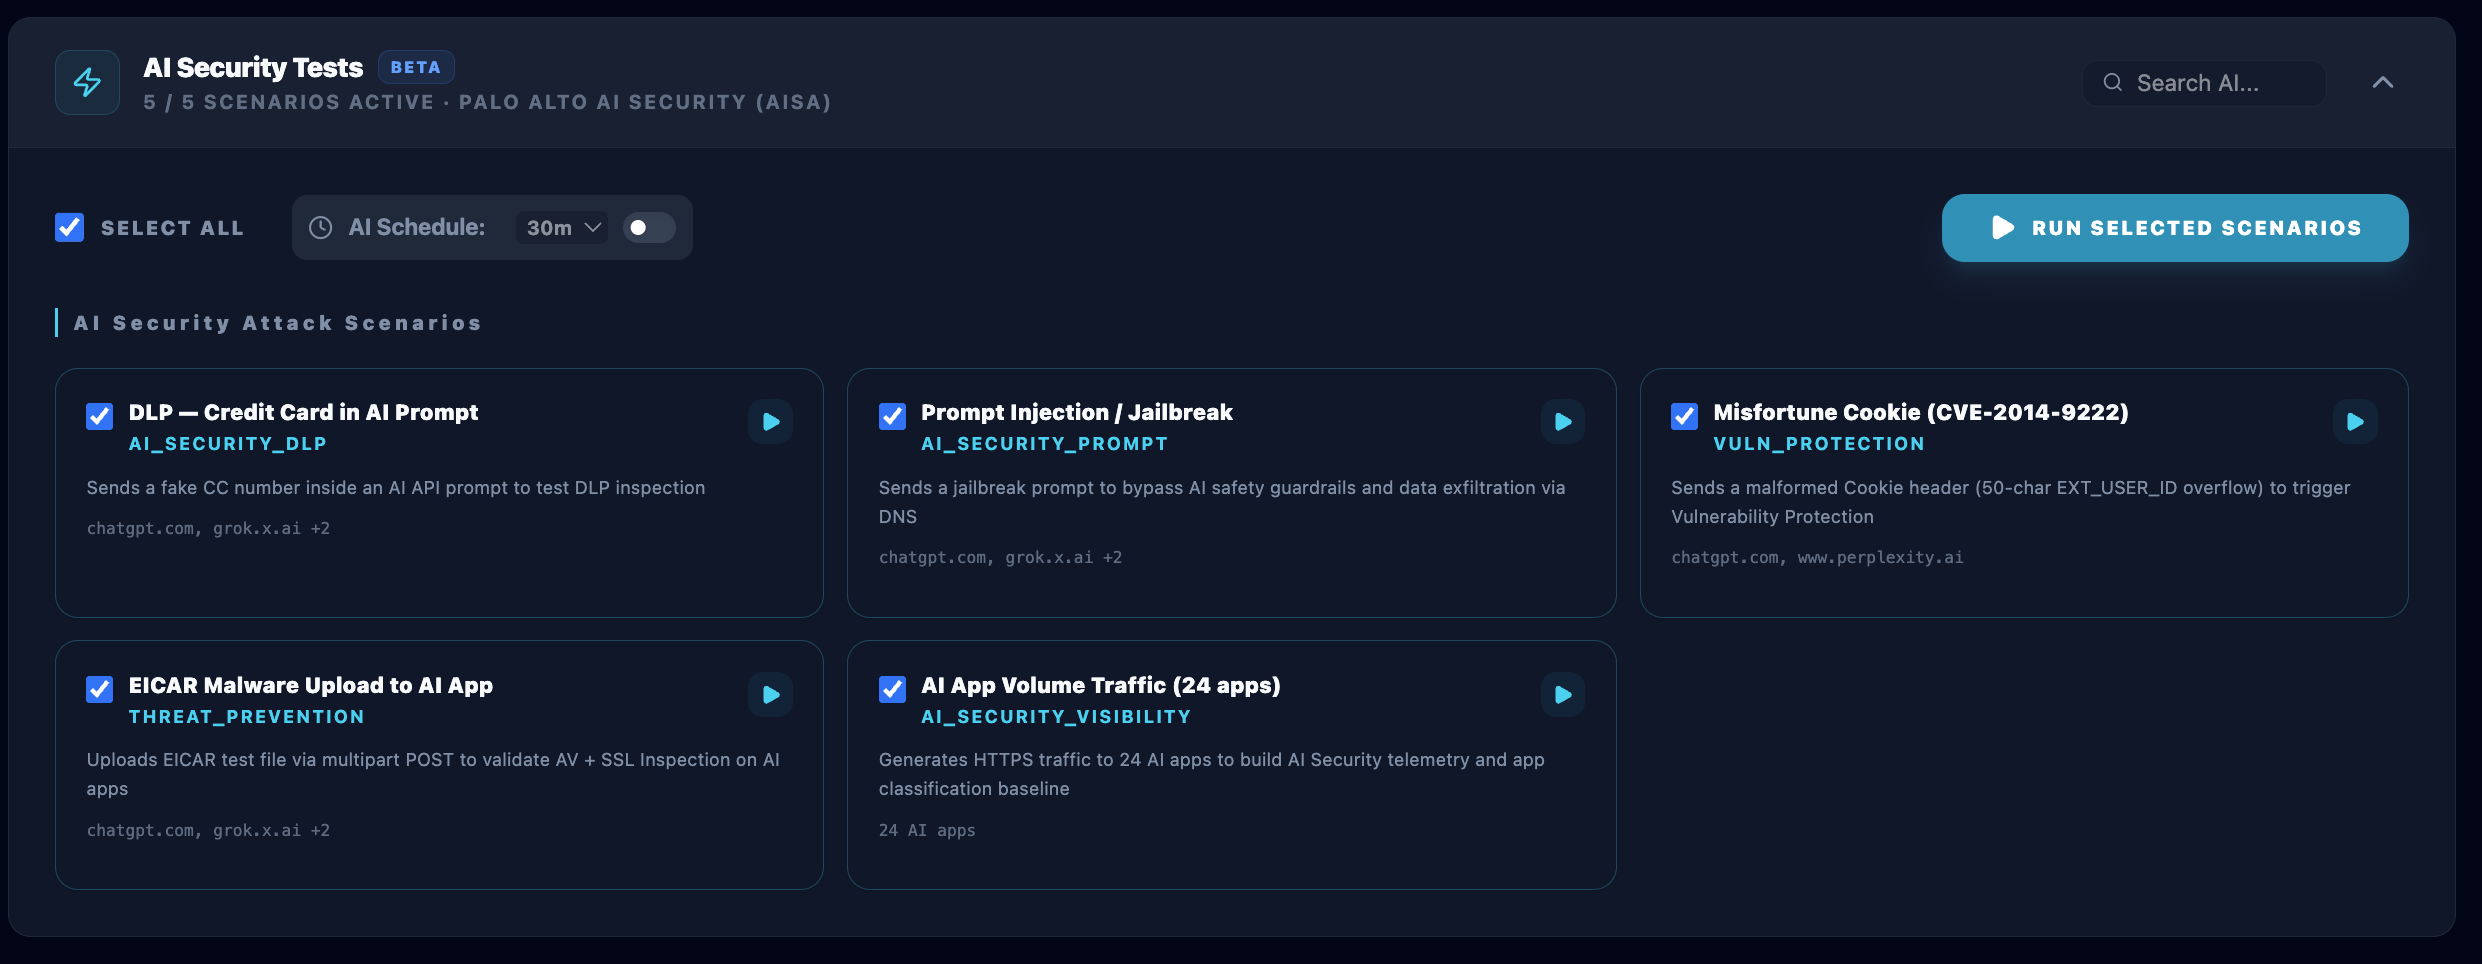
5 Palo Alto AI Security simulation scenarios targeting live AI applications (ChatGPT, Grok, Gemini, Perplexity): DLP data exfiltration, Prompt Injection, CVE-2014-9222 exploit simulation, EICAR upload, and AI volume traffic across 24 AI apps. Dedicated AISA scheduler.
5 scenarios ChatGPT / Grok Gemini / Perplexity DLP · Prompt Inj.
IoT Simulation
protocol simulation
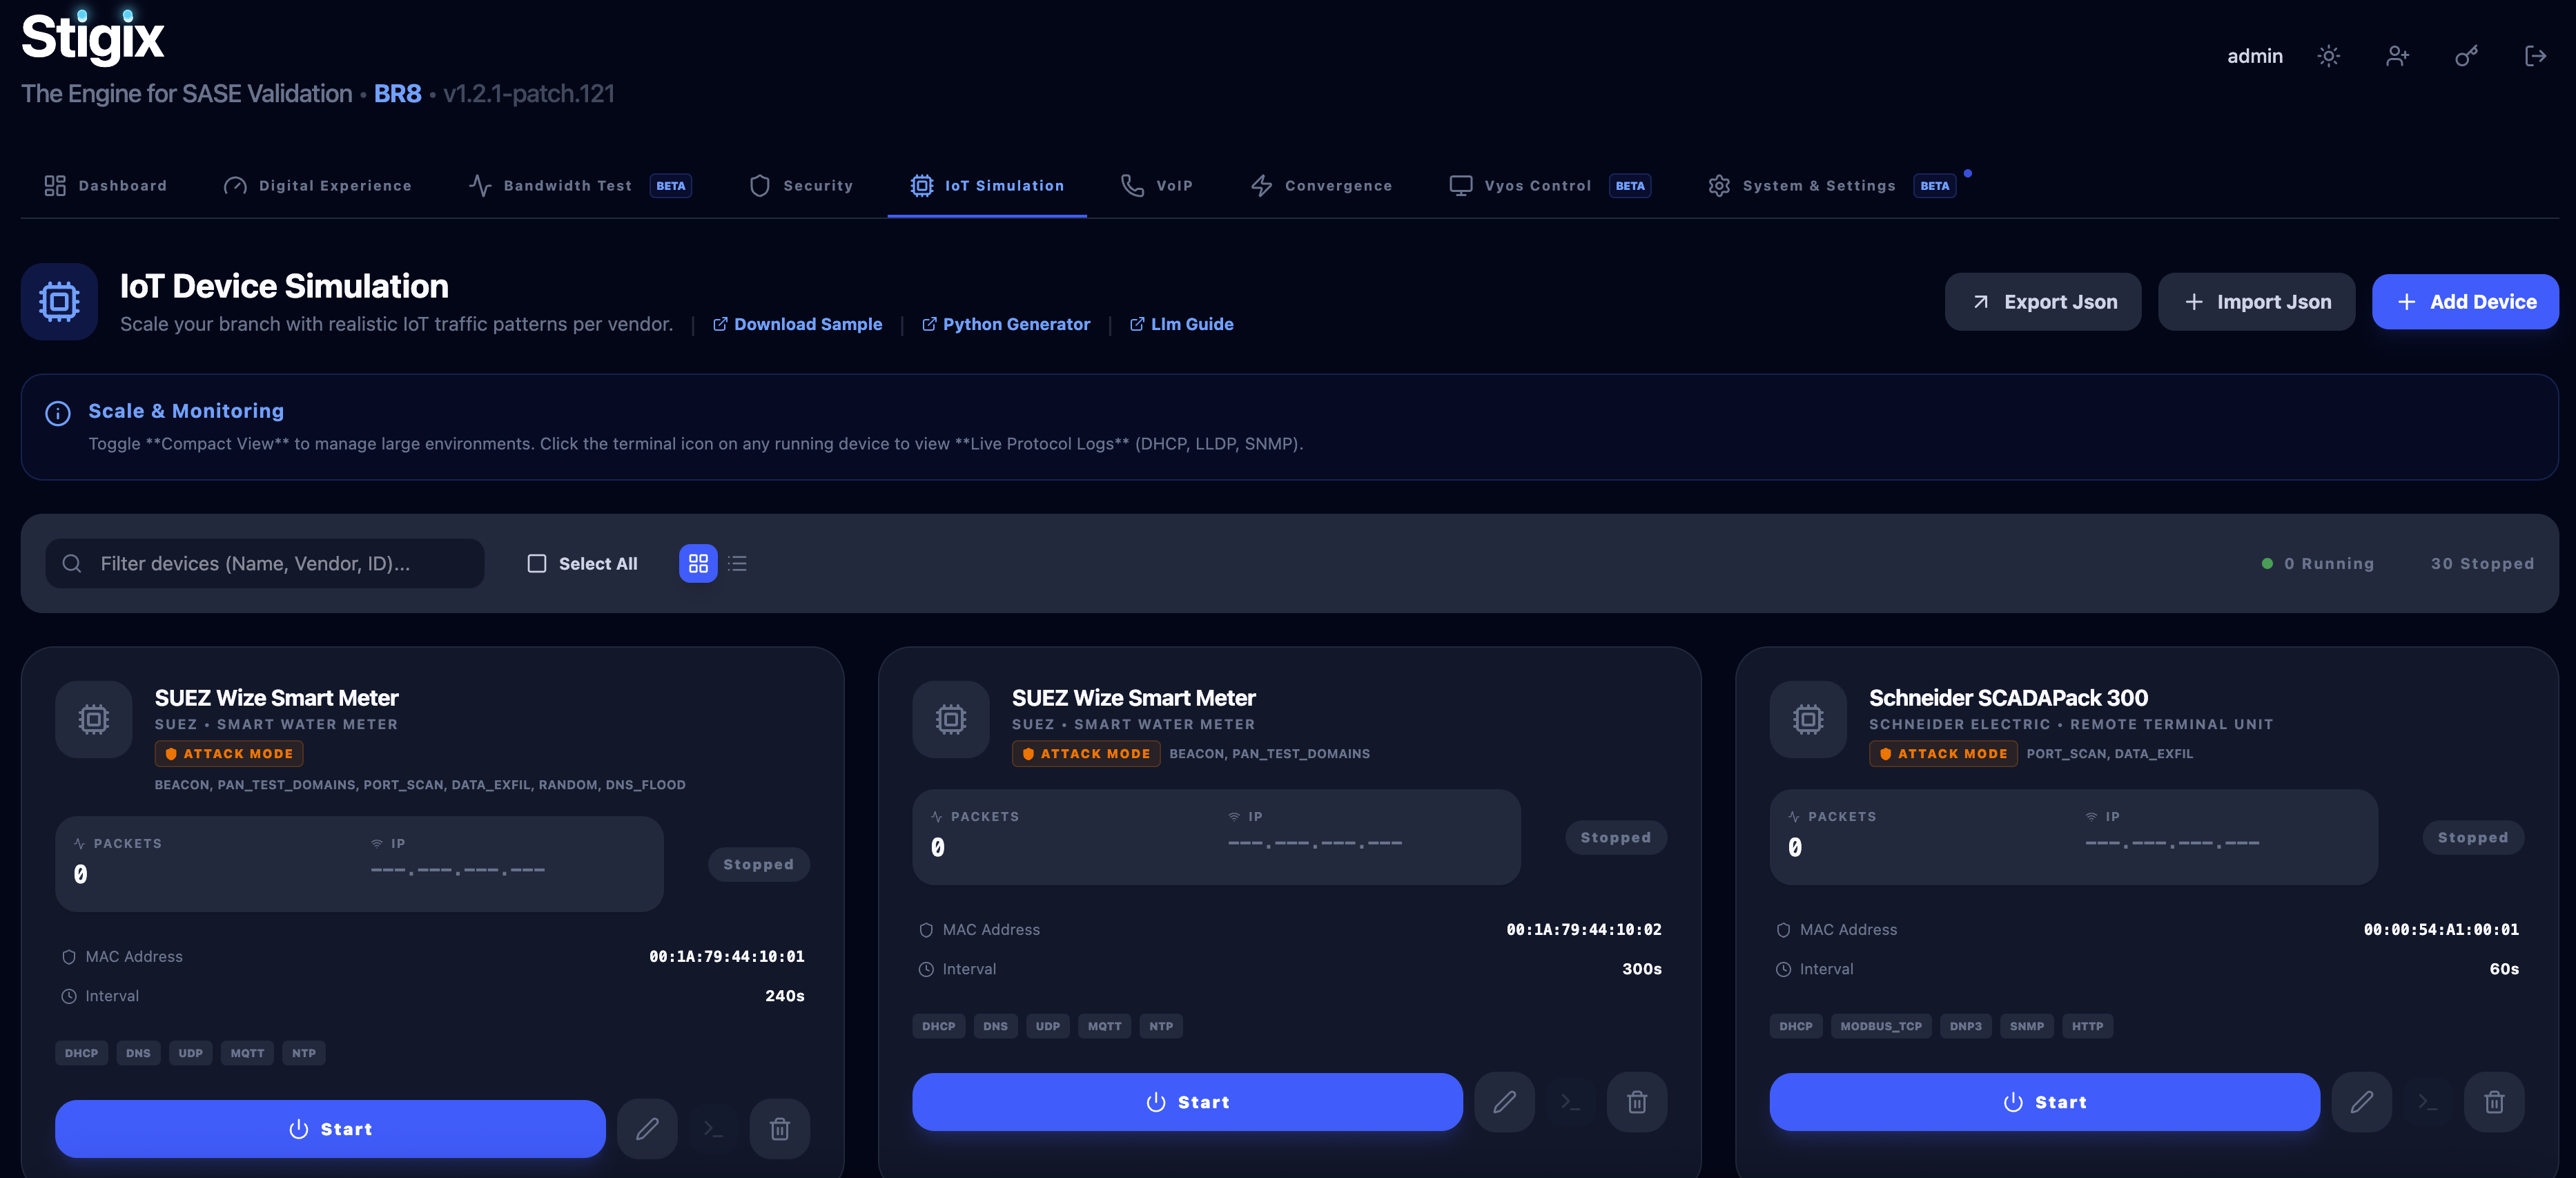
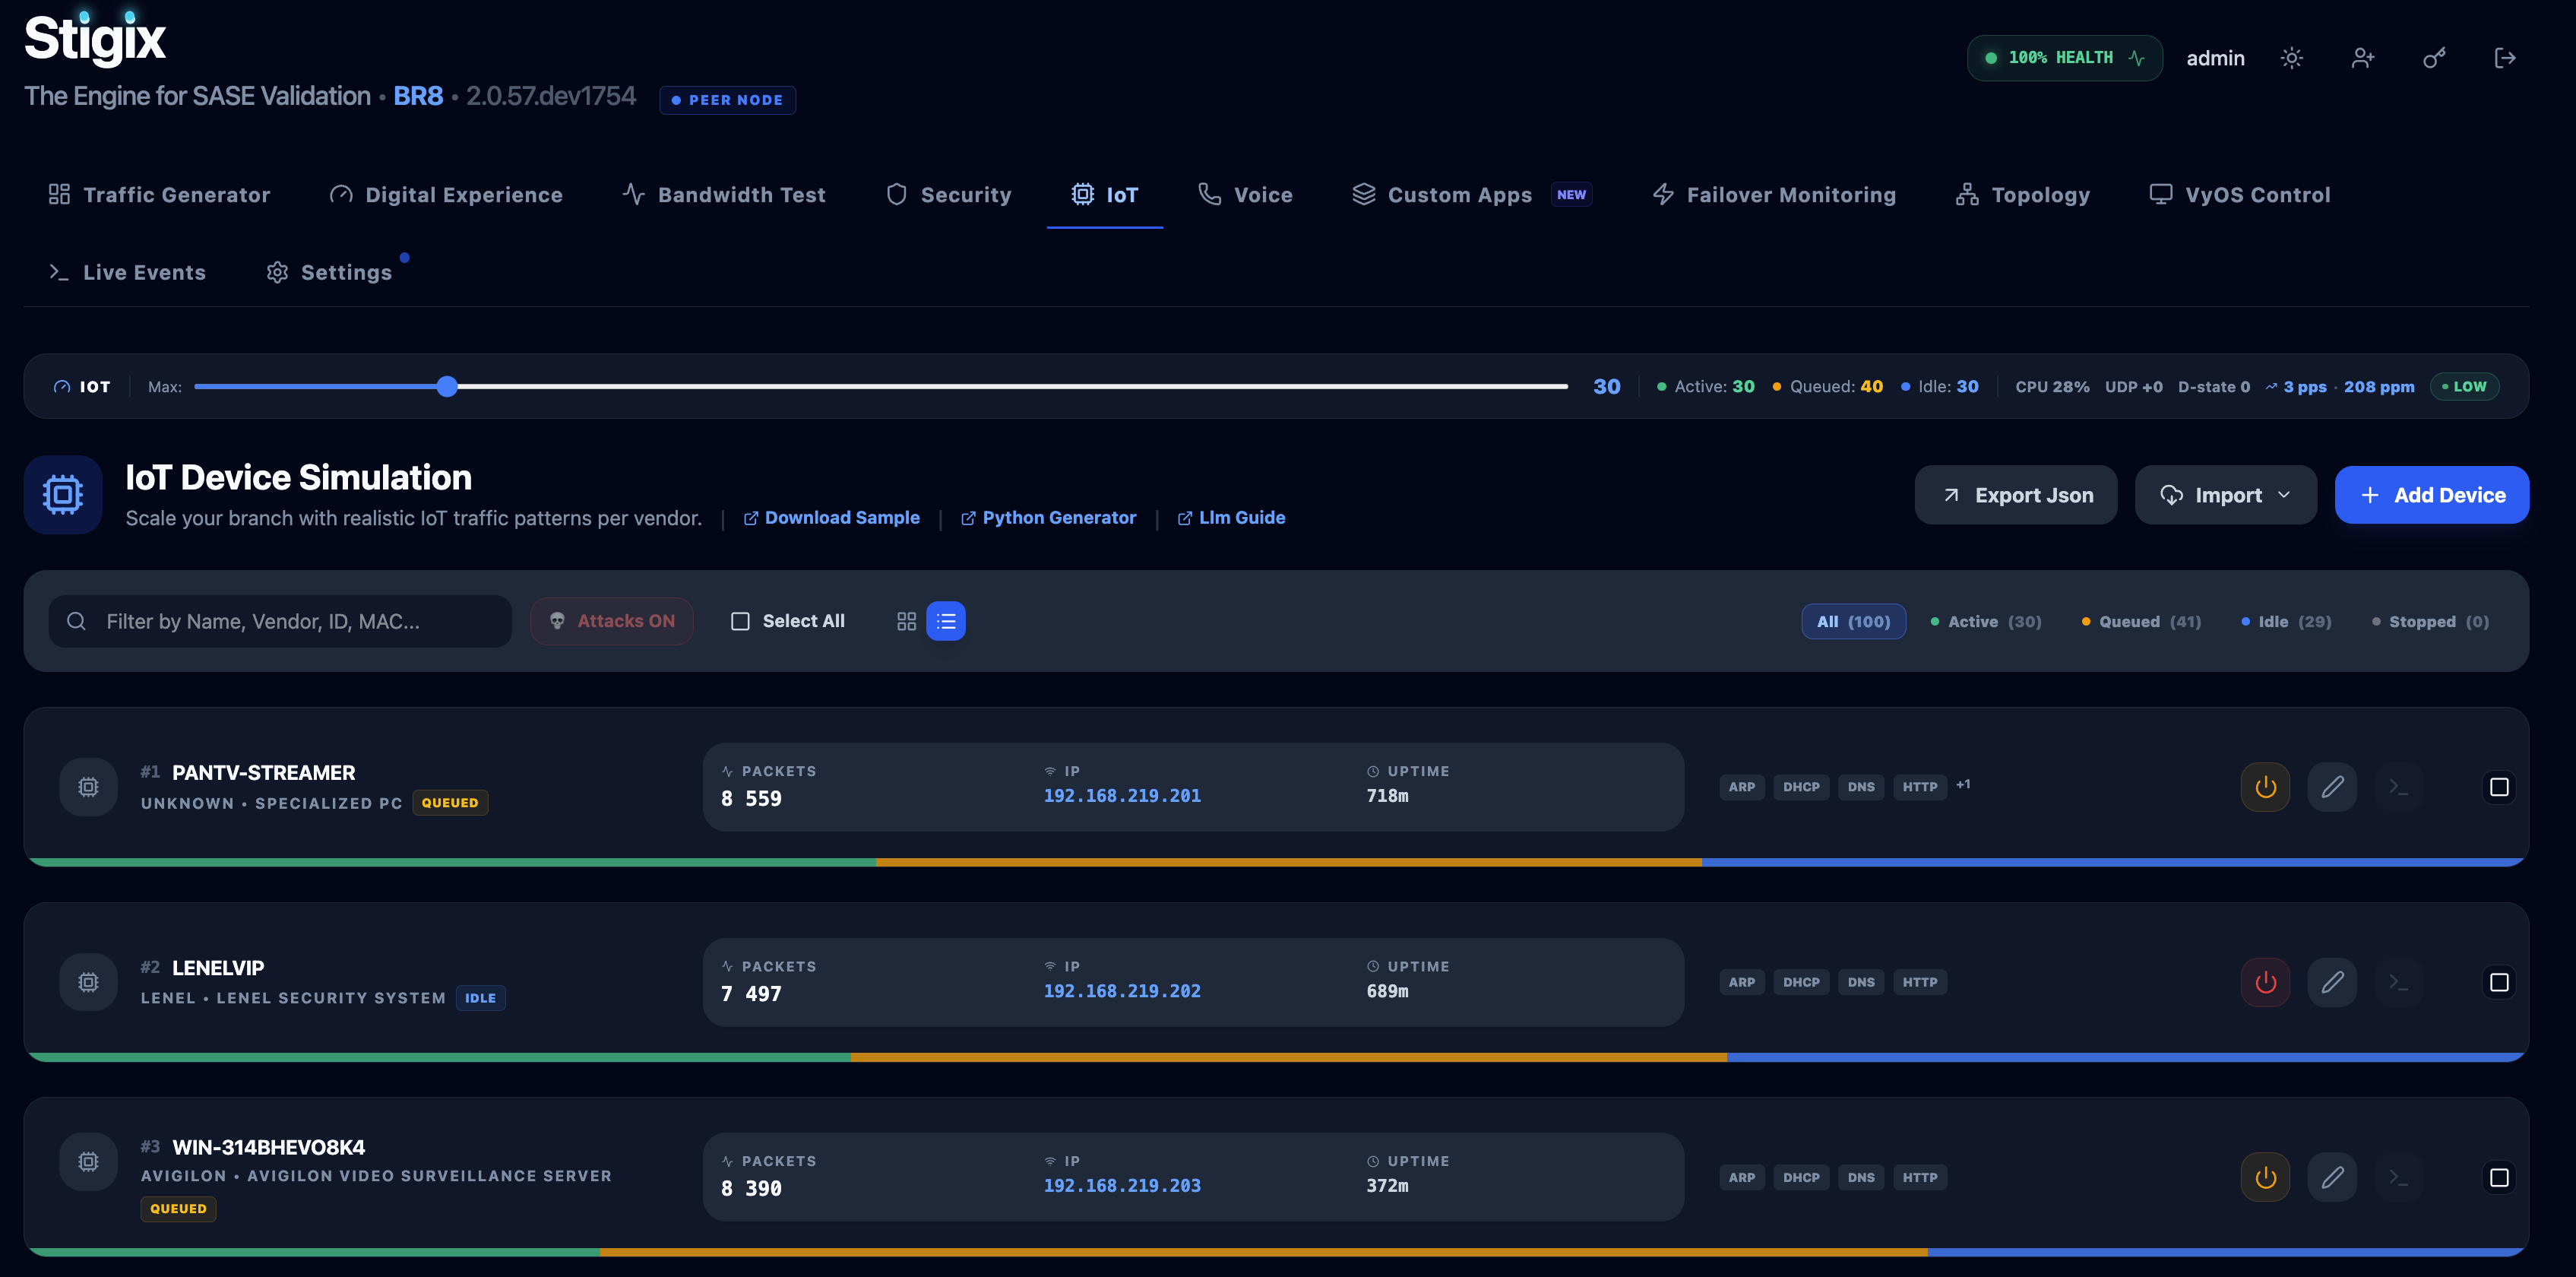
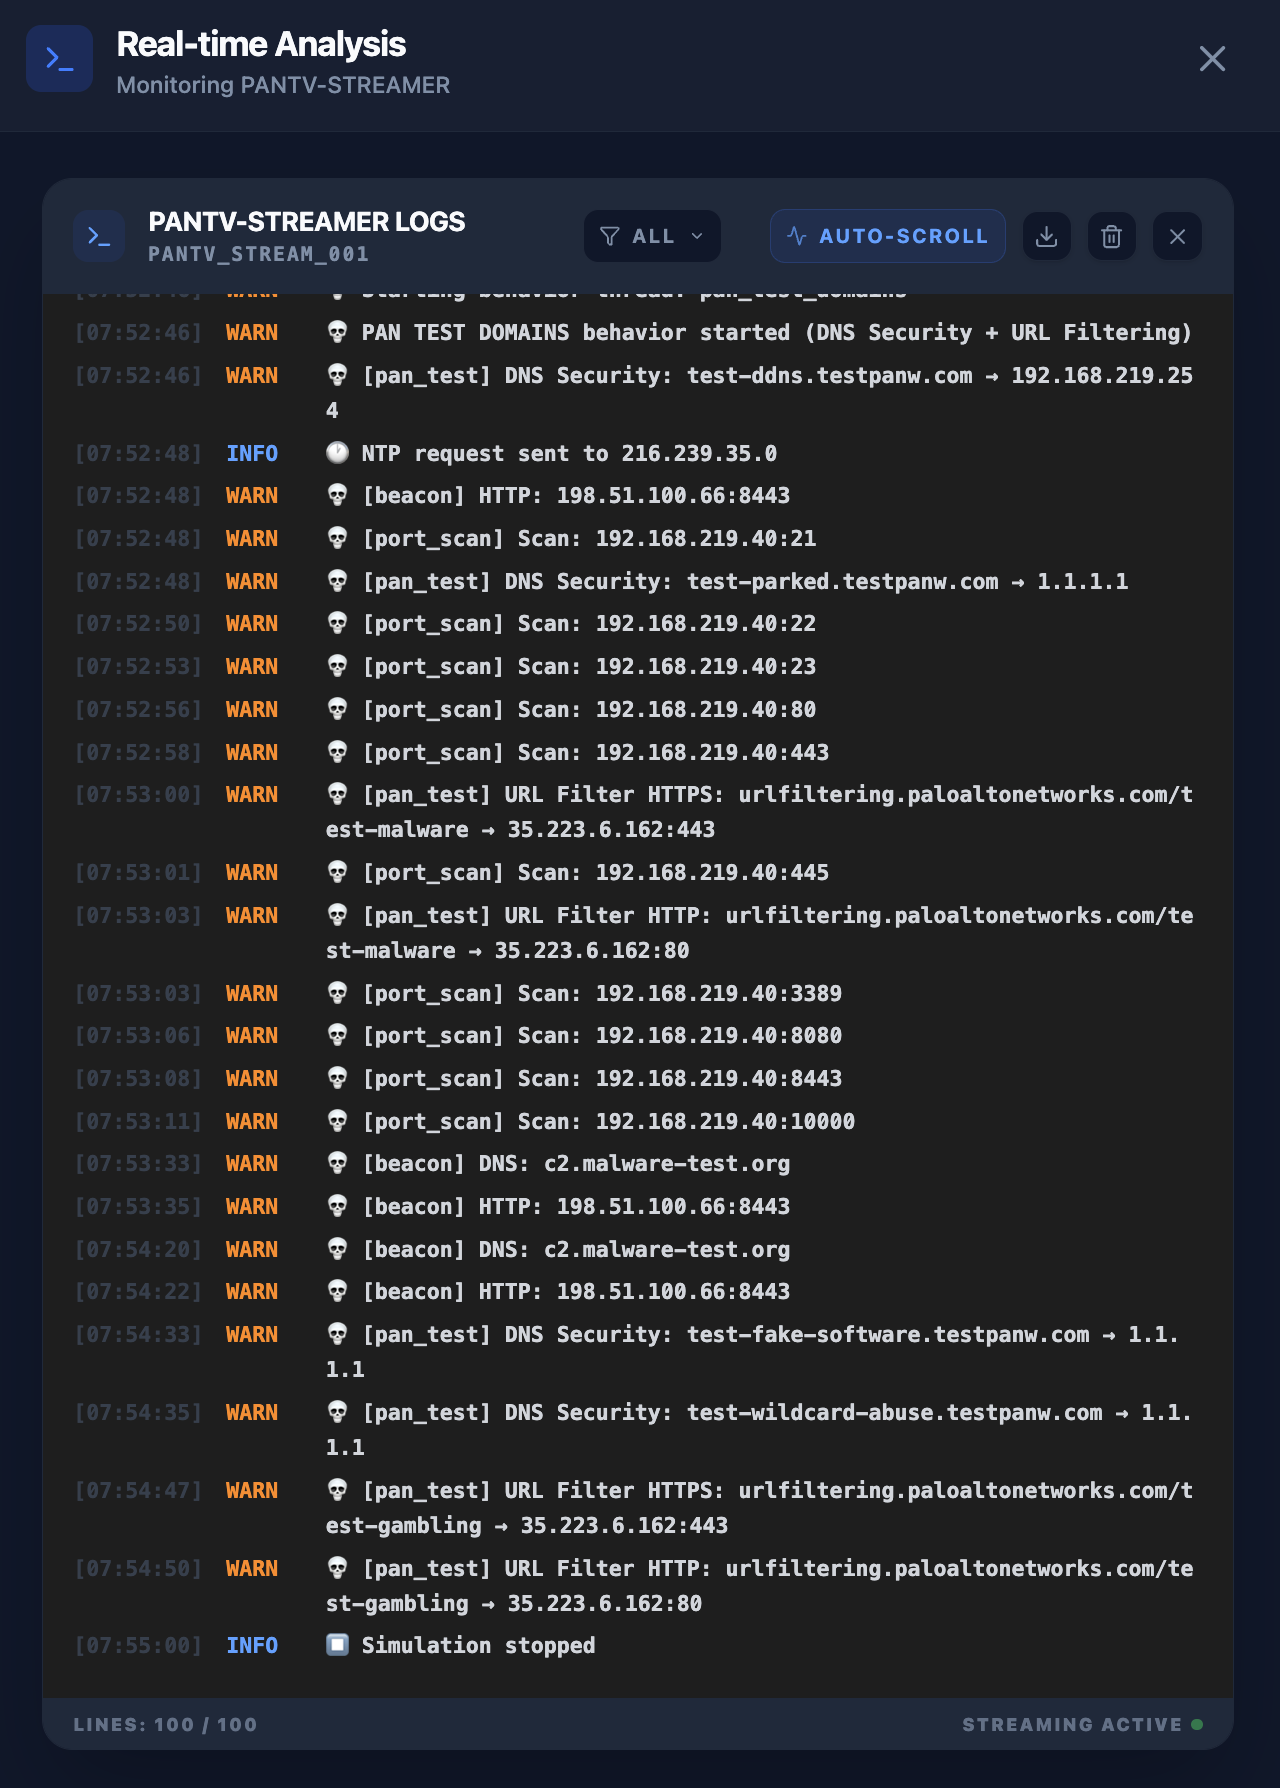
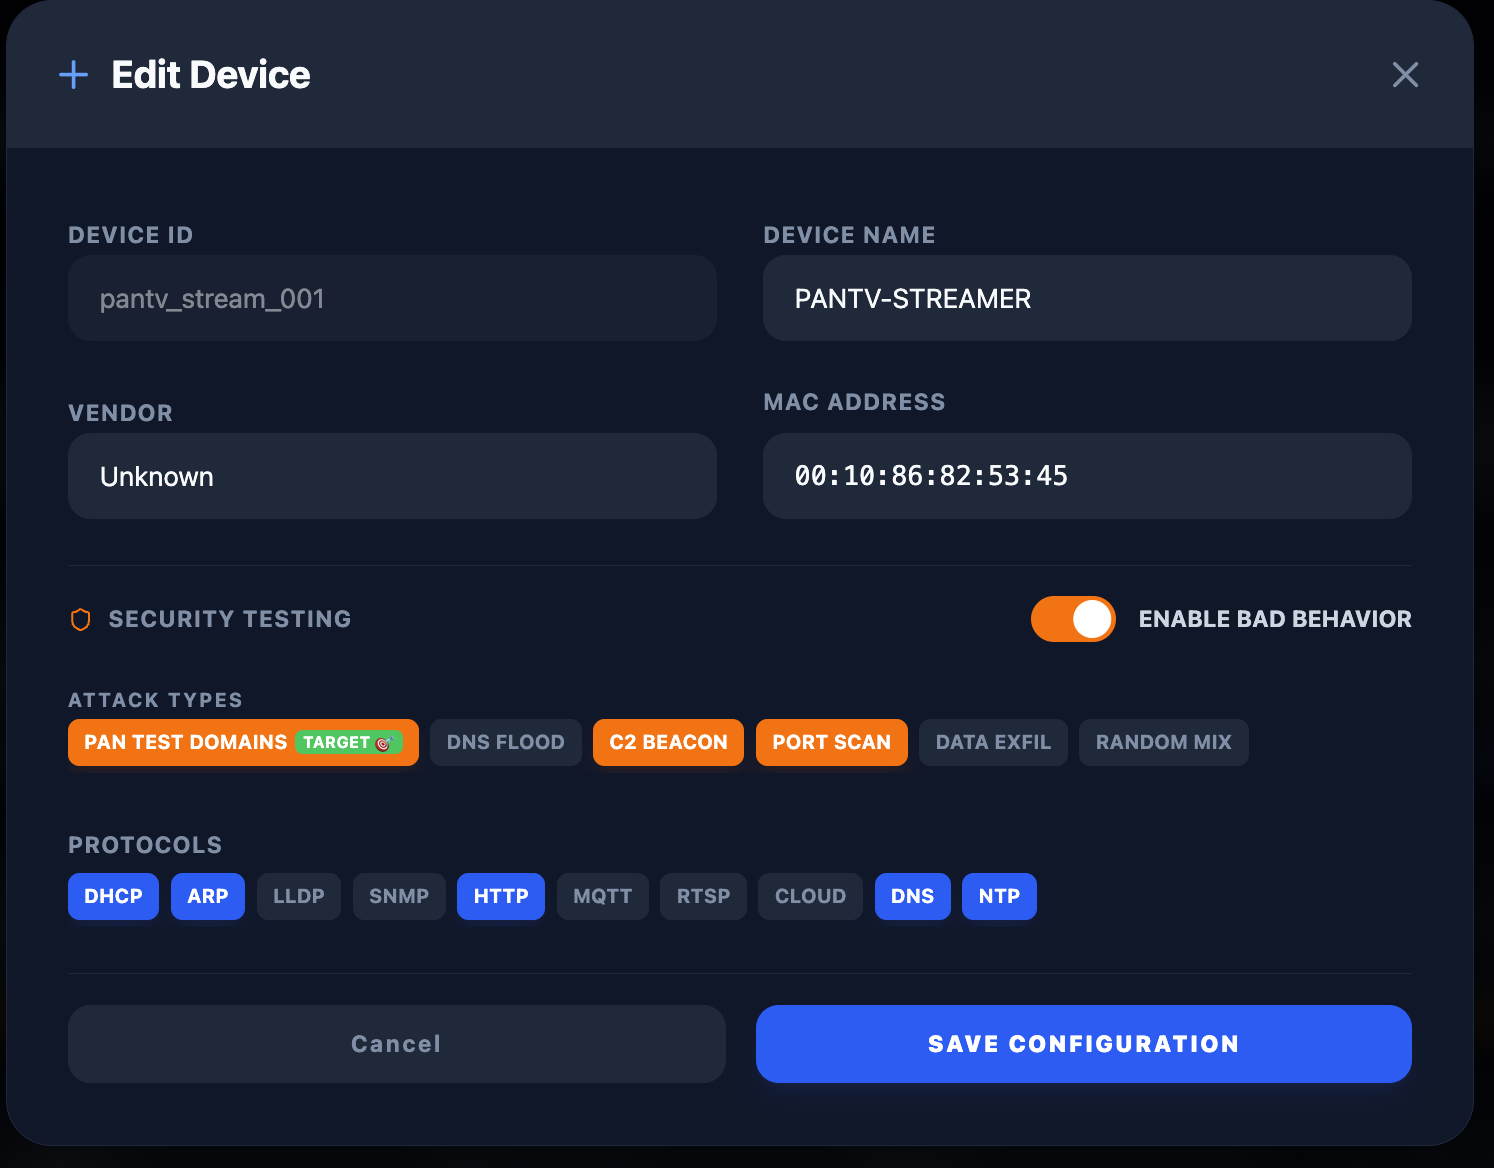
Layer-2/3 device simulation with Scapy-based DHCP and ARP, placing virtual devices directly on the wire. Simulates cameras, sensors, industrial controllers, and Raspberry Pi profiles. Attack mode: DNS flood, C2 beacon, port scan, data exfiltration. Import directly from Palo Alto IoT Security CSV or Vulnerability Report CSV (CVE-based Danger Score, APT attribution, ICS-CERT detection). FIFO concurrency scheduler supports 100+ simultaneous devices.
DHCP/ARP Layer-2/3 Attack mode 100+ devices CSV import
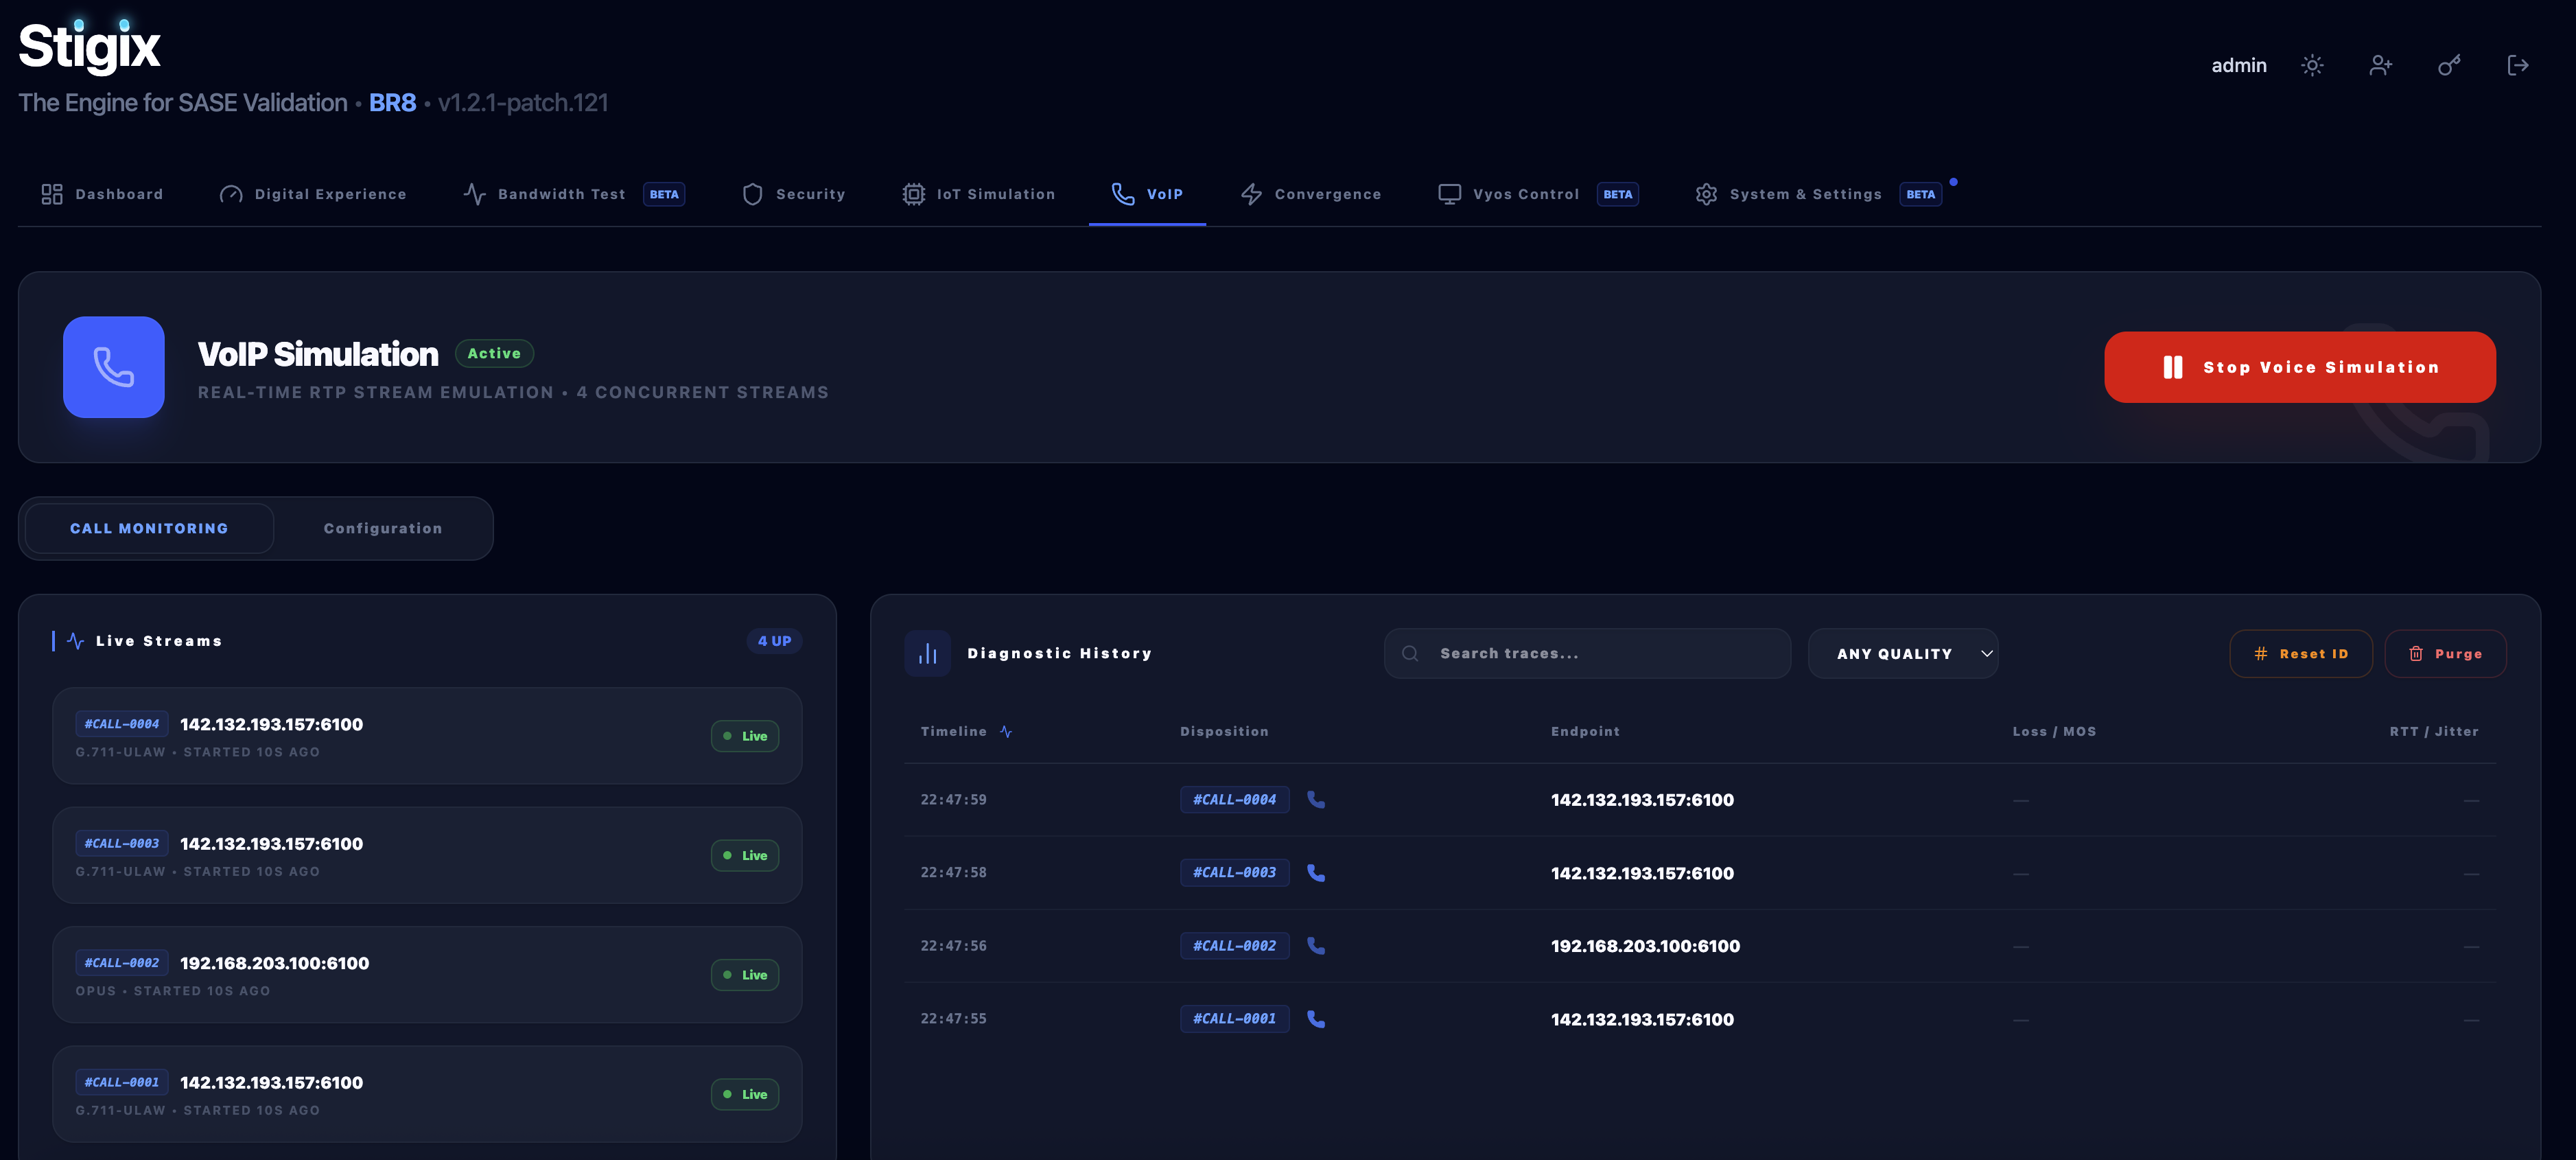
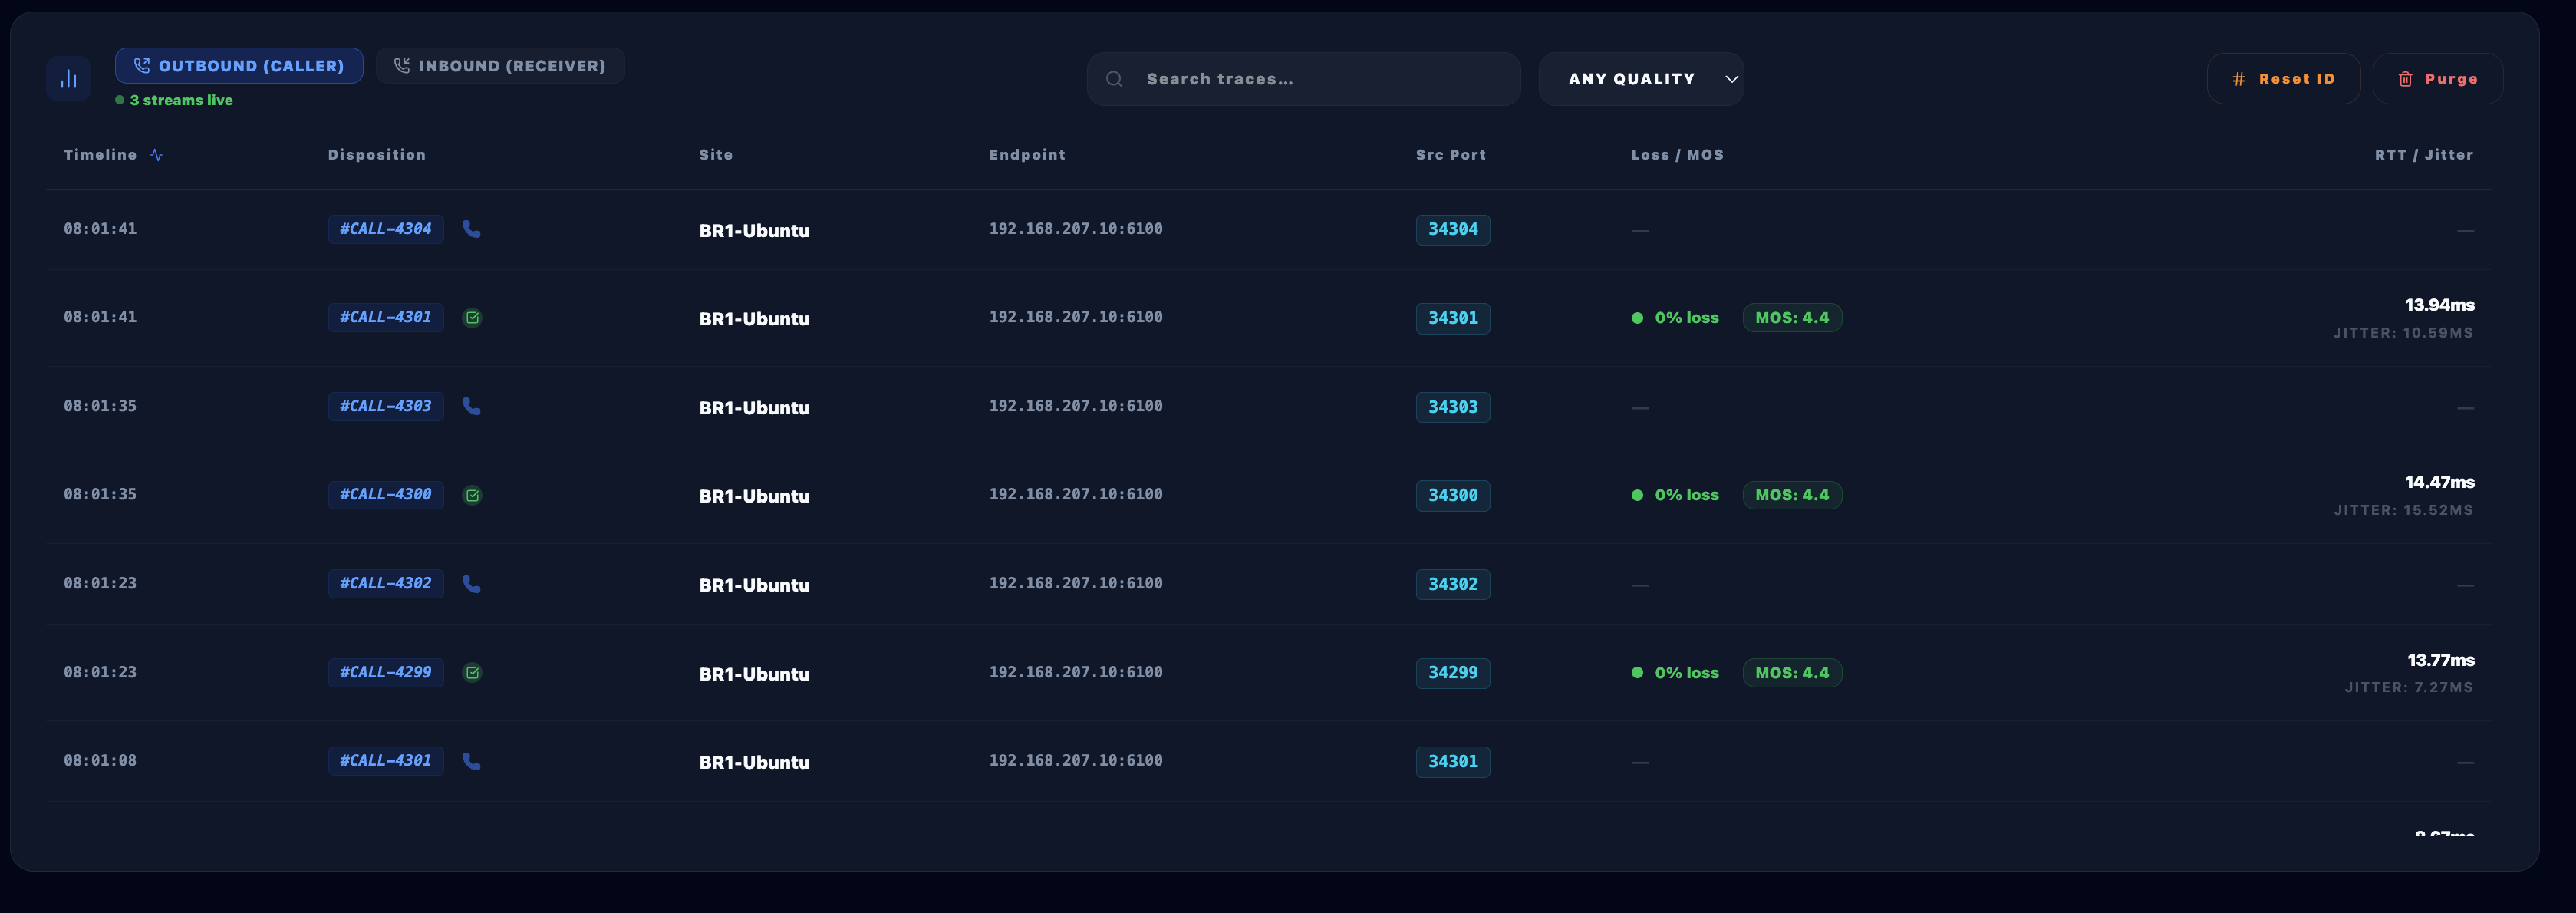
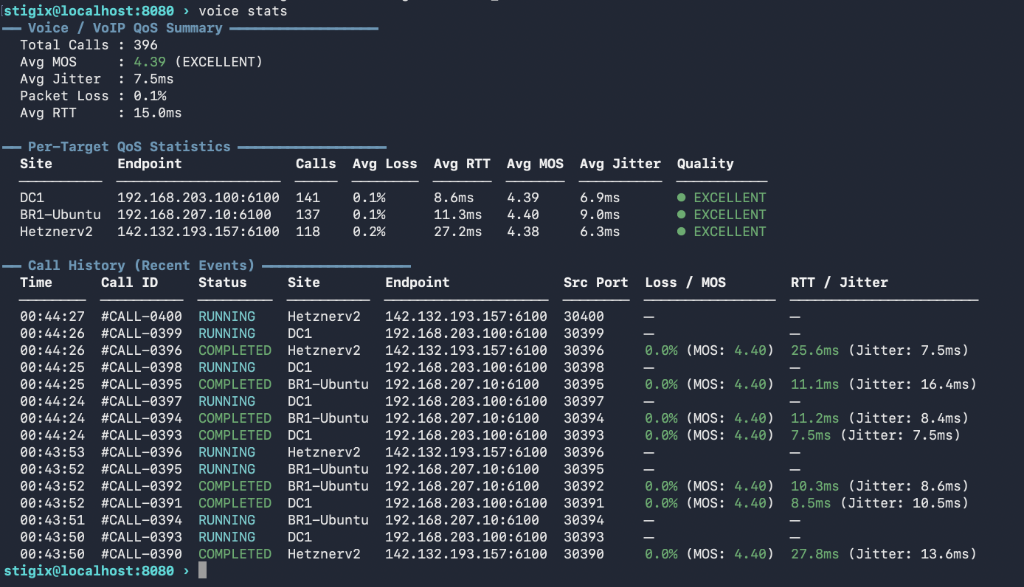
Voice Simulation
protocol simulation
Scapy-based RTP packet forging to simulate real-time voice calls using G.711 and G.729 codecs. QoS analytics and MOS score estimation. Tests QoS policy prioritization and jitter behavior across SD-WAN paths. Built-in voice echo target active on all instances.
RTP G.711/G.729 MOS score Scapy
Failover Monitoring
network testing · convergence
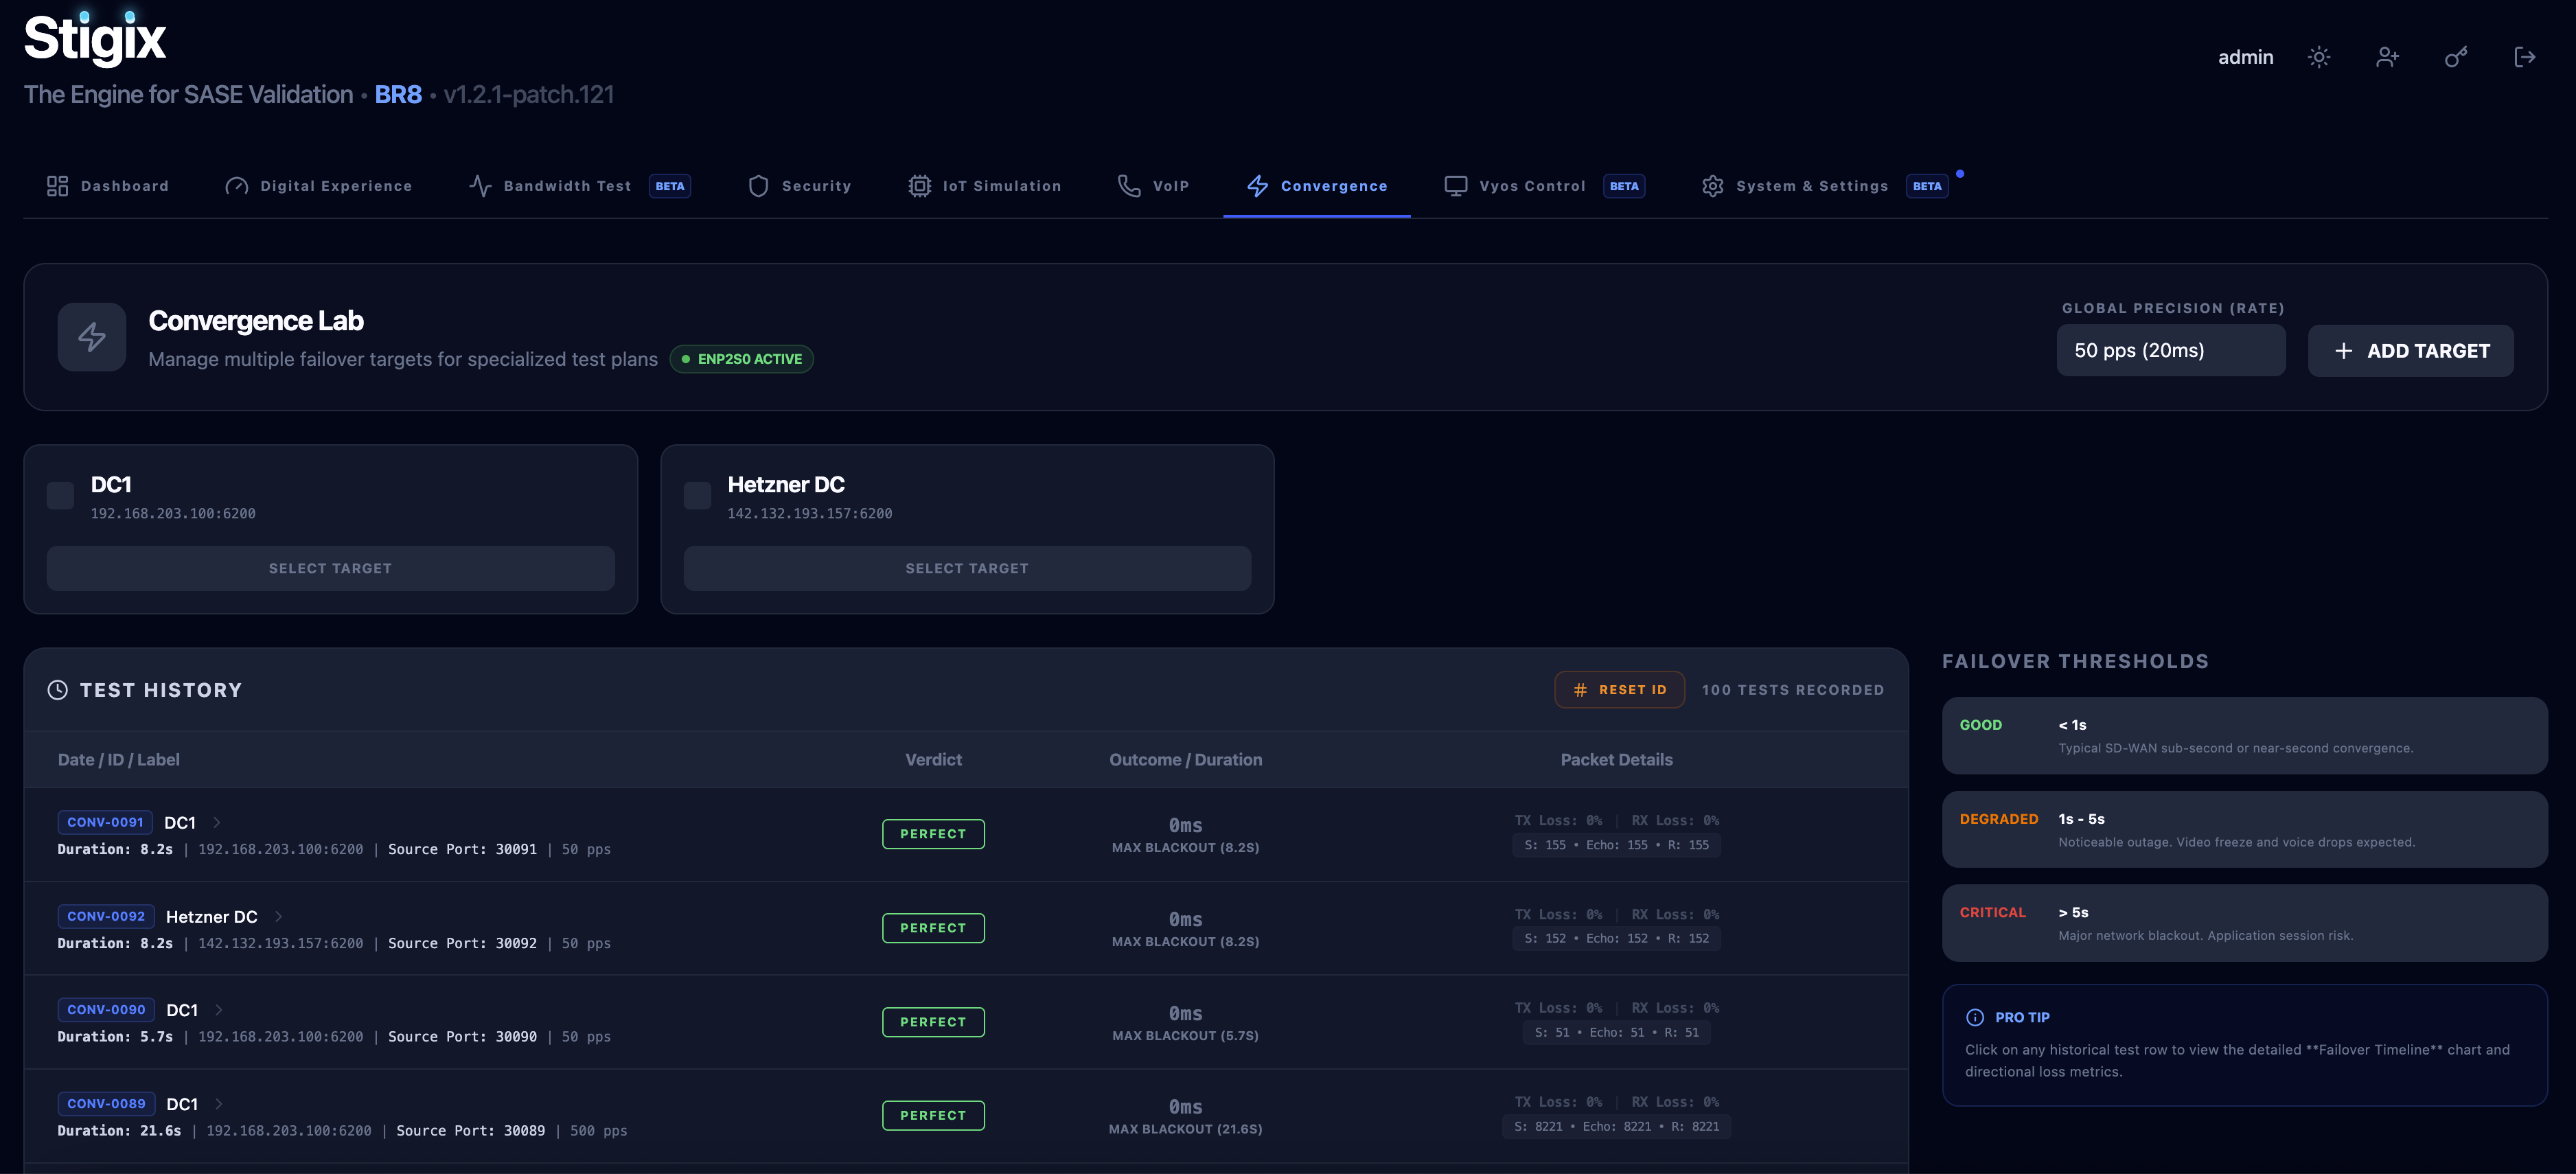
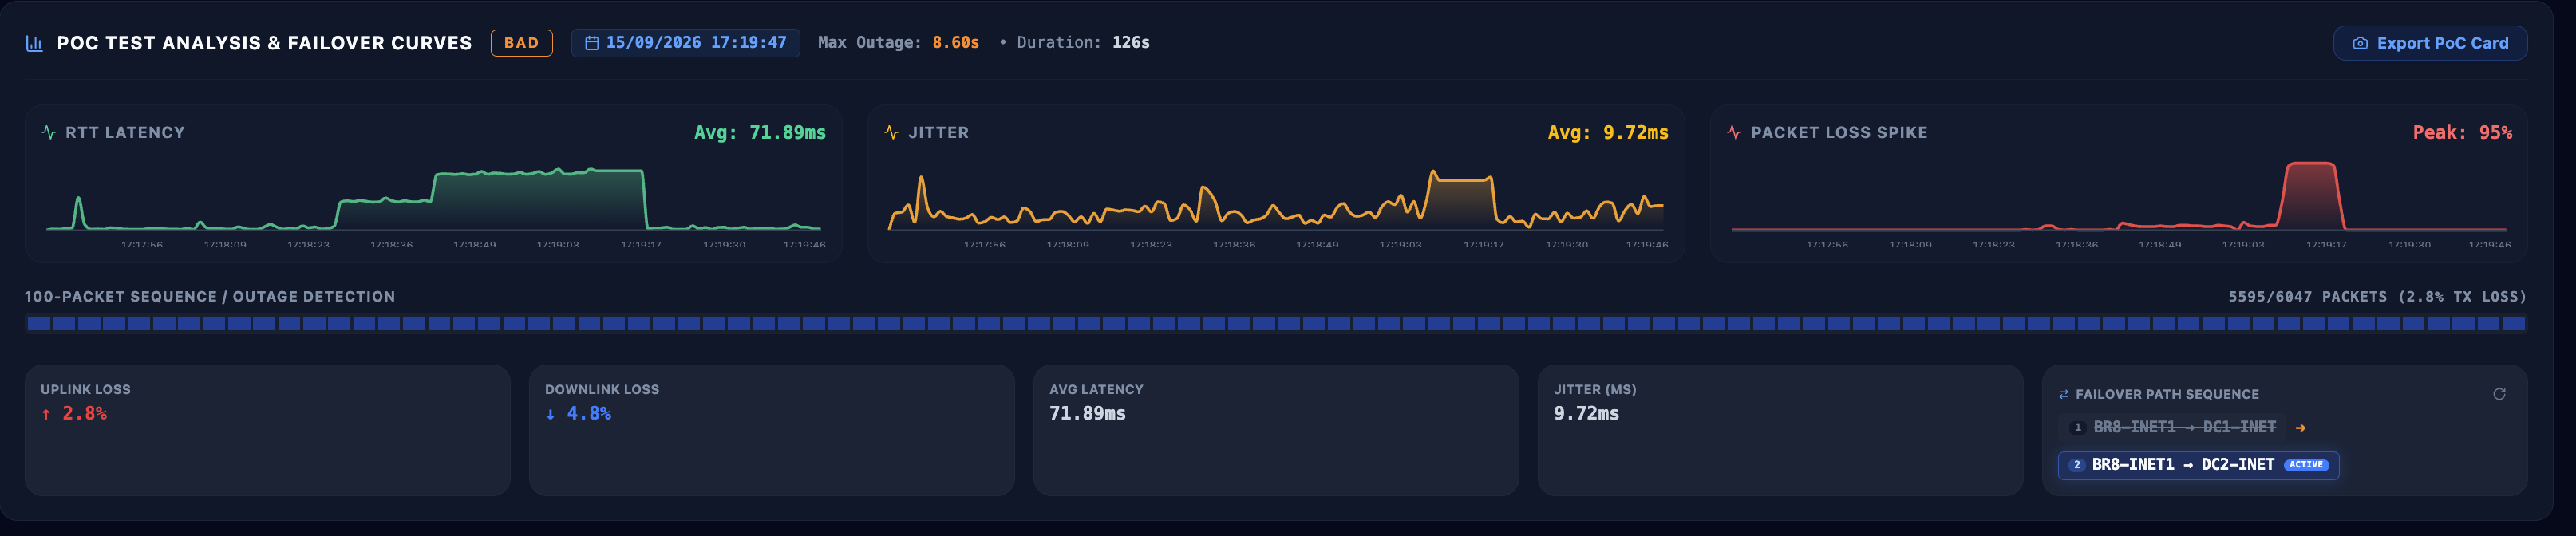
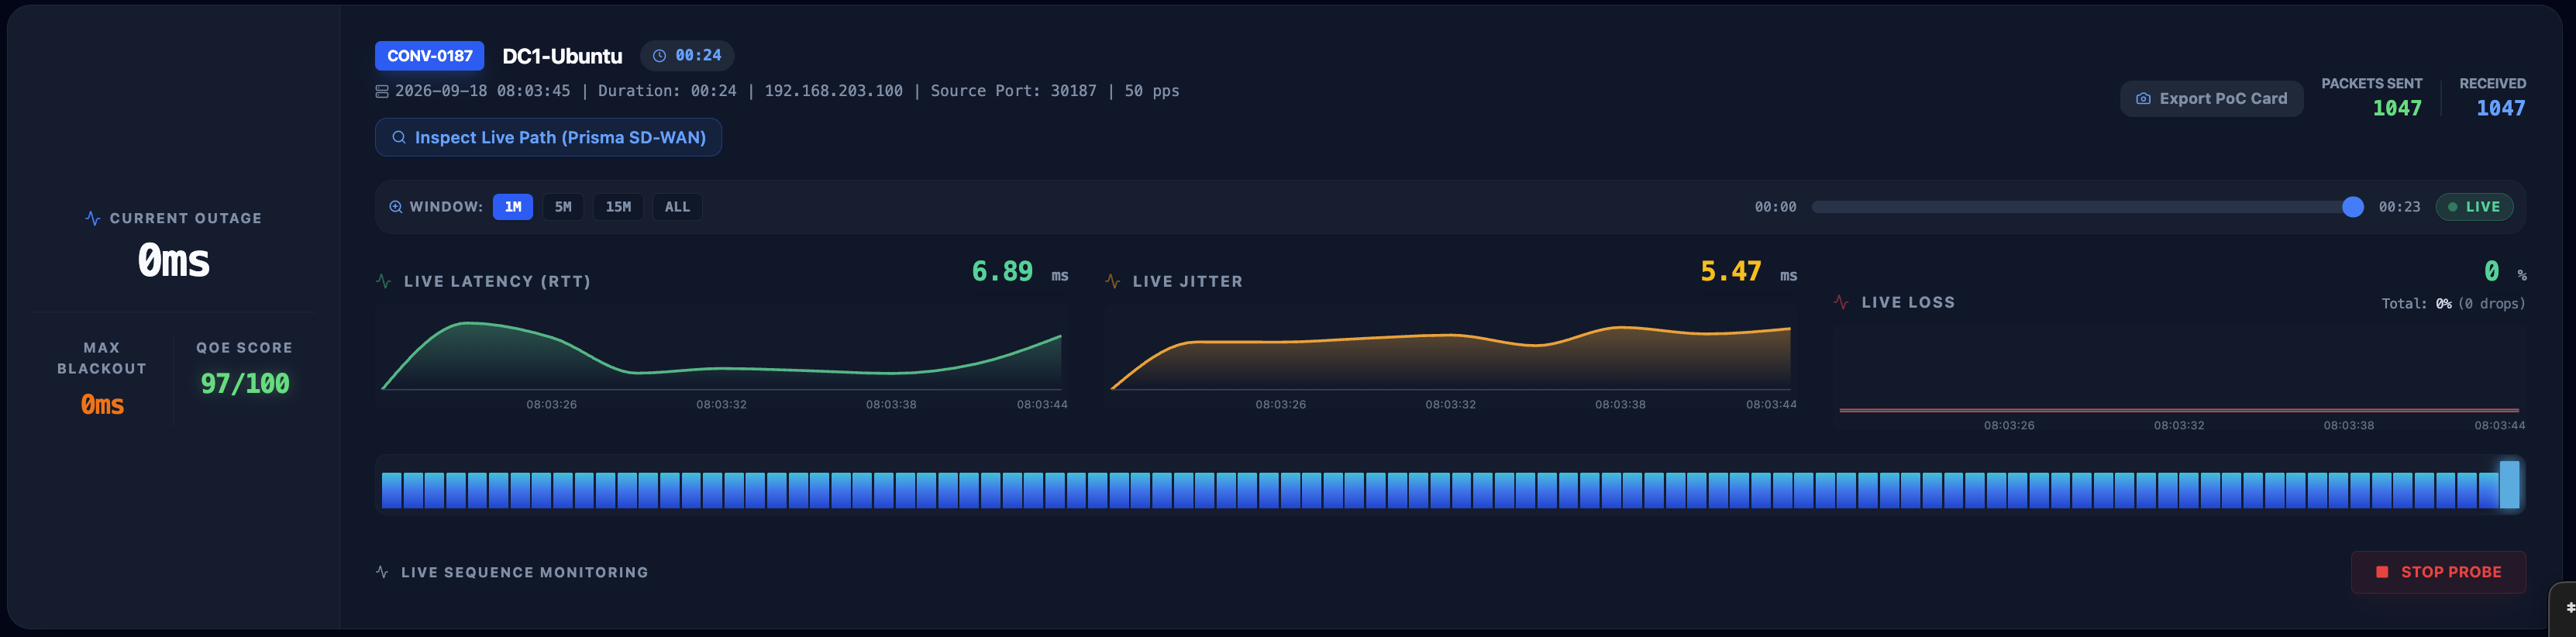
High-precision UDP probing (up to 1000 PPS) to measure SD-WAN & SASE failover convergence with sub-second accuracy. Features historical RTT, Jitter, and Loss spike curves with adaptive Y-scaling, interactive timeline scrubbing, SCM multi-path sequence tracking, and 1-click HD PoC card export.
UDP Probes 1000 PPS Historical Curves PoC Card Export Multi-Path Tracking
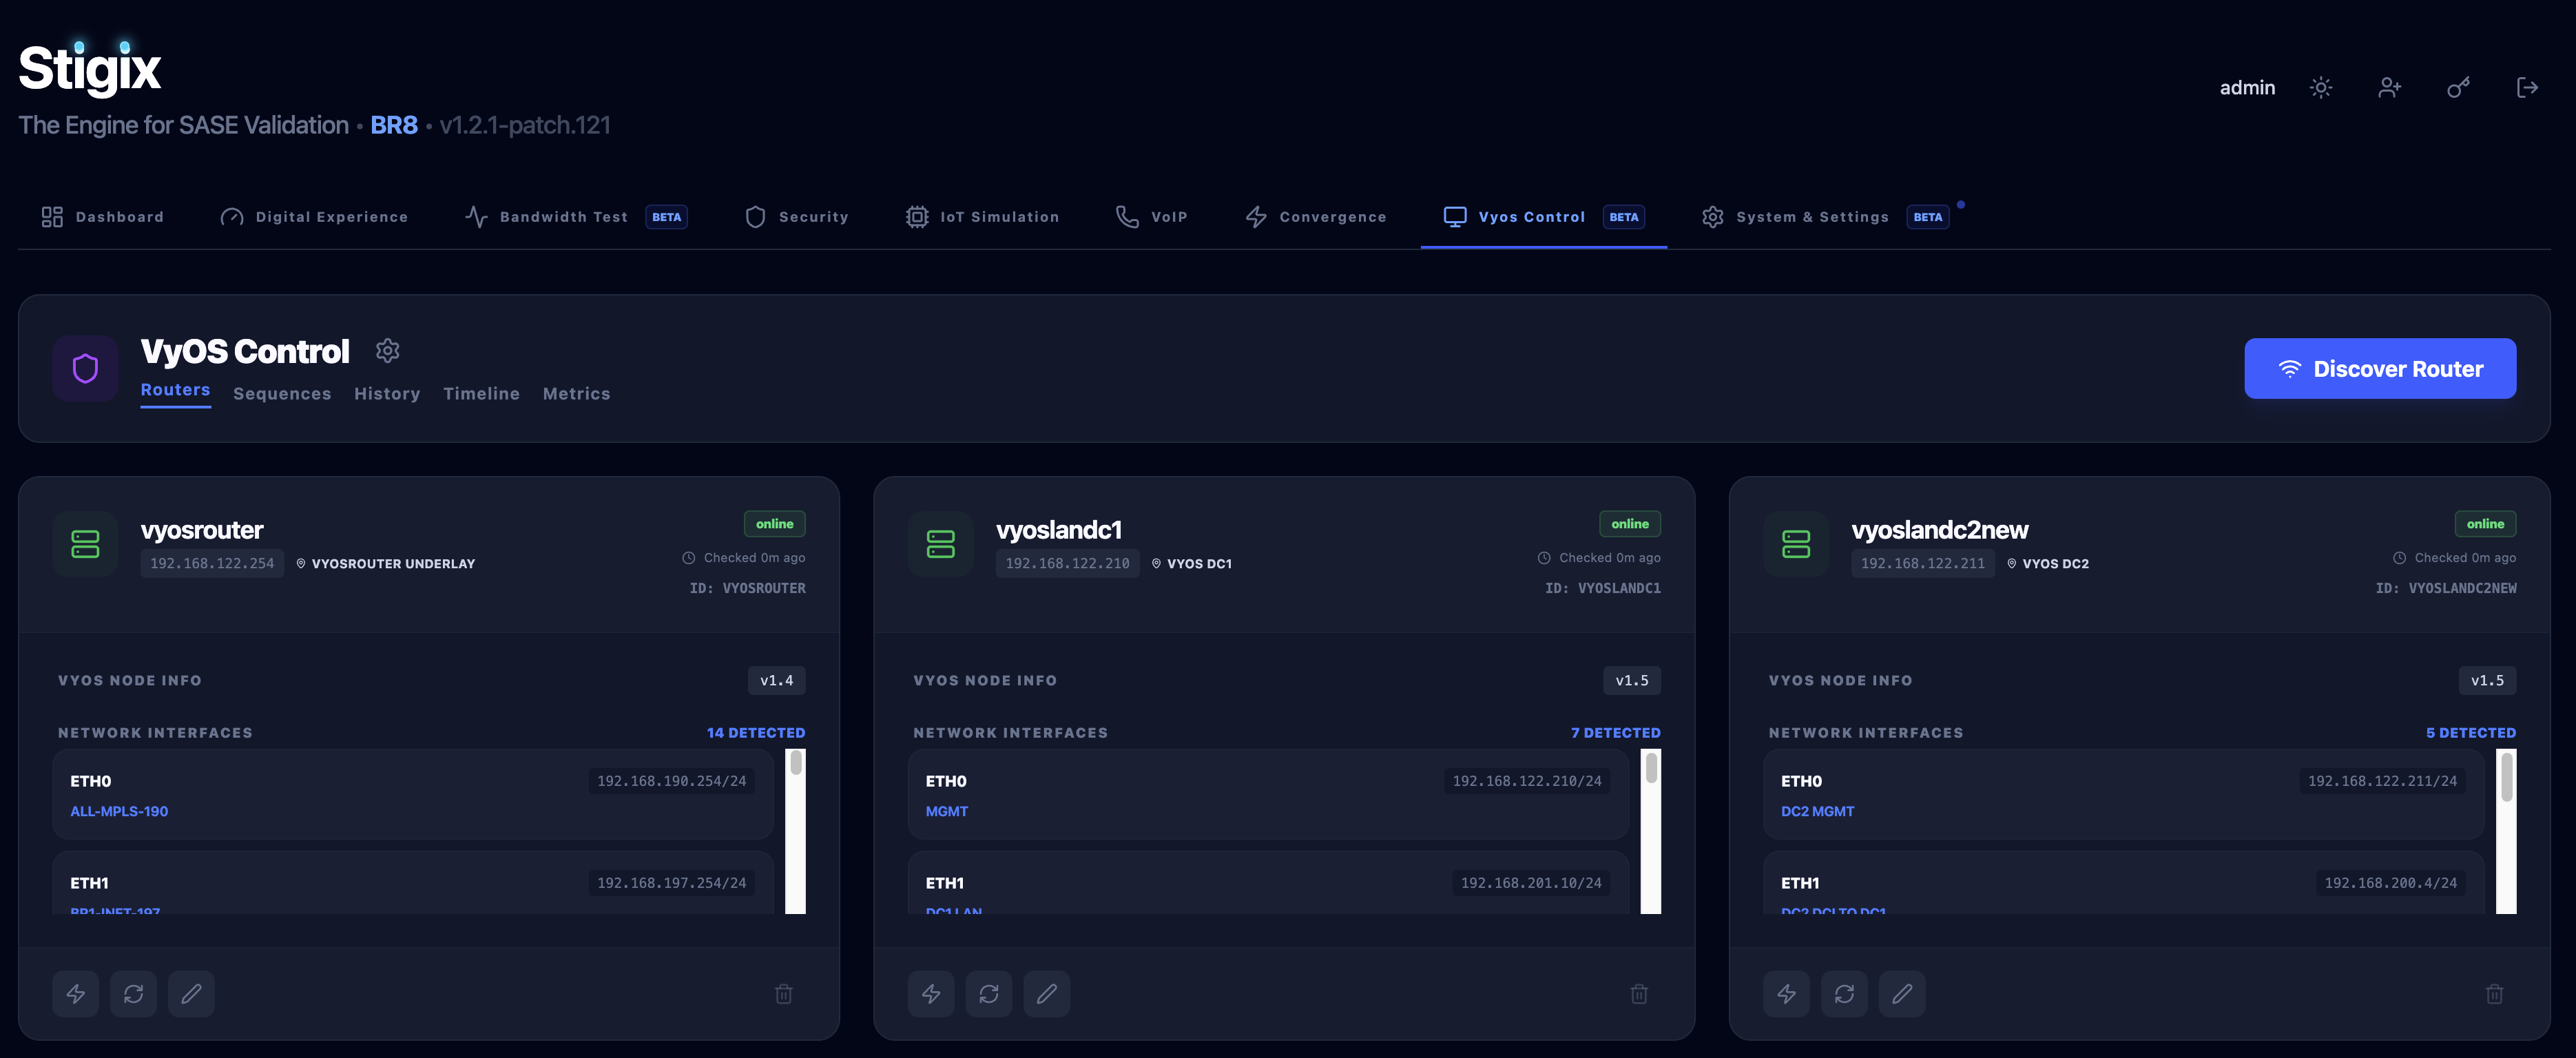
VyOS Control
orchestration · chaos
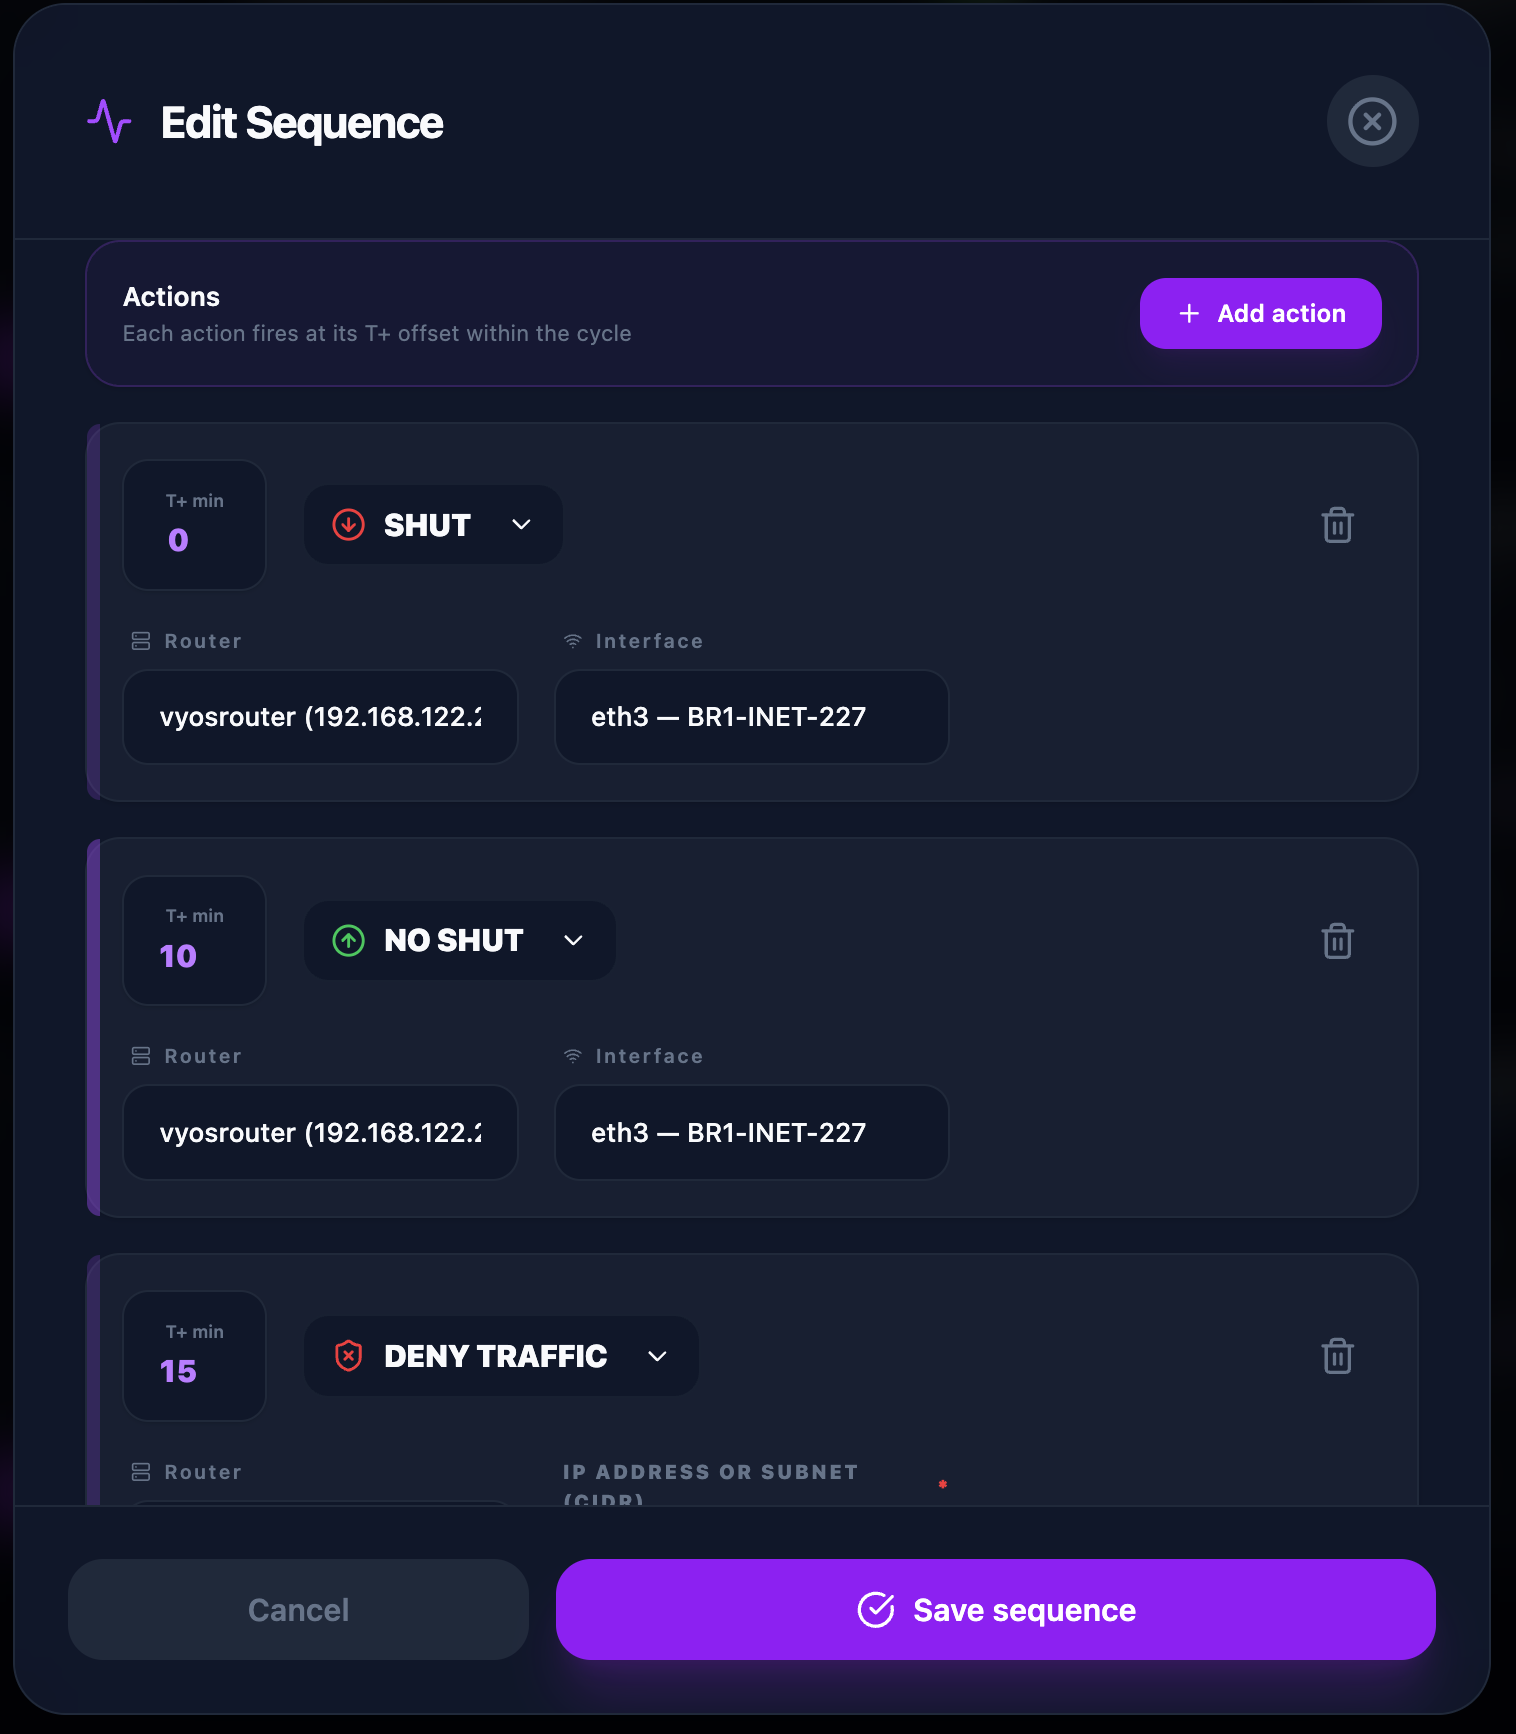
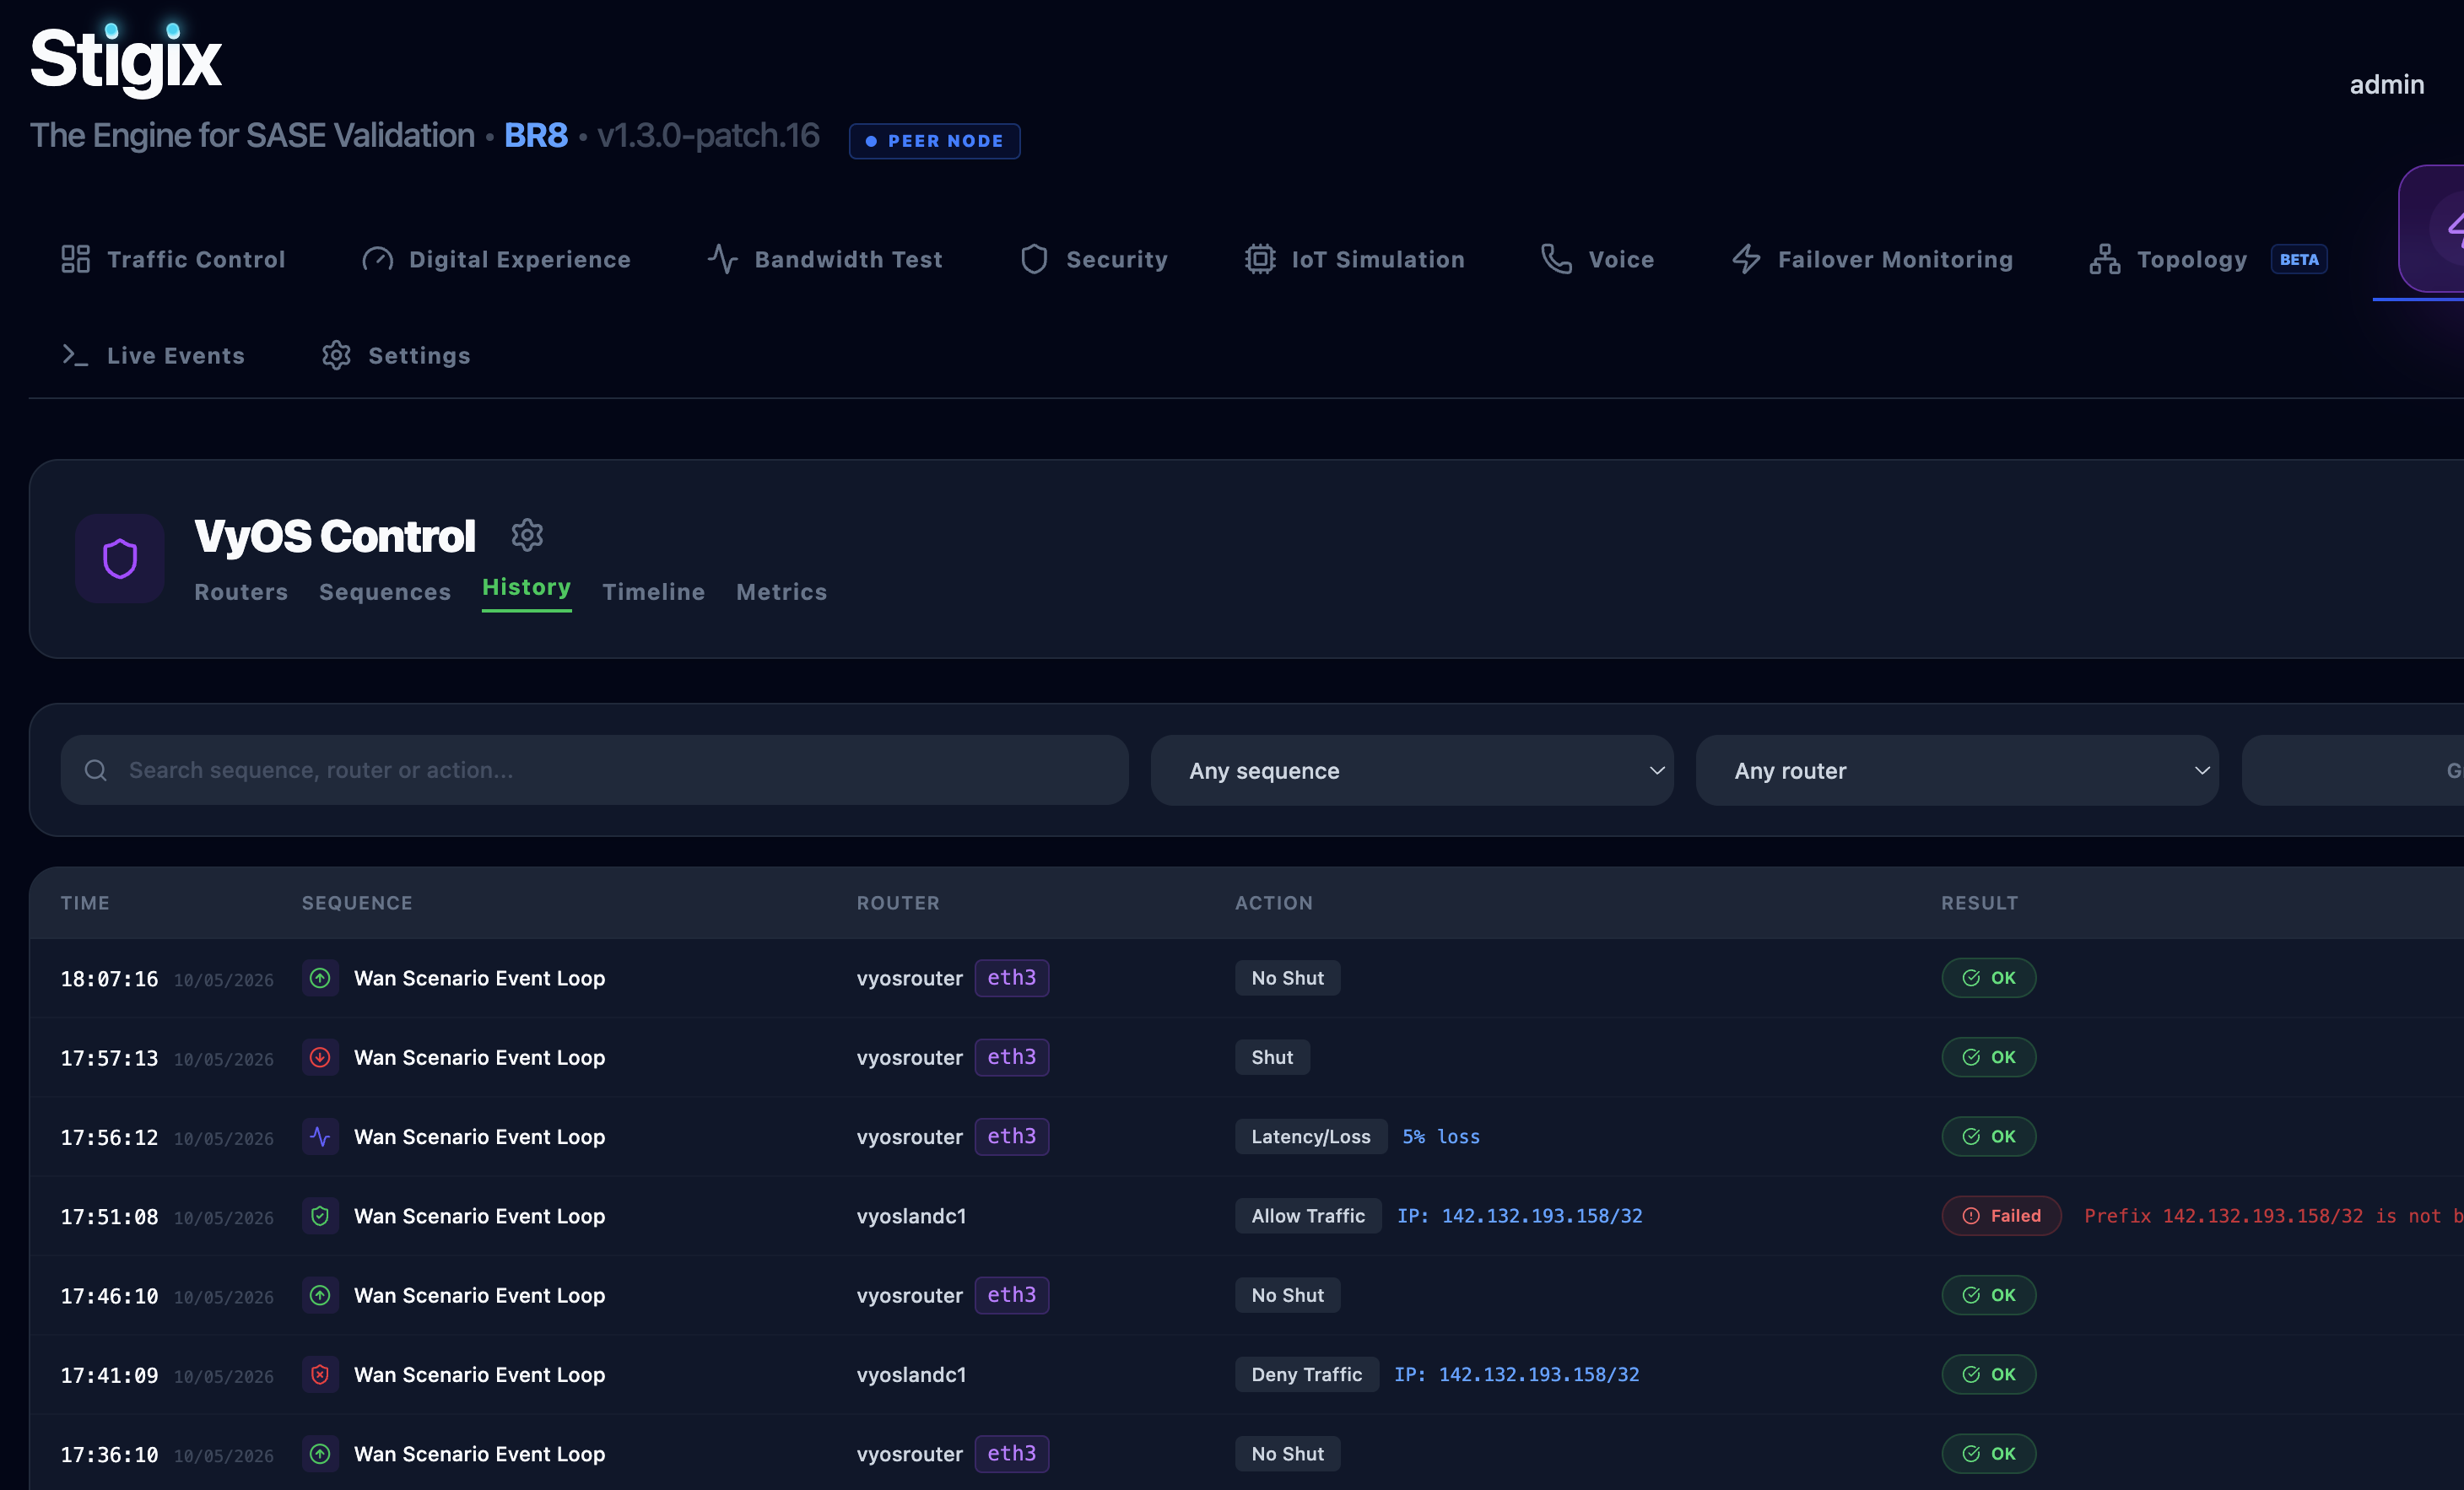
Orchestrate network impairments on VyOS routers via the VyOS API. Execute direct actions from the Topology canvas or schedule multi-step automated sequences. Inject latency, packet loss, rate-limiting, and IP blocking on demand with persistent audit history.
VyOS API Direct Topology Latency Loss Sequences
Stigix CLI
operations
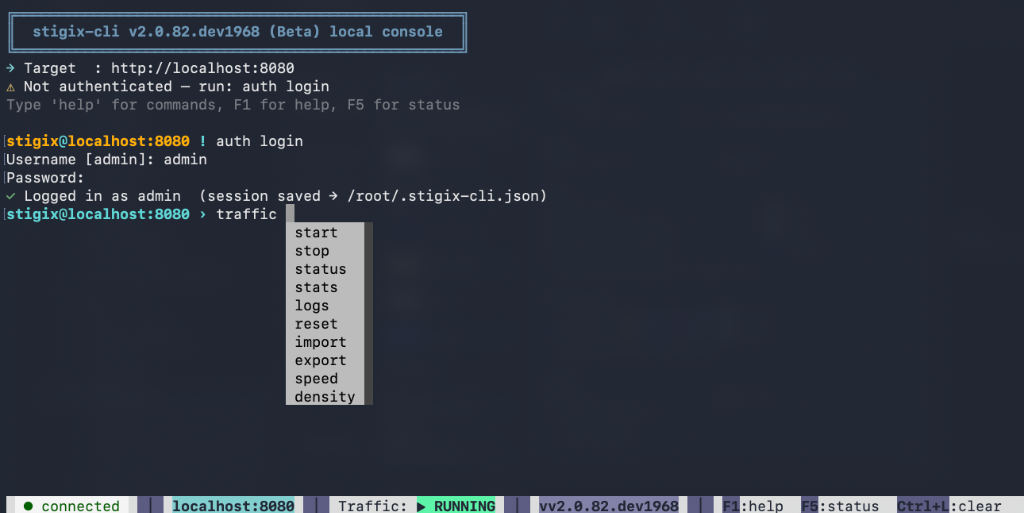
Interactive terminal console built into the container. Supports auth login, status, tcp-app, provision, and controller. Persistent command history file for scripting and audit. Tab-completion for all parameters.
Interactive tcp-app provision controller Tab-complete
MCP Server & Reports
operations · AI · reporting
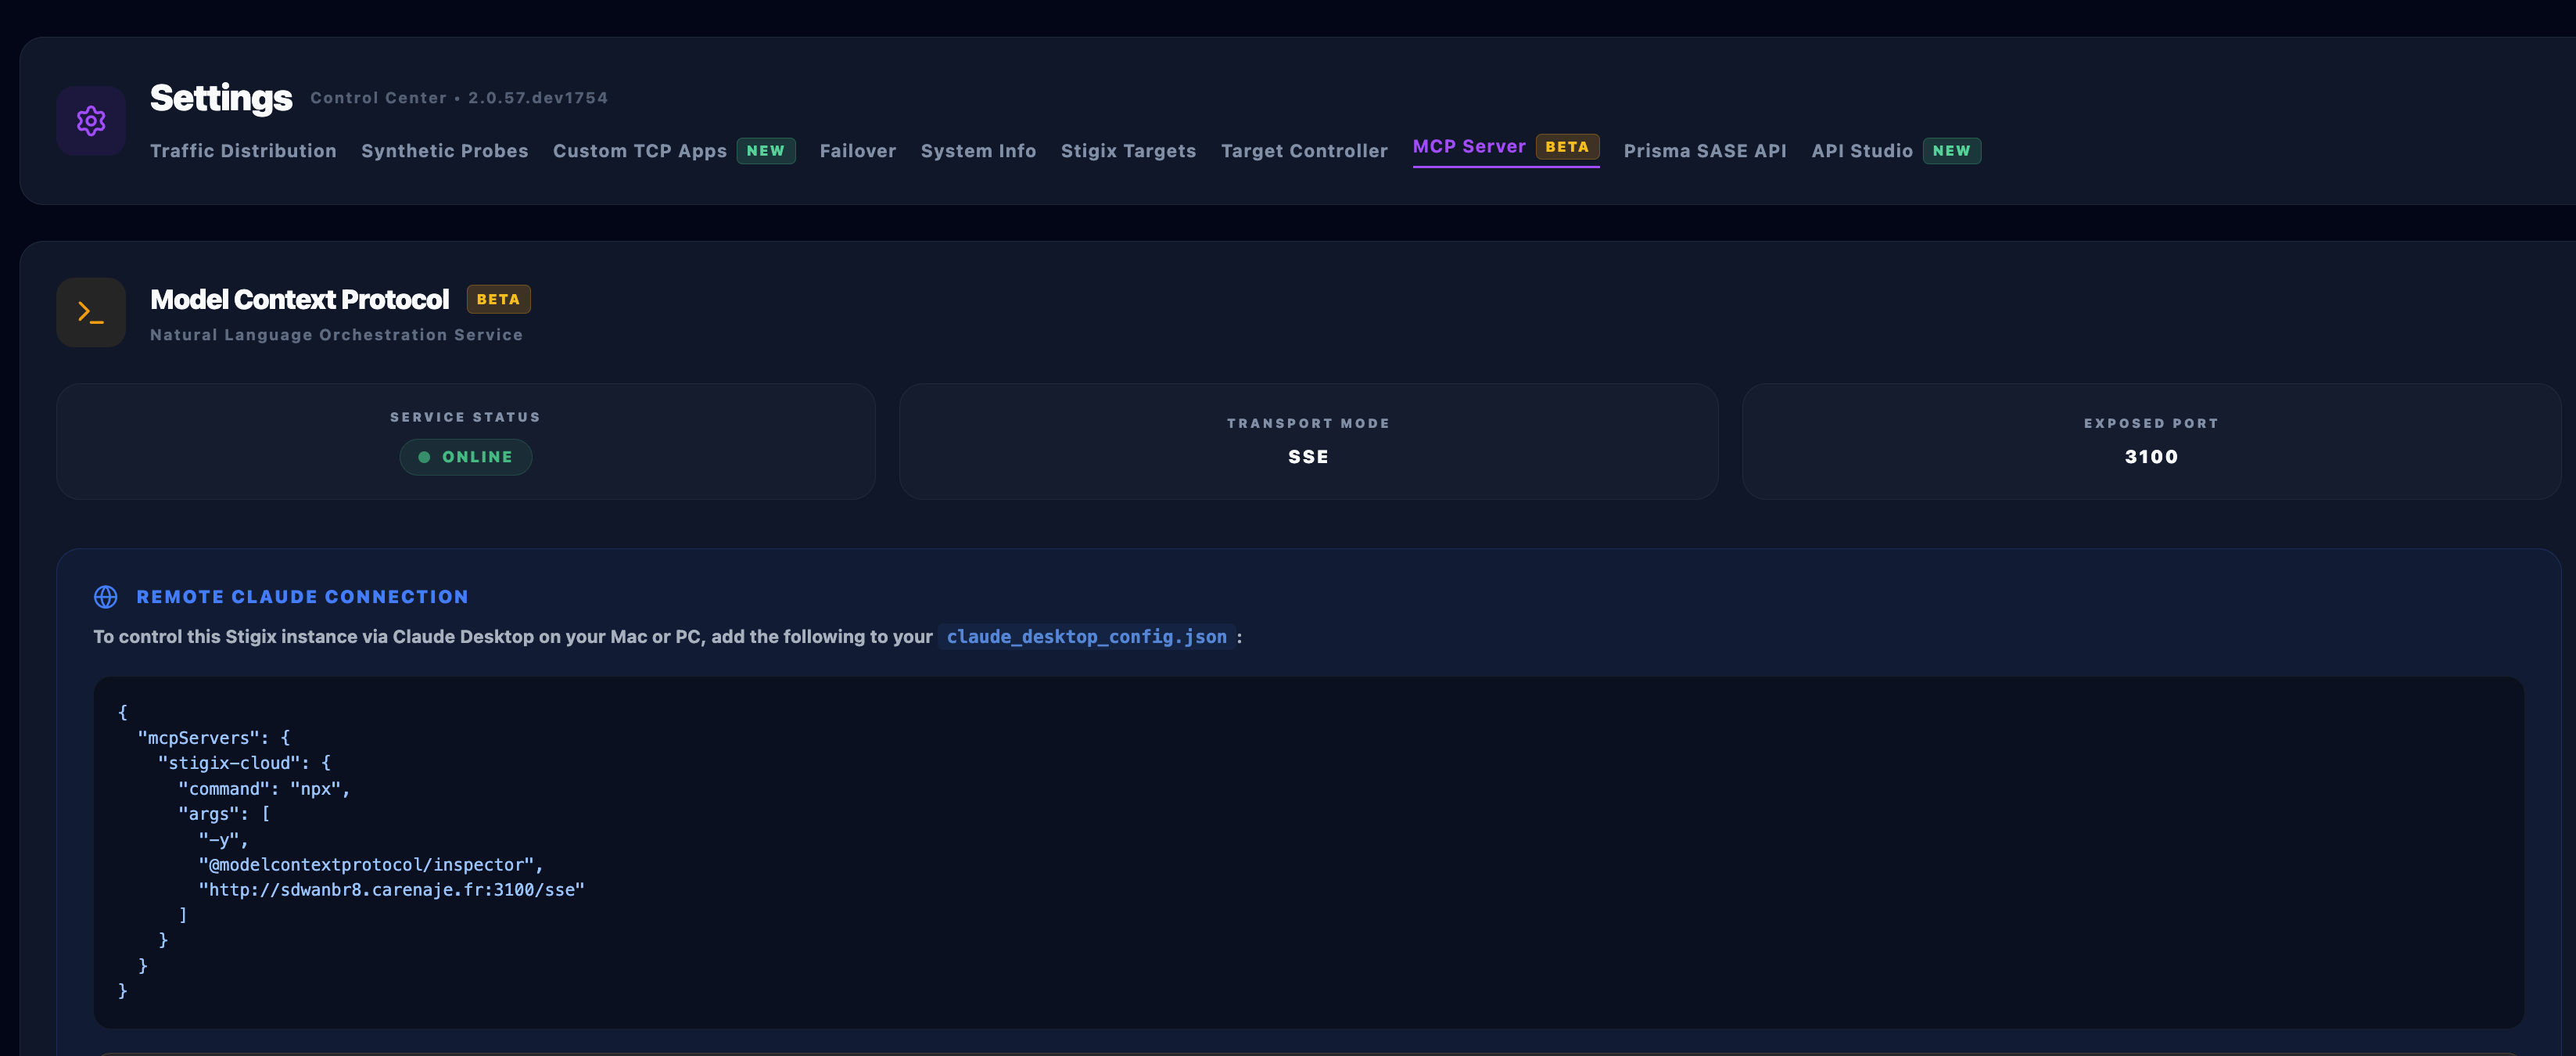
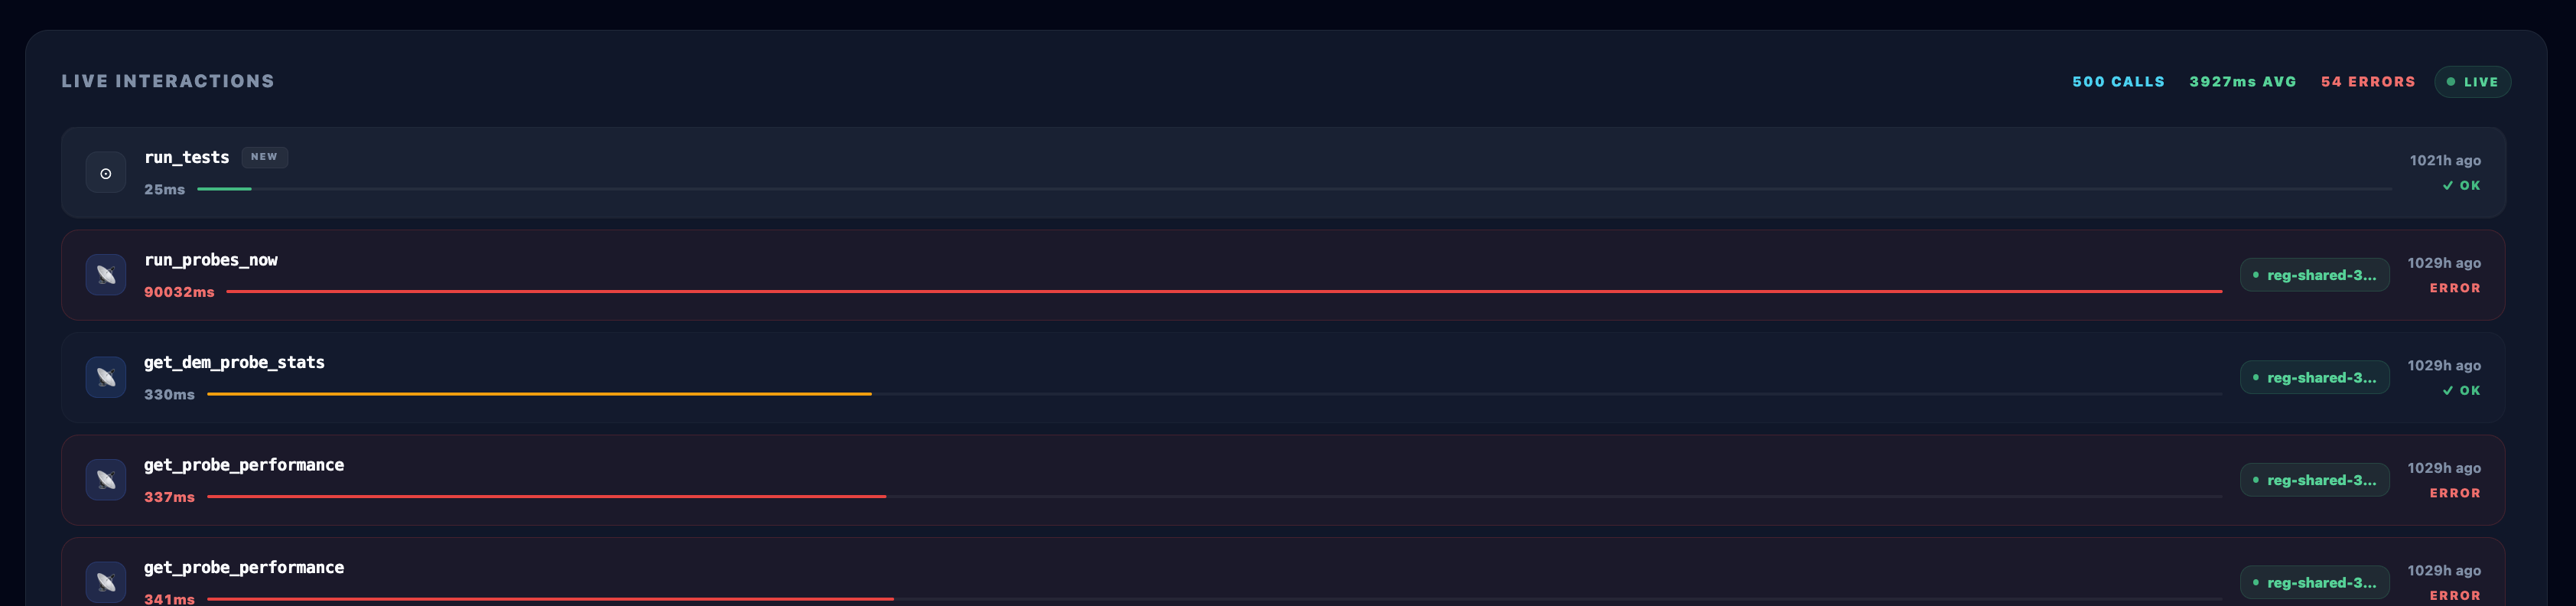
Model Context Protocol (FastMCP) server exposing 79 automated network and security diagnostic tools to AI engines (Claude Desktop). Enables autonomous end-to-end SD-WAN failover analysis, DEM latency investigations, security posture diffs, and the automated generation of executive whitepapers and technical audit reports (PDF / DOCX / Markdown) — Browse Sample Reports →
FastMCP (79 tools) Sample Reports → Whitepapers Claude Desktop SSE (3100)
Fleet Gateway & Remote View
multi-site · control plane
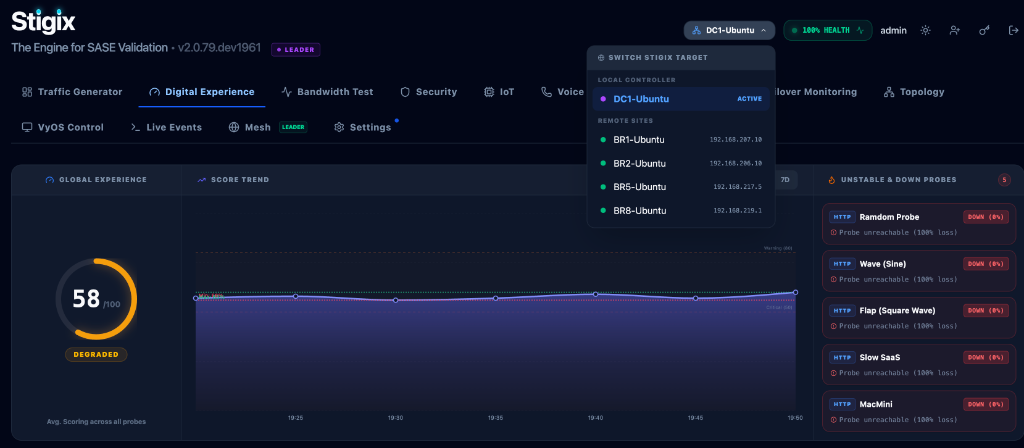
Centralized single-pane-of-glass observability and control across all distributed edge nodes directly from the Leader dashboard. Multiplexes API traffic over persistent WebSocket reverse tunnels (traversing NAT/CGNAT/firewalls with zero inbound ports) and Leader outbound dialing for external Cloud VMs (Hetzner, AWS, Home LAN) with instant bidirectional provisioning push/pull.
Single Pane of Glass WebSocket Reverse Tunnel Context Switcher Zero-Inbound Multi-Cloud Global Provisioning

Applications & Workflows

What engineers use Stigix for

01

SD-WAN Policy & SLA Steering Validation

Generate weighted SaaS and line-of-business traffic across specific interfaces and verify that application steering rules behave as intended. Confirm that video, voice, and critical SaaS flows follow the expected path based on policy — before and after configuration changes.
02

East-West Custom Application Emulation

Replicate line-of-business ERP (SAP/Oracle), POS checkout systems, database replication, and industrial SCADA protocols across SD-WAN overlays. Inject realistic server processing latencies, socket resets, and application-level errors to observe and validate dynamic path selection under real application stress.
03

Zero-Touch Multi-Branch Lab Automation

Deploy and centrally orchestrate a multi-site SD-WAN testbed across 10+ branch locations from a single Leader node. Onboard remote Linux boxes in 30 seconds with 1-line curl commands, and distribute standardized test suites, custom applications, and security policies across the entire mesh with Global Provisioning.

04

Chaos Engineering & Dynamic SLA Failover

Inject deterministic or looping application degradations (e.g. alternating 60s normal phase with 60s slow 1500ms latency or packet drops) to force SD-WAN controllers to trigger application-aware SLA failovers. Measure failover times with microsecond-accurate UDP probes without physical cable pulling.

05

Underlay vs. Overlay Root-Cause Correlation

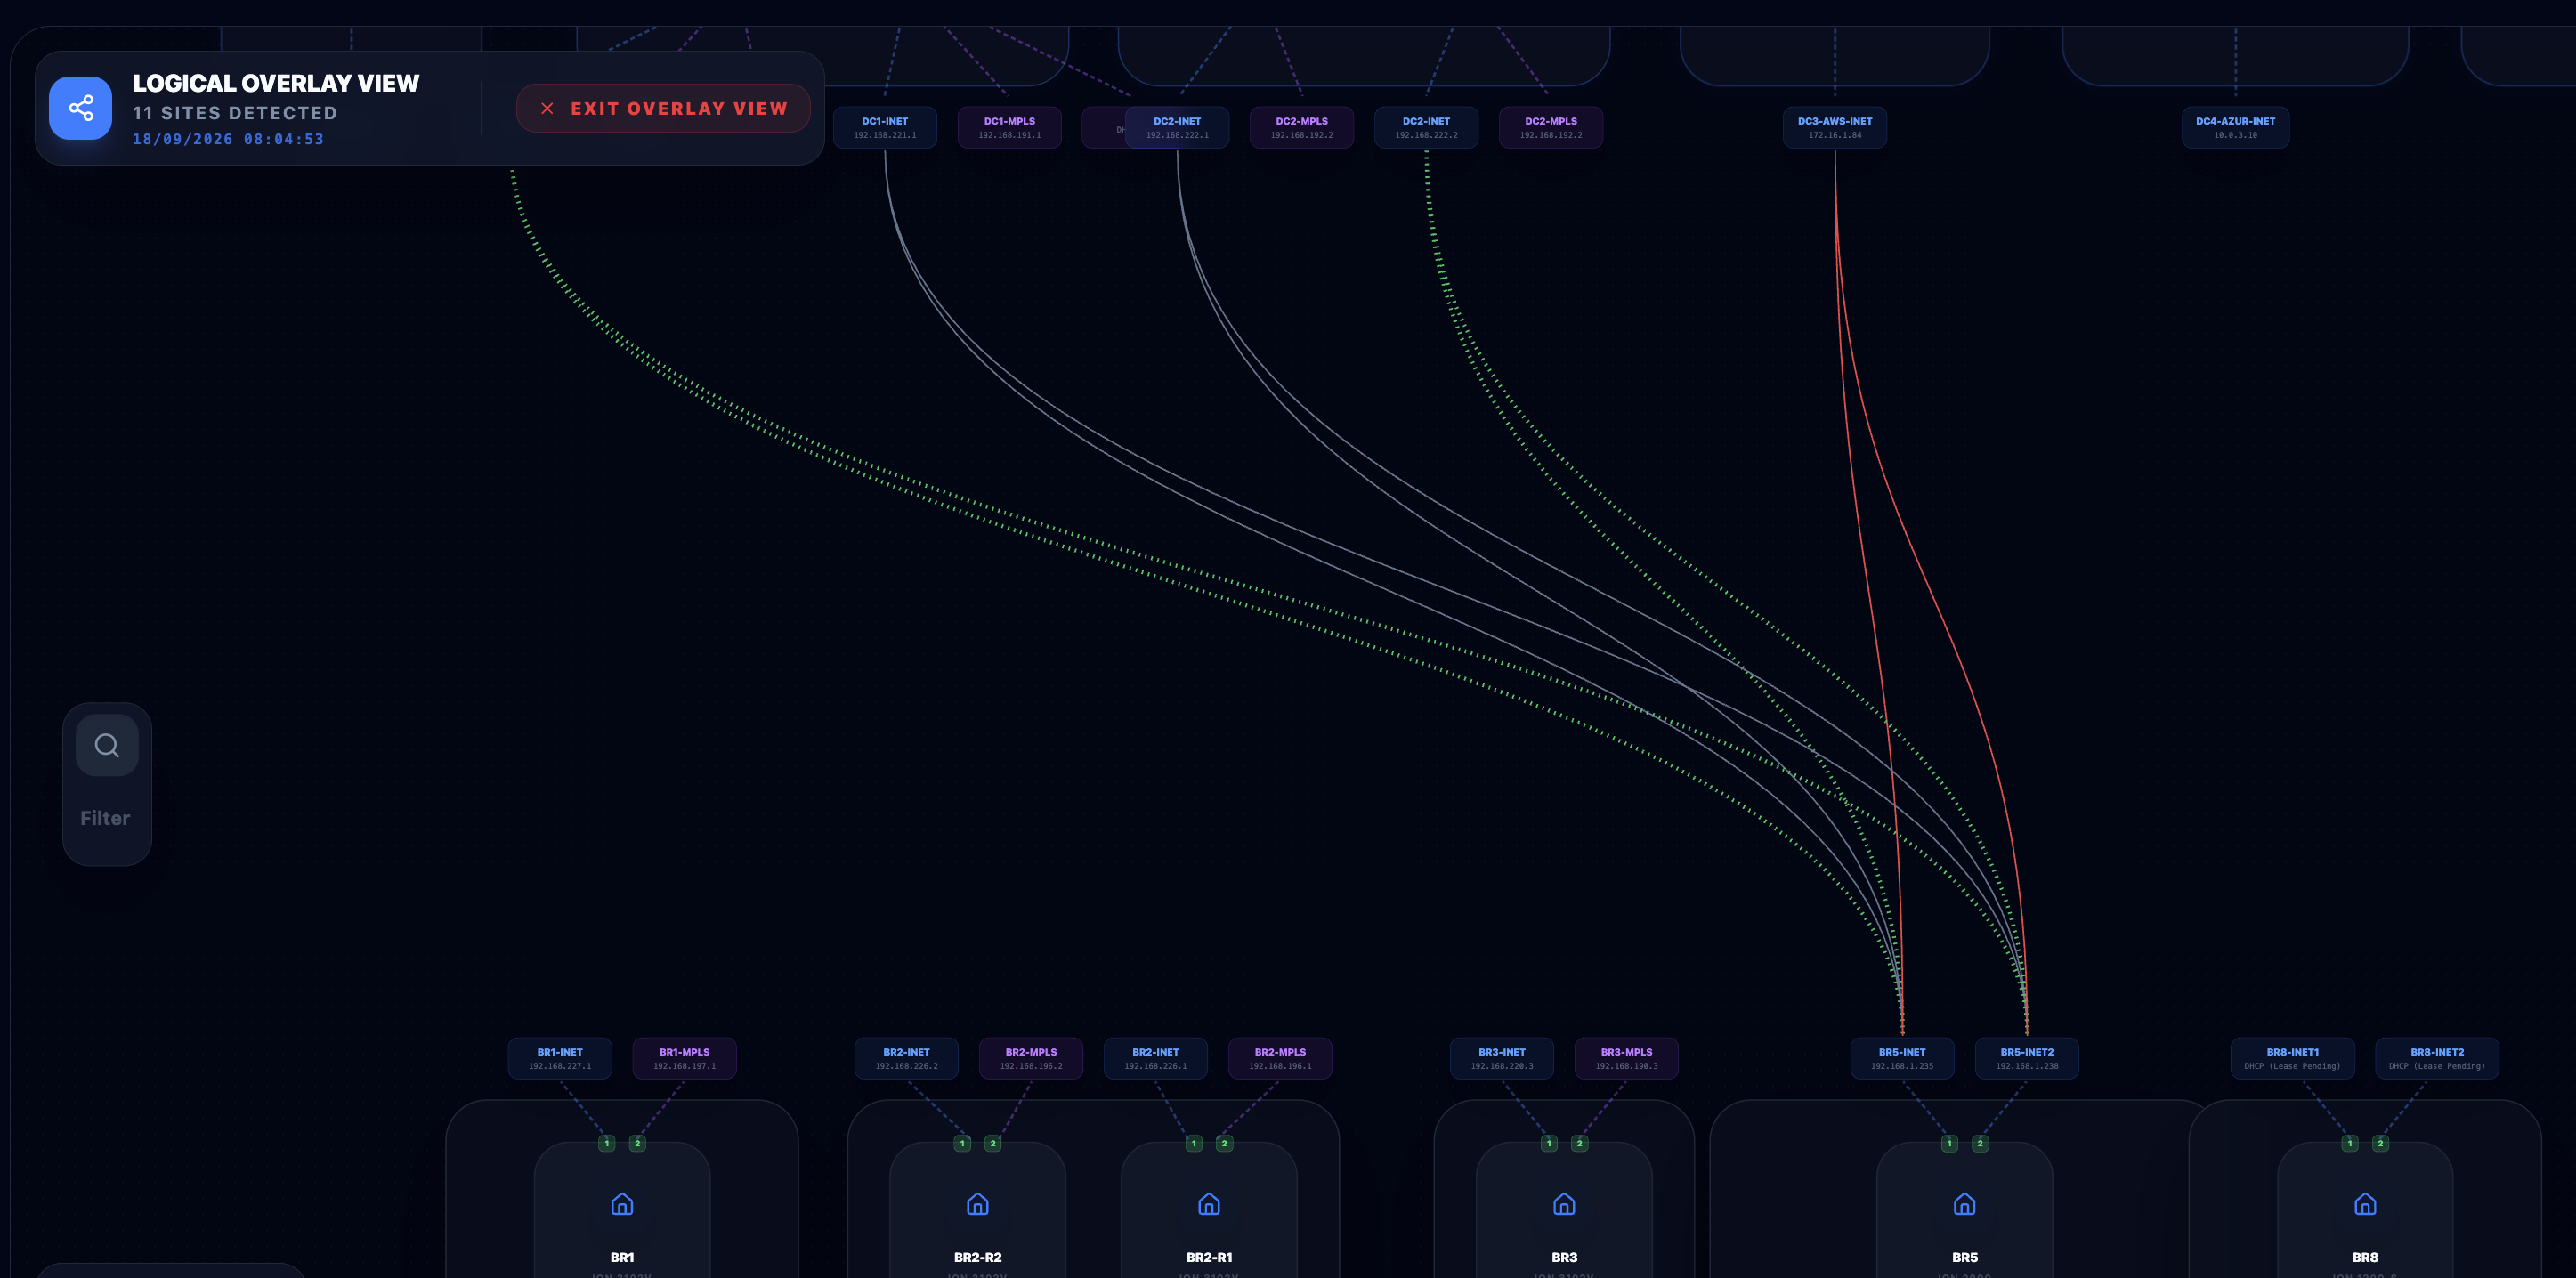
Visually compare logical SD-WAN overlay tunnels (Active/Backup/Down) with physical VyOS router chassis ports. Trace packet paths, compare transit subnets and circuit IDs with one click, and pinpoint whether an application outage originates from an underlay link impairment or an overlay policy misconfiguration.

06

Security Policy & Threat Testing

Validate URL filtering categories, DNS security, and IPS policies against real test destinations. Run scheduled security test cycles and capture results persistently. Confirm that blocking and alerting rules fire correctly before go-live or after a policy change.

07

IoT Micro-Segmentation & Attack Simulation

Simulate realistic IoT device presence at Layer 2/3 and validate that DHCP profiling, micro-segmentation, and traffic classification work correctly. Test threat prevention detection against active IoT attack vectors (DNS Flood, C2 Beacon, Port Scan, Data Exfiltration).

08

Voice QoS & Sub-Second Failover Timing

Measure exact tunnel transition times during link failure or SD-WAN path change events. Use VyOS network impairment orchestration to induce failures on demand and capture convergence timing with high-precision UDP probes at up to 1000 PPS alongside RTP voice simulation and MOS scoring.

09

AI Security Validation BETA

Simulate DLP exfiltration, Prompt Injection, exploit attempts, and EICAR uploads against live AI platforms (ChatGPT, Grok, Gemini, Perplexity). Validate that AI Security policies detect and block sensitive data leaving through AI chat interfaces — a rapidly growing attack vector in enterprise environments.

10

Demo & Presales POC Enrichment

Build repeatable, visually compelling demo environments for customer presentations and partner enablement sessions. Feed SASE and SD-WAN dashboards with realistic multi-application traffic and security event telemetry without requiring access to production environments.


Research & Engineering Benchmarks

Technical Whitepapers & Lab Studies Powered by Stigix

Real-world SASE & SD-WAN validation studies produced from live lab scenarios orchestrated by Stigix and analyzed with AI assistants via FastMCP.

Browse All Reports (9) →
White Paper 2026-09-25

When Routing Can't See the Failure

How Prisma SD-WAN and Stigix demonstrated automatic failover in ~3 minutes during a silent internet breakout failure where Layer 3 BFD keepalives remained completely blind.

  • Automatic ~3 min failover during dead breakout behind active next-hop
  • End-to-end TCP session tracking vs blind Layer 3 tunnel keepalives
  • Continuous probe-driven failback once primary DC breakout is repaired
White Paper 2026-09-26

Beyond Ping: App vs Network Latency

Architectural deep-dive decomposing end-to-end user latency into Network RTT and Server Response Time (SRT) without agents or SSL decryption using dual synchronized telemetry.

  • 5.8 ms Network RTT vs 800 ms Server Response Time (SRT) clear isolation
  • Eliminates the "Is it the network?" blame game in minutes
  • Non-intrusive dual measurement with Stigix and Prisma SD-WAN SCM
Lab Benchmark 2026-09-24

SD-WAN Multi-Circuit Failover Audit

Live failover benchmark between branch office BR8 and datacenter DC1 measuring sub-second packet loss and active path evolution during induced WAN circuit impairments.

  • Sub-second packet loss measurement during active link disruption
  • Path evolution telemetry: BR8-INET2 → DC1-INET → BR8-INET1
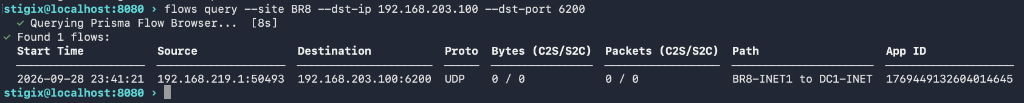
  • Full flow session continuity audit with 79 MCP diagnostic tools
AI-Assisted Lab Orchestration & Reporting Stigix exposes 79 network diagnostic and chaos impairment tools over FastMCP — enabling AI engines (like Claude Desktop) to autonomously execute test plans, analyze convergence curves, and draft executive-ready reports.
View All Sample Reports →

Installation & Deployment

Up and running in under 60 seconds

ⓘ Prerequisite Docker must be installed and running on your host. No other dependency required.  Install Docker →
bash — stigix deployment
# 1. Standalone / Leader Node Deployment
$ curl -sSL https://raw.githubusercontent.com/jsuzanne/stigix/main/install.sh | bash
🚀 Stigix (All-in-One) — Starting Leader services...
✅ Dashboard active → http://localhost:8080
# 2. Zero-Touch Remote Branch Peer Onboarding (Points to Leader)
$ curl -fsSL https://raw.githubusercontent.com/jsuzanne/stigix/main/install.sh | sudo bash -s -- --controller http://192.168.203.100:8080
✅ Registered to Leader [192.168.203.100:8080]. Direct Mode active.
✅ Pulling Central Global Provisioning bundles (rev-1.json)...
# 3. Manual Compose Install
$ mkdir -p stigix && cd stigix && curl -sSL -o docker-compose.yml https://raw.githubusercontent.com/jsuzanne/stigix/main/docker-compose.yml && docker compose up -d
⚡
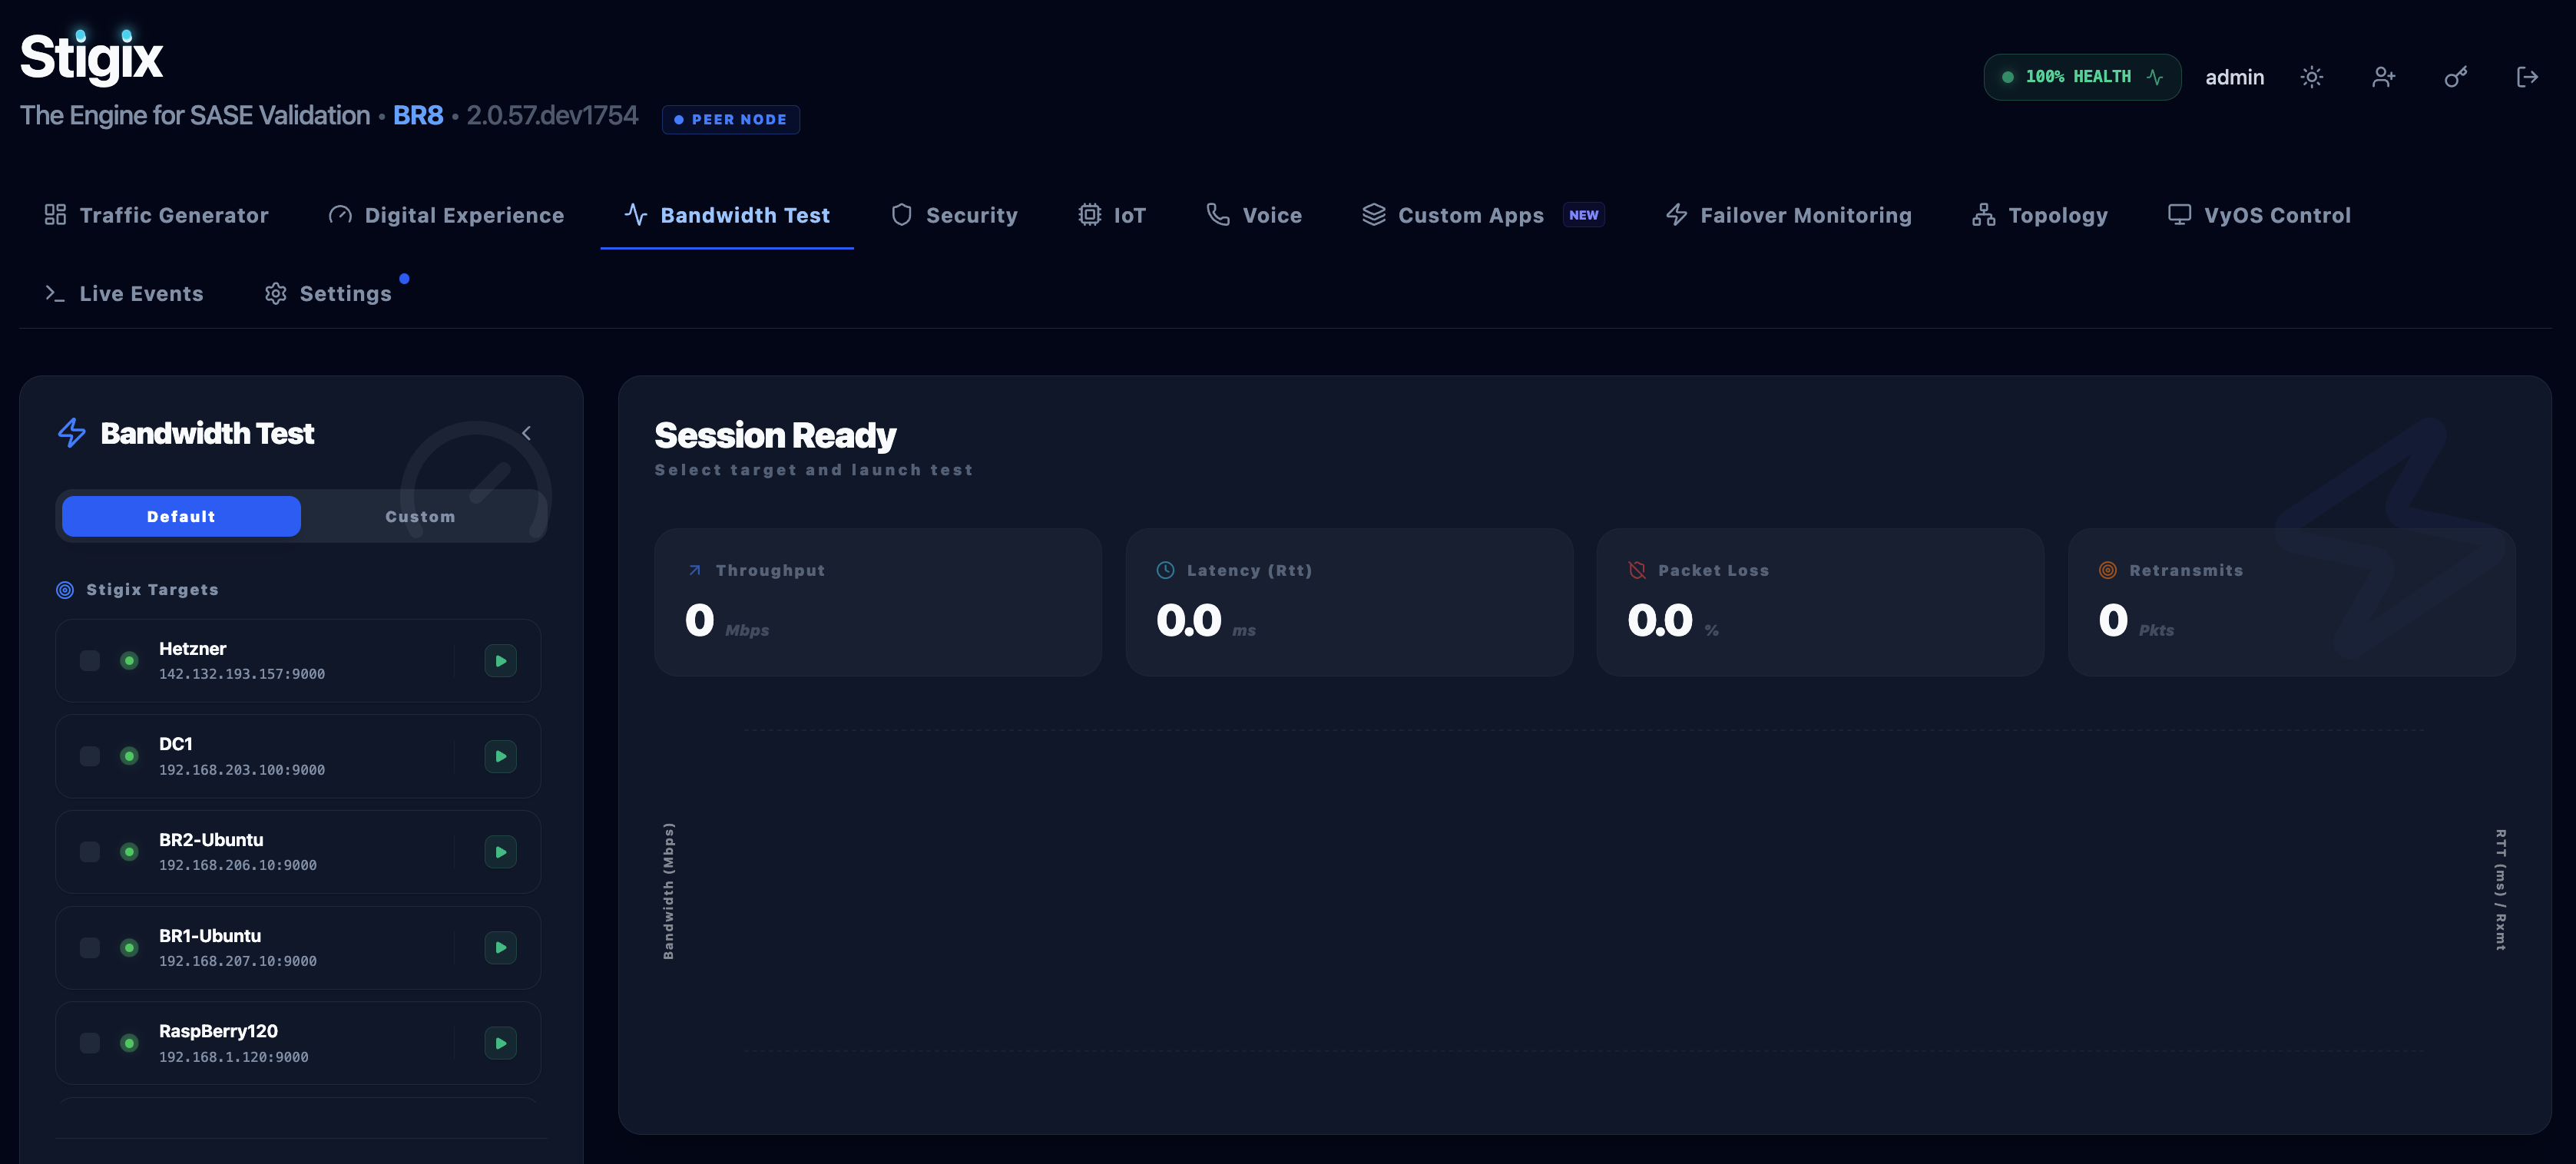
Distributed Mesh: Every Stigix instance is both a Sender and a Responder. Once deployed, the instance immediately starts generating traffic and listening as a custom TCP application server, HTTP echo, bandwidth speedtest, voice echo, and SLA probe target. Deploy on a branch node, a hub, or a cloud VM: all instances are auto-discovered and synchronized via the Central Global Provisioning engine.
Linux
Docker Engine · x86 / ARM64 servers, VMs, Raspberry Pi, or any Docker-capable appliance — including routers, switches, and access points that support container workloads. Host network mode for full Layer-2/3.
macOS
Docker Desktop / OrbStack · macOS 11+. Bridge mode. Some Layer-2 constraints apply.
Windows
Docker Desktop + WSL 2 · Windows Install Guide — full Docker container support.

Operations & Automation

Control and verify with the built-in CLI

Stigix ships a fully interactive terminal console inside the container with support for Custom Apps, Global Provisioning, DEM probes, and Controller mesh management.

stigix-cli — interactive console
# Launch the interactive console
$ docker exec -it stigix stigix-cli
stigix@localhost:8080 › tcp-app status erp-8443
━━ Application: ERP-Production (:8443) ━━━━━━━━━━
✓ Listener [LISTENING] (mode: fixed_delay 150ms)
✓ Outbound [RUNNING] (2 streams to DC1)
→ Health 98/100 [OPTIMAL] (p50: 16.2ms · p95: 24.1ms)
stigix@localhost:8080 › provision publish custom-tcp-apps
✓ Published custom-tcp-apps bundle rev-4 (diff: +1 app ~2 peers)
stigix@localhost:8080 › controller peers
→ BR1 (192.168.101.50) · BR2 (192.168.102.50) · DC1 (192.168.203.100)
🖥️
Scripting & CI/CD Pipelines: Execute non-interactive commands in batch or CI/CD pipelines with stigix-cli --exec "<command>". Full command history is saved to JSON for auditability and compliance.

Resources

Documentation & Guides